TL;DR: what autonomous pentesting is going to absorb
- Traditional vulnerability management, specifically the signature-and-version detection layer that ships hypotheses and calls them findings.
- BAS, a bridge category built for a world where real exploitation was too expensive to run continuously.
- Chunks of cloud security posture, because the exploit graph does natively what CSPM has been approximating from configuration metadata.
I have watched the security industry run a very profitable game with abbreviations for the last decade. The simple way to do it is to invent a category, give it a cool catchy abbreviation, market it as the missing piece of the stack, and repeat. The greatest examples are CTEM, BAS, ASM, and EASM.
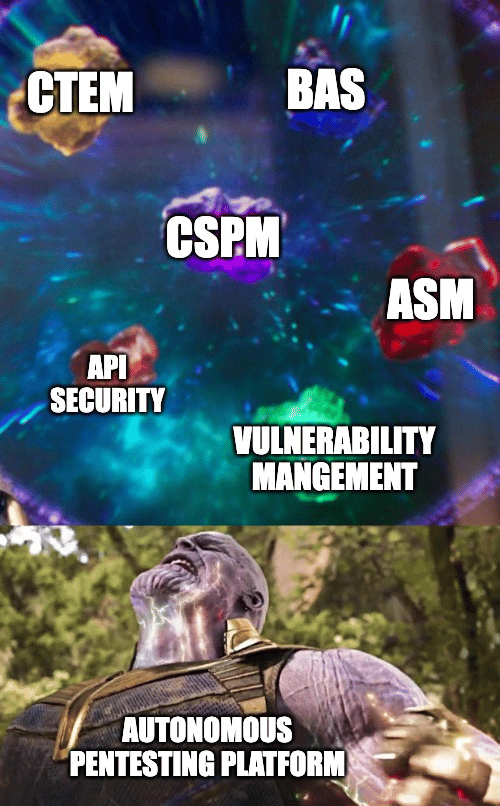
Every one of them arrived promising to close the gap the last one left open, and every one of them ended up as a line item on a renewal spreadsheet that nobody at the buyer‘s side could confidently defend. That model worked well when buyers had the budget and patience. In my experience, both are gone now.
The pattern that follows is boringly consistent, and I have watched it play out three or four times since Astra became part of the security industry. A cluster of adjacent point tools solves overlapping problems poorly, a new category shows up with a genuinely different primitive, and the surrounding letters either get acquired or quietly disappear from the market.
A few of the cleanest cases:
- Antivirus grew into EDR, which further grew into XDR.
- Standalone SWG, CASB, ZTNA, and FWaaS were reorganized under SASE.
- CSPM, CWPP, and CIEM got rolled up into CNAPP.
My read is that the market forced each collapse because vendors had already been walking into each other’s territory for years, fishing buyers from adjacent categories only to earn a defensible USP and pitch a better ROI.
Autonomous pentesting platforms are about to trigger more abbreviation collapse than the industry has ever seen, and I am happy Astra is delivering value through it as one of the pioneers in this space. Autonomous pentesting goes beyond the pattern of adjacent creep, because it rewrites what a finding actually is.
Autonomous pentesting uses context as its core primitive and makes it inexpensive to acquire. That makes me 200 percent sure the same foundation will carry it into API and cloud security. When one tool tests all of these surfaces and carries that context into every subsequent scan, buyers will accept some vendor lock-in in exchange for a unified view of security. The result of this category creation is a rampant collapse of abbreviation into features.
Now, why should you believe any of this? And how am I sure this isn’t another bold prediction? The numbers already agree with me. The broader pentesting market is projected to grow from USD 2.36 billion in 2025 to USD 5.54 billion by 2031 at a 15.29 % CAGR, and the autonomous slice inside it is compounding at a stated 42.3% CAGR through 2034. Categories do not grow at 42% without eating the categories next to them. Gartner says 75% of organizations are actively pursuing vendor consolidation, up from 29% in 2022.
Translation: buyers are done paying twelve vendors to describe the same problem in twelve dialects.
My gut says that by the end of 2027, I expect at least one of the top-five VM incumbents to either get acquired by an autonomous pentesting platform or ship one themselves through acquisition or an in-house build.
The winners of this cycle will be the platforms that own the validated exploit graph, because that graph is the substrate that VM, BAS, and ASM have all been approximating from different angles. And once a category becomes an input, it is only a matter of time before it becomes a feature.