Trust used to be a handshake.
Then companies started sharing infrastructure, data, and each other's blast radius.
A handshake stopped being enough.
Explore what we do

Continuous pentesting that actually
fixes your code
Astra Security is a G2 Pentest Leader, combining autonomous AI-powered
testing with expert-led pentesting, built toward a single goal: making software self-healing. Most pentests end in a
PDF nobody reads. Astra's ends in a fix your developers actually ship.
Autonomous + human-led
AI-powered testing + PTaaS in one workflow
DAST + Cloud + API
Vulnerability scanning across
your stack
CREST-accredited
Trusted by 1,000+ businesses
Good security shouldn't be a privilege.
It should be a given.
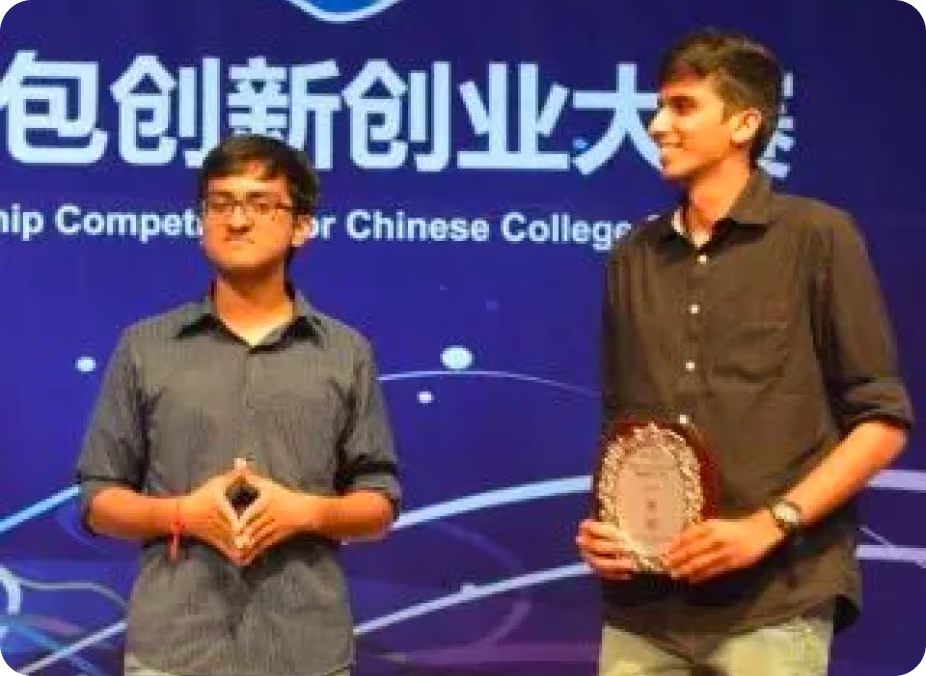
Ananda and Shikhil met as engineering students, drawn to the same problem: how systems break, and why nobody notices until it's too late. That curiosity turned into a career and then a company (and if we're being honest, most of their personality).
Long before Astra existed, both spent years uncovering flaws in the products of some of the world's largest companies, teaching them something enterprises would later confirm themselves: real security testing was rare, expensive, and reserved for a handful of companies who can afford genuine depth.
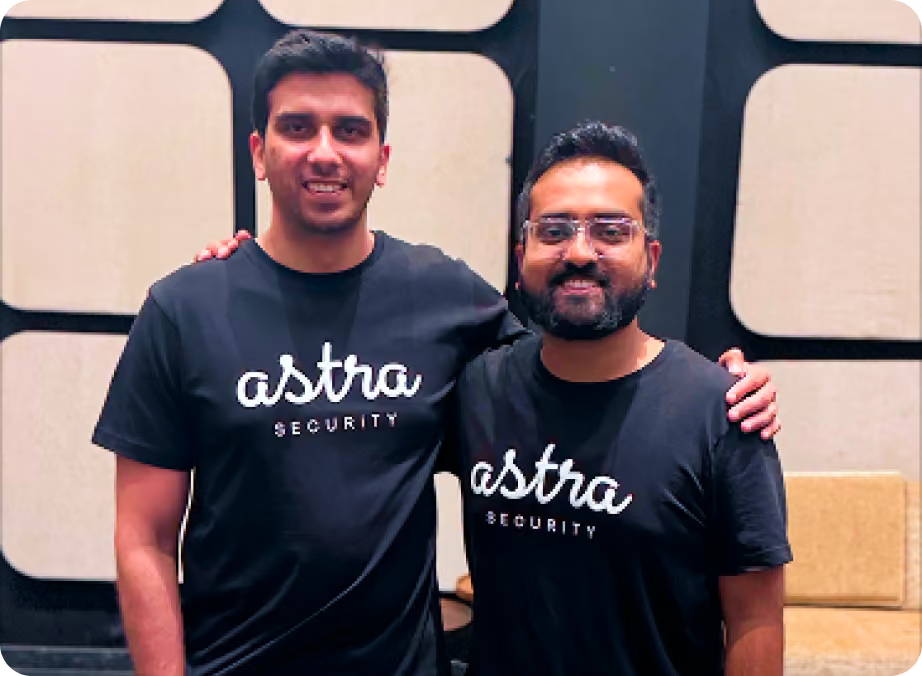
They wanted every engineering team to have access to the same depth, irrespective of their size or budget, so they built it themselves, starting with a handful of clients who took a chance on two people with more conviction than they had headcount.
That conviction is now a team of certified pentesters, researchers, and engineers, serving 1000+ businesses across industries and continents. Astra was born from a simple bet: good security testing should be judged by results and backed by real proof.
Since then, we've grown. A lot.
With offices in the USA and Bangalore, and a team of 100+ astranauts, we help you loop security into a living record you can put in front of a customer, an auditor, or the board and say, "See for yourself."
Our vision: Become the single source of
security trust between organizations.

Trusted by thousands, recognized
by leaders
Which means Astra is among the likes of Sendgrid, Twilio, Uber, DigitalOcean etc. We were accelerated at Techstars in Berlin.
We were awarded at the Global Conference on Cyber Security as the 'Most Innovative Security Company’ by Prime Minister of India Mr. Narendra Modi.

Astra has a grant from the French Government under their French Tech Ticket program. We were awarded by the French president Mr. François Hollande himself.

Loved by 1000+ CTOs & CISOs worldwide

We are impressed by Astra's commitment to continuous rather than sporadic testing.


Astra not only uncovers vulnerabilities proactively but has helped us move from DevOps to DevSecOps


Their website was user-friendly & their continuous vulnerability scans were a pivotal factor in our choice to partner with them.


The combination of pentesting for SOC 2 & automated scanning that integrates into our CI pipelines is a game-changer.


I like the autonomy of running and re-running tests after fixes. Astra ensures we never deploy vulnerabilities to production.


We are impressed with Astra's dashboard and its amazing ‘automated and scheduled‘ scanning capabilities. Integrating these scans into our CI/CD pipeline was a breeze and saved us a lot of time.


Overall, Astra made the penetration testing process much more manageable and helped us complete our audit requirements on time.
Working with Astra on our penetration test was a genuinely smooth experience. The findings were clear and well-documented, which made it easy for our engineers to understand the impact and prioritize fixes.
We recently engaged Astra to carry out penetration testing across several of our applications and were extremely impressed with their service.
Astra’s penetration test of our web archiving platform gave us real security results, not just a list of problems. Every finding came with clear steps to reproduce it and fix it
We are impressed by Astra's commitment to continuous rather than sporadic testing.
Astra not only uncovers vulnerabilities proactively but has helped us move from DevOps to DevSecOps
Their website was user-friendly & their continuous vulnerability scans were a pivotal factor in our choice to partner with them.
The combination of pentesting for SOC 2 & automated scanning that integrates into our CI pipelines is a game-changer.
I like the autonomy of running and re-running tests after fixes. Astra ensures we never deploy vulnerabilities to production.
We are impressed with Astra's dashboard and its amazing ‘automated and scheduled‘ scanning capabilities. Integrating these scans into our CI/CD pipeline was a breeze and saved us a lot of time.

Overall, Astra made the penetration testing process much more manageable and helped us complete our audit requirements on time.
Working with Astra on our penetration test was a genuinely smooth experience. The findings were clear and well-documented, which made it easy for our engineers to understand the impact and prioritize fixes.
We recently engaged Astra to carry out penetration testing across several of our applications and were extremely impressed with their service.
Astra’s penetration test of our web archiving platform gave us real security results, not just a list of problems. Every finding came with clear steps to reproduce it and fix it
Here's the thing about "we take security
seriously": everybody says it, very few
can prove it.
Astra Security tests your apps, APIs, and cloud the way a real attacker would, then hands you
evidence, not adjectives. Five ways, working together:
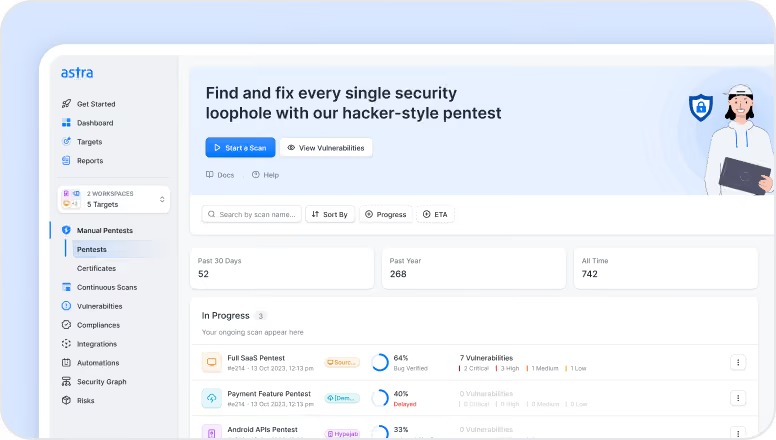
Manual Pentesting (PTaaS)
Certified humans (OSCP, CEH) thinking like attackers. The clever stuff automation walks right past.
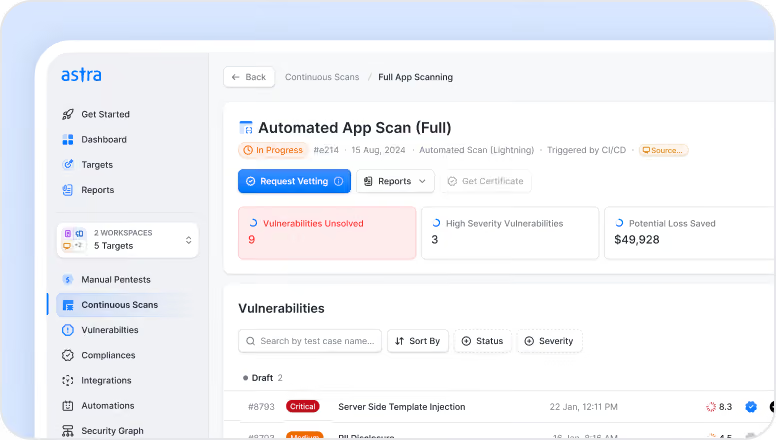
DAST Scanner
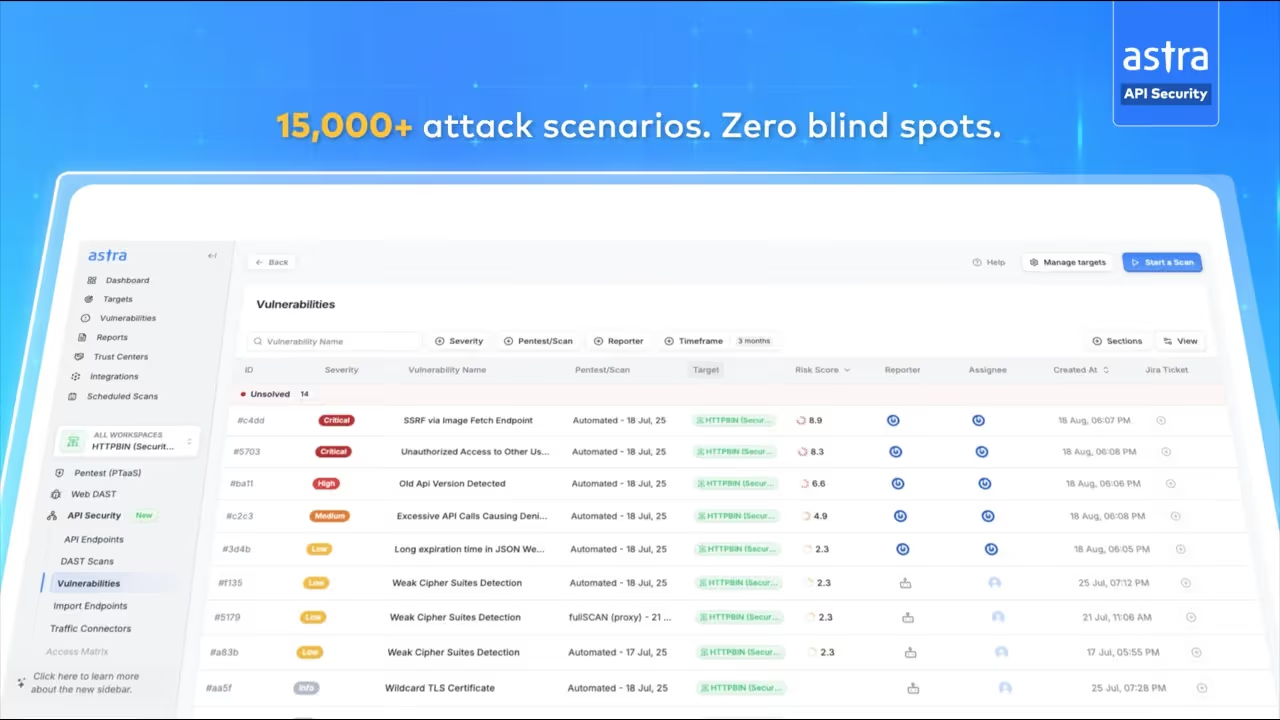
15,000+ tests running behind your login screens. Continuously, not once a year.
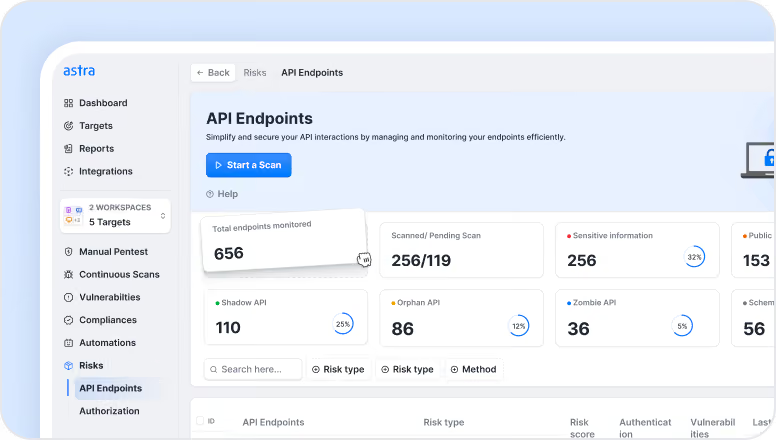
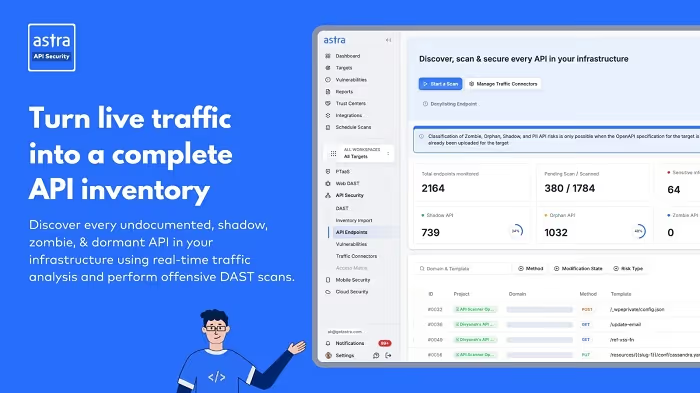
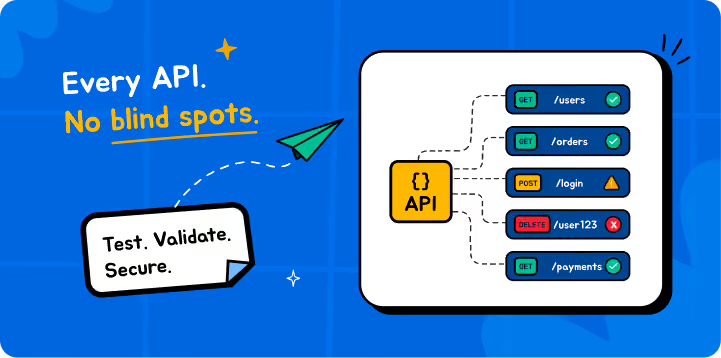
API Security
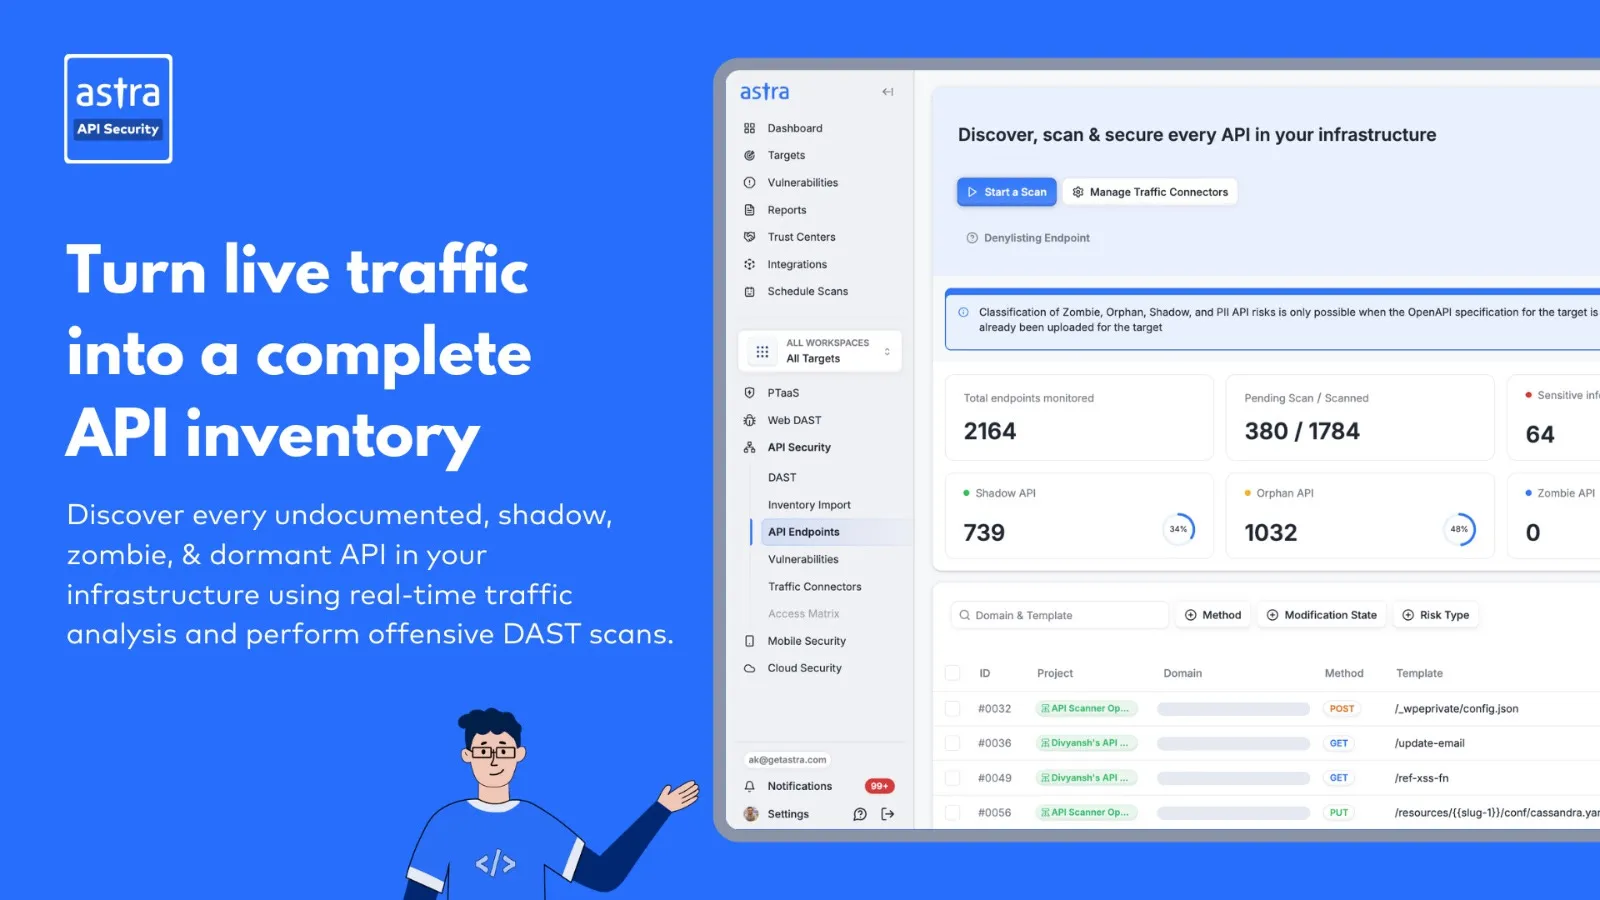
Discover, scan, and secure every API at scale.
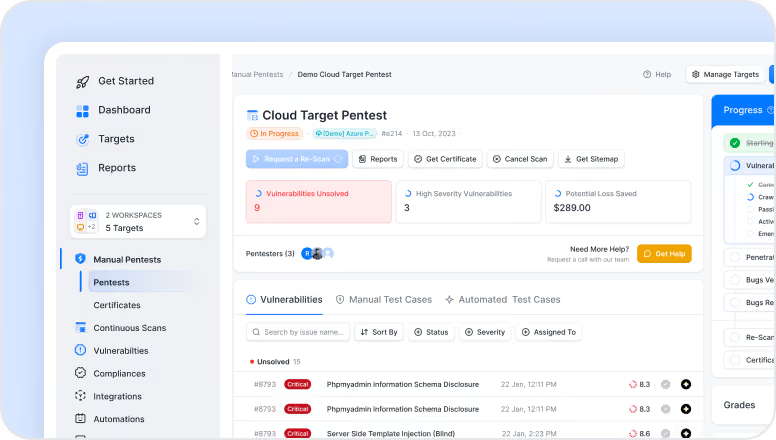
Cloud Scanner
400+ checks across AWS, Azure, and GCP. Agentless, always on.
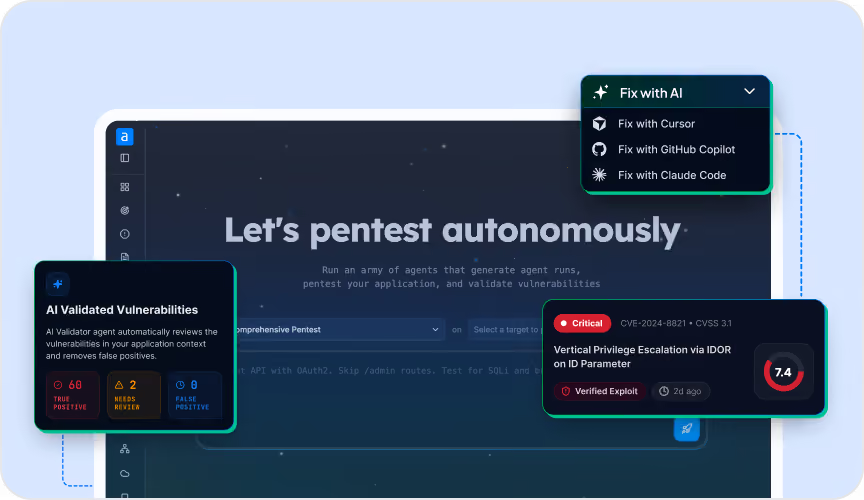
Autonomous Pentesting
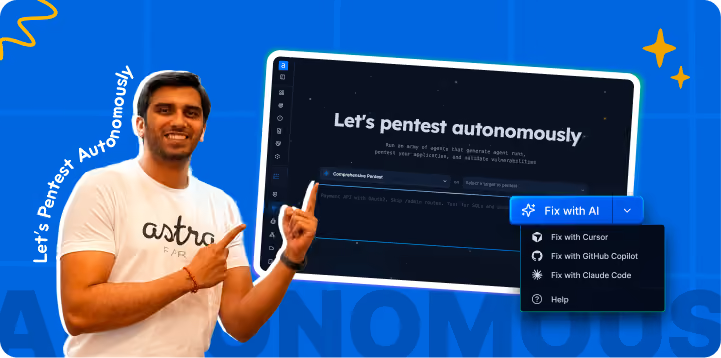
An independent army of AI agents that pentests just like humans do, but in hours, not weeks. Discovering, exploiting, validating, and fixing complex vulnerabilities, all autonomously. Making software self-healing.
OUR WORLD CLASS PENTESTERS
Certified Excellence in Offensive Security
At Astra, we believe in the power of offensive pentesting. Our in-house
pentest team doesn't just find vulnerabilities; they think like hackers to
uncover critical security flaws others often miss.
- OSCP (Offensive Security Certified Professional)
- CCSP (AWS) - ISC2 Certified Cloud Security Professional
- Certified Blockchain Security Professional
- eWPTXv2 (Web Application Penetration Tester)
- CEH (Certified Ethical Hacker)
- CREST, and many more
Our team has discovered and responsibly disclosed 50+ CVEs, actively contributing to global open-source security.
We conduct regular lab based training for our pentesters so that they always remain ahead of the curve.
Astra Security platform in the news