THE SECURITY RISKS WITH VIBE CODING: A STUDY

We built four apps just
to break them.

We gave four AI coding tools the same prompt. The apps shipped, so did 137 vulnerabilities across 5 different ways of getting the same 9 things wrong.

Findings surfaced by Astra's autonomous pentesting agents.
Vibe coding security risks study cover

DIY STRESS TEST

Patch the app

3 flaws, 30 seconds, zero shortcuts. Spoiler alert: AI coding tools had way longer,
and still missed 137 of these.

HOW TO PLAY

You have 30 seconds - the countdown starts when you click Start

Find the hidden flaw in each card.

Can you find all 3, before the timer hits zero?

THE METHODOLOGY

Same build, same pressure, every time

Emergent, Replit, Lovable, and Base44 all received an identical prompt, no advance notice, and
the same bar for what counted as a real finding with Astra's autonomous pentesting platform.

Zero advance notice to ensure unbiased & authentic testing.

No platform knew this was coming, and no vendor relationship affected access, testing, or results.

2 autonomous pentest bots that don't talk to each other.

Structured Pentest mapped the app and built attack chains, while Bug Bounty Hunter Bot went in cold, simulating an unbriefed attacker.

A validator agent tried to break every finding again.

Nothing moved forward until it was independently reproduced.

Then a human security engineer checked it all anyway.

Every finding was reviewed a second time before it counted, and anything unconfirmed was cut before analysis.

Want this run against your own
app instead of a demo build?

THE WEAK POINTS

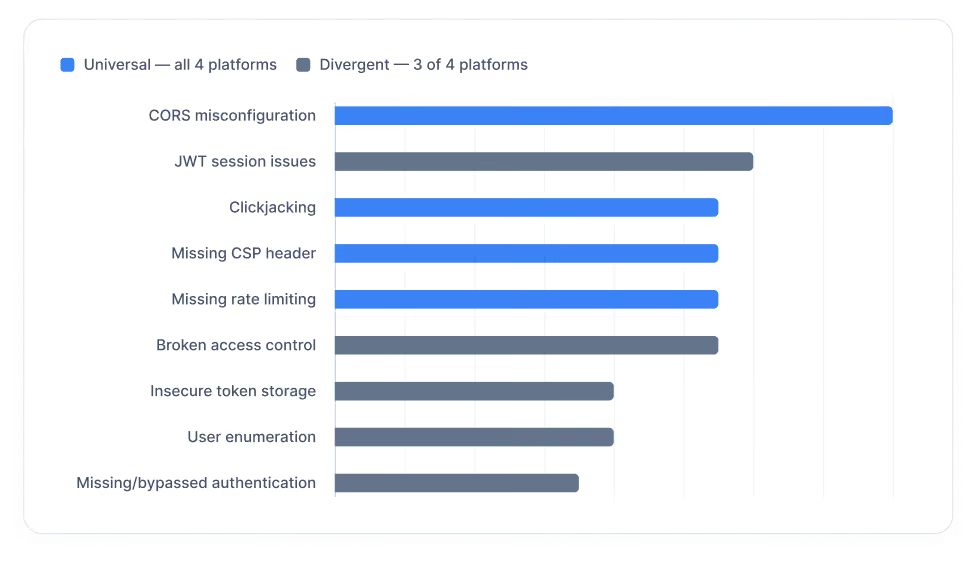
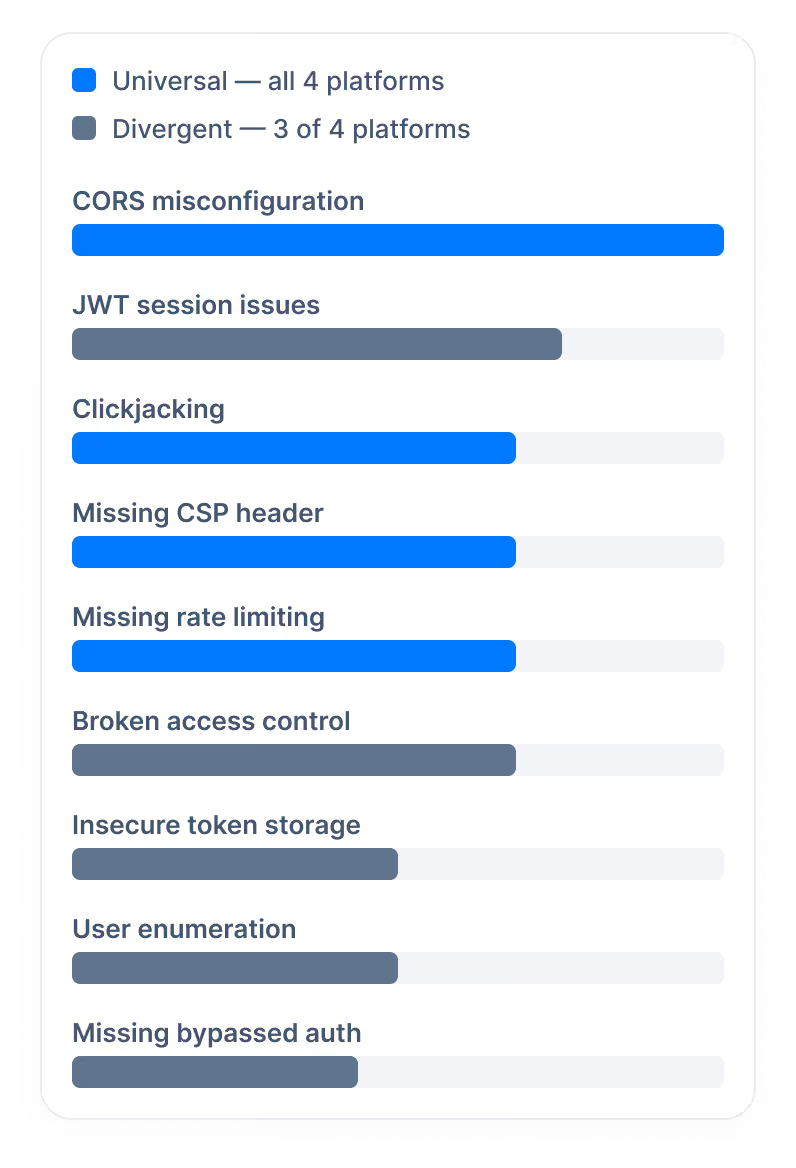
The 9 vibe coding vulnerabilities all four apps shared

Four separate codebases, four separate frameworks, and the same nine weak points gave out anyway.

The four pressure points

Prompt specificity

Vague asks, like “secure login,” instead of an exact threshold.

Finding volume vs. severity

High counts didn’t mean higher risk. Severity did.

Access control enforcement

The most severe failure, when it appeared, almost every time.

Fix complexity

Config-level for the universal patterns, data-layer for the rest.

See exactly where all four
builds gave out, and how to
reinforce yours.

Download the Report

Log in 8 times with the wrong password.

Attempt 6 should return a 429, not a 200.

Check any response's headers in DevTools.

No Content-Security-Policy means this is already a real finding.

Reset a password with a fake email, then a real one.
The response, wording, and timing should be identical either way.

See what gave out

Your next AI-generated app
hasn't been through this yet

Get the full report for every fracture point, every fix, and the prompt
built to hold up before you ship.

Get the PDF

What are the security risks of vibe coding?

The main risk is that AI tools build what you ask for and skip security. Across four AI-built apps, we found 137 confirmed vulnerabilities in the same nine weak points. Broken access control was almost always the most severe failure when it appeared, because it can let one user see or change another user's data.

Does this rank study the four platforms against each other?

No, this report evaluates what four applications built from the same prompt looked like under test, not which platform is more secure. Section 2 of the report states this explicitly.

Are these real vulnerabilities, or theoretical ones?

All vulnerabilities identified in the study are real. Findings were taken into consideration only if it was actually exploited, with evidence of impact, and independently reconfirmed by a second pass.

 Is vibe coding not safe?

Vibe-coded apps can get you to a working app fast, but working doesn’t always mean secure. In our study, four AI coding tools built the same app from the same prompt. All four apps worked, but together they contained 137 confirmed vulnerabilities. Before you ship, run the 10-minute security checklist on this page.

What are vibe coding security best practices?

Be specific in your prompts: ask for exact limits, such as locking login after five failed attempts, instead of "secure login." Enforce access control on the server and in the database, not just in the interface. Set security headers like Content-Security-Policy. Then test the running app before you ship, or have it pentested.

Is there a security prompt for vibe coding, and do I need a security background to use any of this?

Yes, there’s a security prompt, and no, you don’t need a security background to use it. The 10-minute checklist and the copy-paste prompt in Section 9 are designed to be used directly. Use it at the start of a build so key protections are included from version one, rather than patched in after launch.
Click here to update your cookies settings