


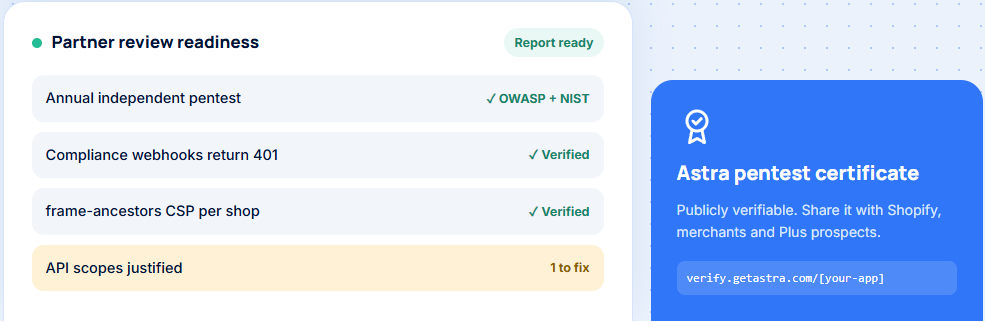
Which requirement are you facing?
Three ways Shopify asks about security.
Pick yours. The pentest shifts a little for each.
Certified Technology Partner.
Annual independent pentest. OWASP and NIST. Not optional, not self-assessed.
Protected customer data, Level 2.
Names, emails, addresses, phones. Seven extra controls to prove. A pentest is how you prove them.
App Store review or delisting notice.
Missing CSP. Unverified webhooks. OAuth after the UI. Small misses, long delays.
CVSS Severity Scoring
Every finding gets a score, so you know what needs to be fixed first and what can wait.
Remediation Guidance that’s not just “Implement Best Practices.”
We produce step-by-step fix instructions. We give you details on what was exploited, how we did it, and how you can fix it.
Proof-of-Concept Videos
Because “trust me, bro” won't cut it. We provide concrete proof that it is exploitable.
Retest what you fixed until it’s actually fixed.
Two manual re-scans are included with our pentest services. Additionally, we include unlimited automated rescans.
Your pentesters are only a text away.
Ask questions mid-engagement about findings, remediations, or just to say hi on our dashboard or Slack. We actually reply.
Trust Center
Verifiable pentest certificates and a shareable security posture page. Because saying your web application is secure is different from proving it.
Think the pentest is the end?
It's just the beginning.
We don't leave you high and dry post the pentest.
With Astra, a successful web app pentest is
the start of your security journey.
Regular automated scans with our DAST scanner having 10,000+ test case library

API security scanning that never sleeps

Continuous pentesting for your shiny new features
We play nice with your tools: GitHub, GitLab, Slack, JIRA - you name it

Modern web apps are intricate. Our expertise? Unmatched.
We understand the complexity of today's web applications. Our comprehensive offensive pentest approach dissects web apps into layers, and tests every layer:
API-first architectures
Microservices
Complex cloud infrastructures
And every layer in between

Frequently asked questions
What is included in Astra’s Web App Pentesting Services?
How long does a typical web application penetration test take?
What types of vulnerabilities are identified during a web application pentest?
How does the pricing work?
I have a specific scope, can you tailor the pricing?
Do you test APIs?
Which engagement options do you offer for black-box, grey-box, and white-box testing?
