For Shopify app developers

Shopify app penetration testing. Done before Shopify asks.

An independent Shopify app pentest, mapped to all 18 Shopify Certified Technology Partner security requirements.
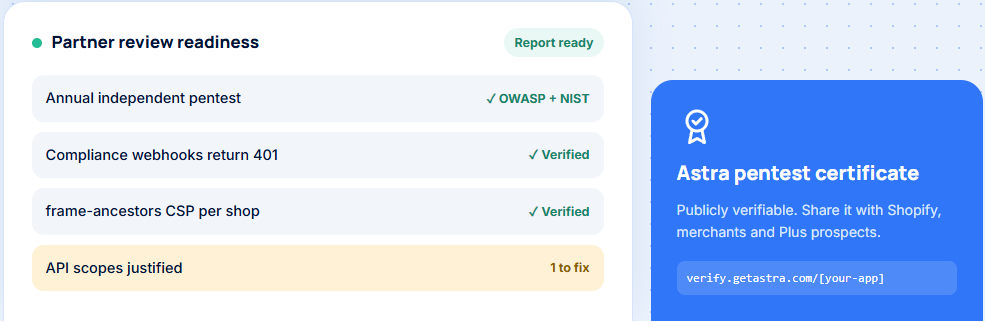
OWASP and NIST methodology. A certificate anyone can verify.

Astra's Web App Pentest Platform

Which requirement are you facing?

Three ways Shopify asks about security.

Pick yours. The pentest shifts a little for each.

Certified Technology Partner.

Annual independent pentest. OWASP and NIST. Not optional, not self-assessed.

Protected customer data, Level 2.

Names, emails, addresses, phones. Seven extra controls to prove. A pentest is how you prove them.

App Store review or delisting notice.

Missing CSP. Unverified webhooks. OAuth after the UI. Small misses, long delays.

What Shopify asks vs how Astra maps

18 controls. We'll tell you
which ones a pentest can
prove.

Not all of them, for the record. Six are your internal process, and the report says so.

5
Tested
7
Partly tested
6
Your process
01
Annual third-party pentest
02
Secrets and token storage
03
Architecture diagrams
04
Test vs prod separation
05
Data minimization
06
Minimal API scopes
07
Retention and deletion
08
TLS 1.2+ in transit
09
Encryption at rest
10
Encrypted backups
11
Data minimization
12
Role-based access control
13
Passwords and MFA
14
Vulnerability disclosure
15
Patching process
16
Staff data policies
17
Incident response plan
18
24-hour breach notice

OAuth and session tokens

OAuth before any UI. Tokens checked server-side.

Webhook HMAC (401)

Invalid signature? Expect a 401, every time.

frame-ancestors CSP

Your admin, frameable only by the shop.

Scope over-reach

Every API scope earns its place.

Multi-tenant shop isolation

Shop A never sees Shop B. We try every route.

App proxy and theme extensions

No injection through the storefront.

Billing tampering

No paid features without an active charge.

Token storage

Offline tokens encrypted. Never in logs.

How it works

Certificate in days. Not quarters.

Day 0
Scope
Dev store, test accounts, one 30-minute call.
Day 1
Autonomous pentest
AI agents run Shopify and OWASP tests. First findings in hours.
Day 1-14
Expert verification
Certified pentesters confirm every finding and dig into logic.
Fix Window
Re-scans
You fix. We re-test to prove it.
Done
Public certificate
Verifiable proof for Shopify and merchants.
Typical web app: 10–14 business days for the expert report. Re-scans depend on your plan.

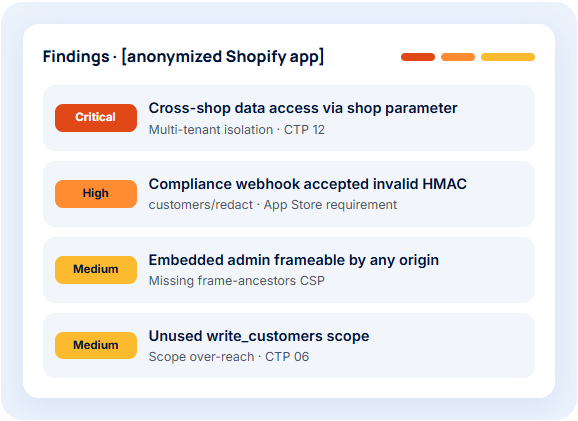
What we find in Shopify apps.

Anonymized. Each one ships with proof, severity and a fix your developers can use.

[Swap in anonymized findings signed off by the security team]

See a Sample Report

Pricing

Pricing, without the sales maze.

Offensive DAST vulnerability scanner that scans behind login for 15,000+
test cases like OWASP Top 10, ports, CVEs & more

LIMITED OFFER

Try DAST Scanner for a full week — just $7

Get platform access · No credit card commitment · Cancel anytime

Start $7 Trial

BEST FOR SMALL TEAMS
Scanner Lite
Schedule monthly vulnerability scans

$69/m

Astra
1 Target

Here's how the target is defined

Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, IP, website, API etc.

‍

If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

‍

Astra
Supported for
15,000+ test cases
3 vulnerability scans a month
Authenticated scanning
1 Integration (Slack, Jira, CI/CD etc.)
Vulnerability management console
Auto re-scan after fixes
AI fix assistance
Email support
⭐ Popular
BEST FOR SMALL TEAMS
Scanner
Unlimited security scans at dev speed

$199/m

1 Target

Here's how the target is defined

Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, IP, website, API etc.

‍

If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

Supported for
All Scanner Lite features, plus
Unlimited vulnerability scans
4 vetted scans (annual billing)
Unlimited integrations
BEST FOR SMALL TEAMS
Scanner Agency
Unlimited scans on a rotating pool

$499/m

5 Target Pool

Target

You get 5 target slots, with the ability to change targets in those slots with a 30-day cooling period. Example: Scan 5 targets, after 30 days scan 5 new targets.

Target Explained: Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, website, API etc. If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

‍

Get Started
Supported for
All Scanner features, plus
5-target pool, swap every 30 days
4 vetted scans (annual billing)
Customer success manager
LIMITED OFFER

Try DAST Scanner for a full week — just $7

Get platform access · No credit card commitment · Cancel anytime

Start $7 Trial

BEST FOR SMALL TEAMS
Scanner Lite
Schedule monthly vulnerability scans

$699/yr

Astra
1 Target

Here's how the target is defined

Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, IP, website, API etc.

‍

If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

‍

Astra
Supported for
15,000+ test cases
3 vulnerability scans a month
Authenticated scanning
1 Integration (Slack, Jira, CI/CD etc.)
Vulnerability management console
Auto re-scan after fixes
AI fix assistance
Email support
⭐ Popular
BEST FOR SMALL TEAMS
Scanner
Unlimited security scans at dev speed

$1999/yr

1 Target

Here's how the target is defined

Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, IP, website, API etc.

‍

If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

Supported for
All Scanner Lite features, plus
Unlimited vulnerability scans
4 vetted scans (annual billing)
Unlimited integrations
BEST FOR SMALL TEAMS
Scanner Agency
Unlimited scans on a rotating pool

$4999/yr

5 Target Pool

Target

You get 5 target slots, with the ability to change targets in those slots with a 30-day cooling period. Example: Scan 5 targets, after 30 days scan 5 new targets.

Target Explained: Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, website, API etc. If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

‍

Get Started
Supported for
All Scanner features, plus
5-target pool, swap every 30 days
4 vetted scans (annual billing)
Customer success manager
For Partners

Think your customers would love Astra too? Let's join forces.

Perfect for
Compliance platforms
MSSPs
Insurance providers
Auditors

Hacker-style pentest by Autonomous AI & certified experts at dev speed, built to meet & exceed
SOC2, ISO, & HIPAA requirement

BEST FOR SMALL TEAMS
Pentest Auto
1 Target

One web or SaaS app counts as one target, including all APIs consumed.
Mobile is per platform, so an Android app and an iOS app are two targets
Networks, cloud, IPs and standalone APIs are 1 target each

Hacker style autonomous pentest at machine speed

$2999/yr

$199/mo

Astra
1 Target
Astra
Astra
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Click the 🛈 icon to know more.
Pentest for SOC2, ISO 27001, HIPAA etc.
Supported for
Real-world attack simulation
Vulnerability management console
Role based graybox pentest
AI auto-fixes
Trust Center
1 human re-scan
Email support
1 Integration
⭐ Popular
BEST FOR SMALL TEAMS
Pentest Expert
1 Target

One web or SaaS app counts as one target, including all APIs consumed.
Mobile is per platform, so an Android app and an iOS app are two targets
Networks, cloud, IPs and standalone APIs are 1 target each

Offensive pentests by certified pentesters & autonomous agents

$5999/yr

Pentest for SOC2, ISO 27001, HIPAA etc.
Supported for
All Pentest Auto features, plus
Manual pentest by certified experts
CREST, PCI-ASV, CERT-IN reports
Unlimited web DAST scans
AI component pentesting
2 human re-scans
Customer success manager
Unlimited integrations
BEST FOR SMALL TEAMS
Enterprise
Autonomous testing & certified pentesters, tailored to your infra

$9999/yr onwards

Run a world class continuous pentest program.
Supported for
All Pentest Expert features, plus
Security consulting
On-premise deployment
Private cloud instance
Custom SLA & payment terms
Voice on roadmap
Custom workspace management
ScannER

$999/yr

$75/mo effectively
Astra
1 Target
Astra
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Know More
Get Started
tick

Weekly vulnerability scans with 3000+ tests (OWASP, SANS etc.)

tick

Essential features like pentest dashboard, PDF reports and scan behind login
For Partners

Think your customers would love Astra too? Let's join forces.

Perfect for
Compliance platforms
MSSPs
Insurance providers
Auditors

Continuously discover & scan every API in your infrastructure for broken access control, authorization flaws, OWASP Top 10 & more

BEST FOR SMALL TEAMS
API DAST Scanner
Scheduled DAST scans on your API spec file
‍

$199/m

$199/mo

1 Target
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Click the 🛈 icon to know more.
15,000+ authenticated test cases
20 scans a month
CI/CD, JIRA & Slack
Auto re-scan after fixes
Full & management PDF reports
Email support
Extra scans at $10
⭐ Popular
BEST FOR SMALL TEAMS
API Security Pro
Continuous API discovery and scans               

$499/m

All API DAST Scanner features, plus
60 scans a month
Live API traffic capture
Continuous observability & inventory
Adds CSV & JSON reports
Orphan, shadow, zombie APIs
BEST FOR SMALL TEAMS
API Enterprise
Discovery and scanning at enterprise scale
‍

Custom

All API Security Pro features, plus
1000+ scans a year
15M+ API requests observed
Tailored test cases
Dedicated account manager
Volume-based scan pricing
BEST FOR SMALL TEAMS
API DAST Scanner
Scheduled DAST scans on your API spec file
‍

$1999/yr

$199/mo

1 Target
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Click the 🛈 icon to know more.
15,000+ authenticated test cases
20 scans a month
CI/CD, JIRA & Slack
Auto re-scan after fixes
Full & management PDF reports
Email support
Extra scans at $10
⭐ Popular
BEST FOR SMALL TEAMS
API Security Pro
Continuous API discovery and scans               

$4999/yr

All API DAST Scanner features, plus
60 scans a month
Live API traffic capture
Continuous observability & inventory
Adds CSV & JSON reports
Orphan, shadow, zombie APIs
BEST FOR SMALL TEAMS
API Enterprise
Discovery and scanning at enterprise scale
‍

Custom

All API Security Pro features, plus
1000+ scans a year
15M+ API requests observed
Tailored test cases
Dedicated account manager
Volume-based scan pricing
For Partners

Think your customers would love Astra too? Let's join forces.

Perfect for
Compliance platforms
MSSPs
Insurance providers
Auditors

Astra continuously scans AWS, Azure, and GCP for misconfigs, IAM risks, and vulnerabilities, validating every finding before it reaches you

LIMITED OFFER

Try Cloud Starter for a full week — just $7

Full platform access · AWS, Azure & GCP · No credit card commitment · Cancel anytime

Start $7 Trial

BEST FOR SMALL TEAMS
Cloud Starter
Scan for cloud security misconfigurations across your cloud account

$99/m

$199/mo

1 Target
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Click the 🛈 icon to know more.
Supported for
Security misconfigs & IAM checks
1 cloud account
Up to 250 resources
Unlimited automated scans
Auto re-scan after fixes
PDF reports
Validated findings
Unlimited Integrations
Email support
⭐ Popular
ENTERPRISE-READY (CUSTOM)
Cloud Growth
Scheduled multi-account scans with control mapping

$199/m

Supported for
All Cloud Starter features, plus
3 cloud accounts
Up to 1000 resources
Scheduled scans
Control mapping
JSON & management reports
BEST FOR LARGE TEAMS
Cloud Enterprise
Multi-cloud and hybrid scanning at enterprise scale

Custom

Supported for
All Cloud Growth features, plus
Multi-cloud & hybrid
Unlimited resources
Continuous scan scheduling
Custom dashboards
Customer Success Manager
LIMITED OFFER

Try Cloud Starter for a full week — just $7

Full platform access · AWS, Azure & GCP · No credit card commitment · Cancel anytime

Start $7 Trial

BEST FOR SMALL TEAMS
Cloud Starter
Automated configuration scans on your cloud account

$999/yr

$199/mo

1 Target
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Click the 🛈 icon to know more.
Supported for
Security misconfigs & IAM checks
1 cloud account
Unlimited automated scans
Up to 250 resources
Auto re-scan after fixes
PDF reports
Validated findings
Unlimited Integrations
Email support
⭐ Popular
Cloud Growth
ENTERPRISE-READY (CUSTOM)
Scheduled multi-account scans with control mapping

$1999/yr

Supported for
All Cloud Starter features, plus
3 cloud accounts
Up to 1000 resources
Scheduled scans
Control mapping
JSON & management reports
BEST FOR LARGE TEAMS
Cloud Enterprise
Multi-cloud and hybrid scanning at enterprise scale

Custom

Supported for
All Cloud Growth features, plus
Multi-cloud & hybrid
Unlimited resources
Continuous scan scheduling
Custom dashboards
Custom integrations & API
Customer Success Manager
For Partners

Think your customers would love Astra too? Let's join forces.

Perfect for
Compliance platforms
MSSPs
Insurance providers
Auditors

What is included in Astra’s Web App Pentesting Services?

Astra’s Web App Pentesting includes manual and automated vulnerability assessments, business logic testing, OWASP Top 10 coverage, remediation guidance, continuous re-scans, and a collaborative dashboard for tracking vulnerabilities until they’re fixed and verified.

How long does a typical web application penetration test take?

A typical web application penetration test (pentest) takes 10-14 business days, depending on the app’s complexity, scope, and technology stack. This includes time for testing, reporting, and verifying fixes through re-scans to ensure all vulnerabilities are resolved.

What types of vulnerabilities are identified during a web application pentest?

Astra’s pentests uncover critical issues like authentication flaws, injection attacks, broken access control, insecure configurations, and business logic errors. We align with OWASP Top 10 and industry-specific compliance standards to ensure complete coverage of potential threats.

How does the pricing work?

The pricing for API Security Platform depends on the number of APIs endpoints you have. You can check pricing right here

I have a specific scope, can you tailor the pricing?

Absolutely, you can schedule a call with our sales engineers. In the call they review the scope, show our platform and are happy share a tailored pricing specific to your needs.

Do you test APIs?

Yes. Astra Security tests APIs as part of web application penetration testing when they are included in the scope of the engagement. API testing helps identify issues such as authorization flaws, data exposure, insecure, orphan, or zombie APIs, and OWASP API Security Top 10 risks across connected application workflows.

Which engagement options do you offer for black-box, grey-box, and white-box testing?

Astra Security supports black-box, grey-box, and white-box web application penetration testing. In black-box testing, the pentesters test with no internal access to your systems. Grey-box testing uses partial internal access with limited credentials or context. White-box testing provides pentesters with full access to applications, architecture, code, or documentation for a comprehensive security assessment.
BLOG

PHP2Shell: Two Critical PHP Vulnerabilities, How They Work, and What to Do About Them

Explore the guide
BLOG

LiteLLM Supply Chain Attack: v1.107.0 IOCs and Response Steps

Explore the guide
BLOG

CVE-2026-110264: GitLab’s Critical CVSS 10.0 Regex RCE Explained

Explore the guide
BLOG

Node.js Security Release (October 2026): Brotli RCE + 9 CVEs

Explore the guide
BLOG

Railway Breach: What to Rotate, and What Rotation Won’t Fix

Explore the guide
Click here to update your cookies settings