Top Penetration Testing Companies in USA & Canada

Here’s why you should choose Astra

Find real issues, not noisy scans - every vulnerability reviewed by certified security engineers with video PoC and fix guidance.

Test continuously as you release - plug into CI/CD, GitHub, GitLab, Jira, and Slack to catch issues before production.

SOC 2, ISO 27001, PCI-DSS, HIPAA-ready - auditor-accepted reports, compliance gap mapping, and a Trust Center your customers can verify.

Fix faster with clear remediation guidance - get proof-backed findings, step-by-step fixes, and retest support so your team can close vulnerabilities without the usual back-and-forth.

Talk to our Security Experts
See how Astra finds what other platforms miss. 30-min personalized demo.
Better pricing, tailored to you. Book a call to unlock it
2026 Rankings

Top 9 Penetration Testing Companies in 2026

Based on capabilities, platform maturity, compliance coverage, customer reviews, and value for money.

#
Company
Best For
Pricing
G2 Rating
1
Astra Security
YOU'RE HERE
Continuous PTaaS
From $2,999/yr
★ 4.6/5
2
Rapid7
Vuln management
$2,100/yr
★ 4.4/5
3
TechMagic
Complex logic testing
On request
★ 4.5/5
4
Acunetix
Web scanning
$2,500/yr
★ 4.4/5
5
CrowdStrike
Endpoint + network
On request
★ 4.3/5
6
Intruder
Cloud pentesting
$1,958/yr
★ 4.3/5
7
Indusface WAS
Web app security
On quote
★ 4.5/5
8
BreachLock
AI-augmented pentest
On quote
★ 4.3/5
9
SecureWorks
Security consulting
On quote
★ 4.1/5

Loved by 1000+ CTOs & CISOs worldwide

We are impressed by Astra's commitment to continuous rather than sporadic testing.

Wayne
Wayne Garb
CEO, OOONA

Astra not only uncovers vulnerabilities proactively but has helped us move from DevOps to DevSecOps

Vinish Vijayan
IT Manager, Muthooth Finance

Their website was user-friendly & their continuous vulnerability scans were a pivotal factor in our choice to partner with them.

Larry Crawley
CTO, Strategic Audit Solutions, Inc.

The combination of pentesting for SOC 2 & automated scanning that integrates into our CI pipelines is a game-changer.

Jack Collins
Head of Product Engineering, Naro

I like the autonomy of running and re-running tests after fixes. Astra ensures we never deploy vulnerabilities to production.

Arthur De Moulins
Web Architect, Vkard

We are impressed with Astra's dashboard and its amazing ‘automated and scheduled‘ scanning capabilities. Integrating these scans into our CI/CD pipeline was a breeze and saved us a lot of time.

Ankur Rawal
CTO, Zenduty

Voted #1  Best Software

Ease of use
Meets requirements
Quality of support

Top 9 Penetration Testing Companies,
Detailed Reviews

Astra is #1 in our rankings. Here's a deep look at companies #2–#9, what they do well,
where they fall short, and how their pricing compares.

★ #1 Ranked
Editor's Choice 2026
Astra Security
Best for: Continuous PTaaS with zero false positives

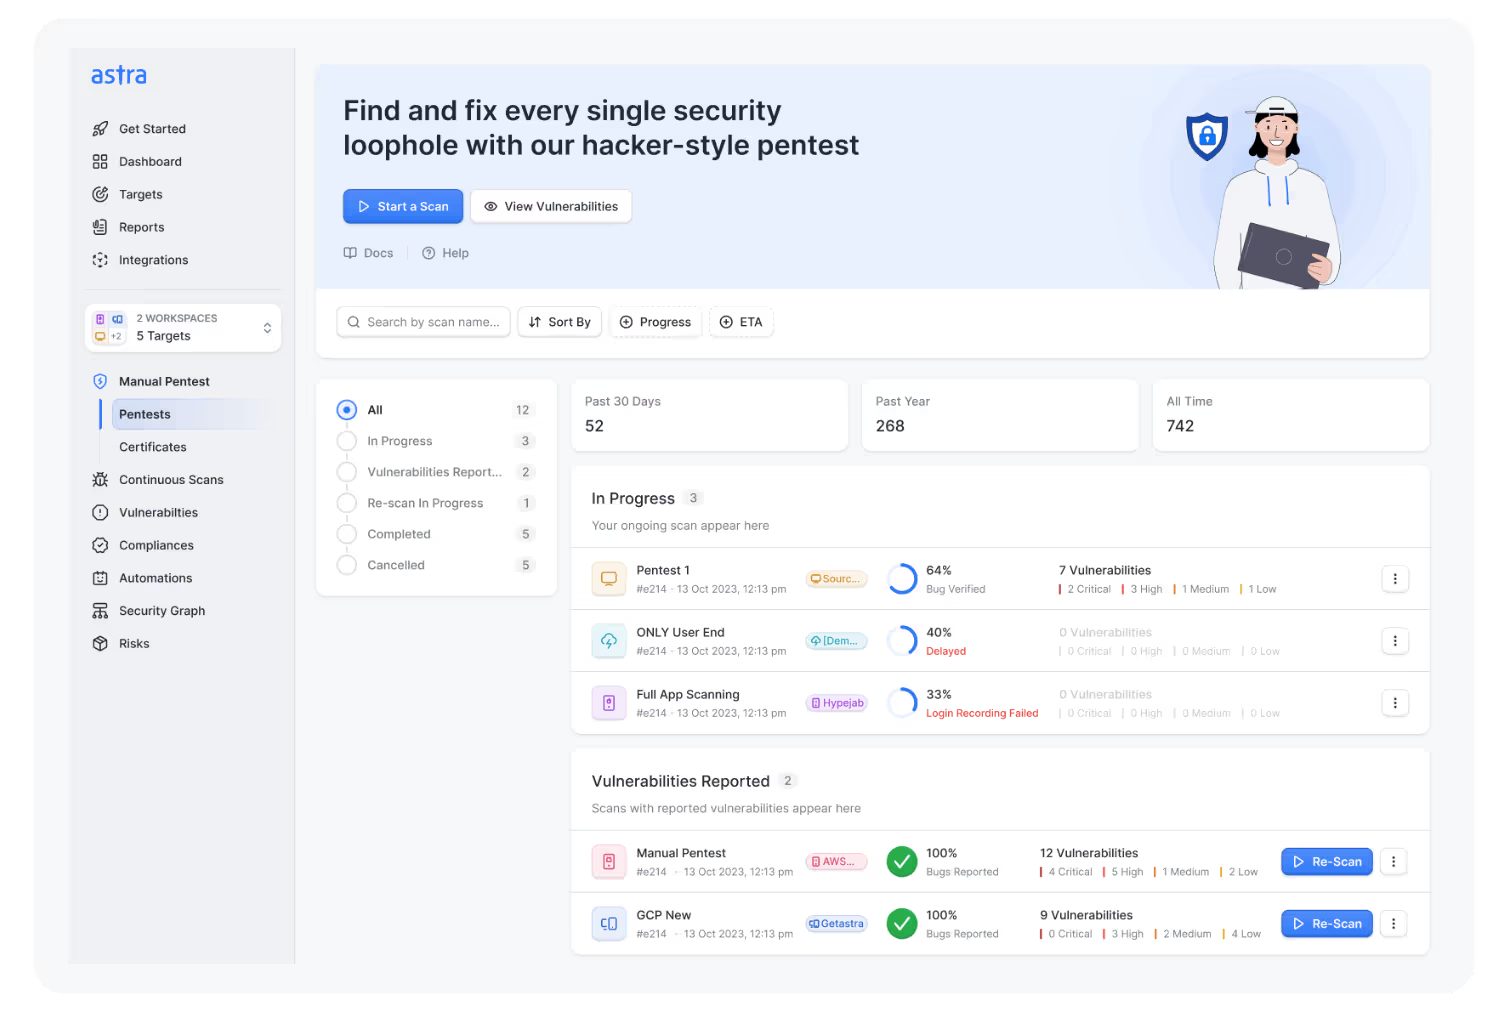
Astra is an AI-powered continuous PTaaS platform combining automated DAST scanning with expert-led manual pentesting. Trusted by 1000+ teams across US & Canada, every finding is human-verified by OSCP/CEH-certified engineers — and you get a publicly verifiable security certificate after remediation.

Key Features
Scanner Capacity: Web, API, Cloud (AWS/Azure/GCP), Mobile, Network, AI/LLM — 15,000+ test cases
Accuracy: Zero false positives — every vulnerability vetted by a security engineer
Scan Behind Logins: Yes — full authenticated scanning included on all tiers
Compliance: SOC 2, ISO 27001, PCI DSS, HIPAA, GDPR — one-click audit-ready reports
Integrations: Jira, GitHub, GitLab, Jenkins, Slack, CircleCI — native CI/CD plug-in
Publicly Verifiable Certificate: Yes — shareable proof after clean rescan
Pricing: From $1,999/yr (Basic) · $5,999/yr (Pentest Plus with manual testing)
PROS
✓ AI + human hybrid — best of both worlds
✓ Zero false positives — saves dev triage hours
✓ Continuous scanning on every CI/CD deploy
✓ 2 free rescans + expert remediation support
✓ Publicly verifiable security certificate
✓ Transparent pricing — 60–80% less than traditional vendors
CONS
− Dashboard can feel slow at peak load (per G2 reviews)
− Best fit for SaaS/cloud — less depth on on-prem hardware

Book a demo

2
Rapid 7
Best for: Enterprise vulnerability management

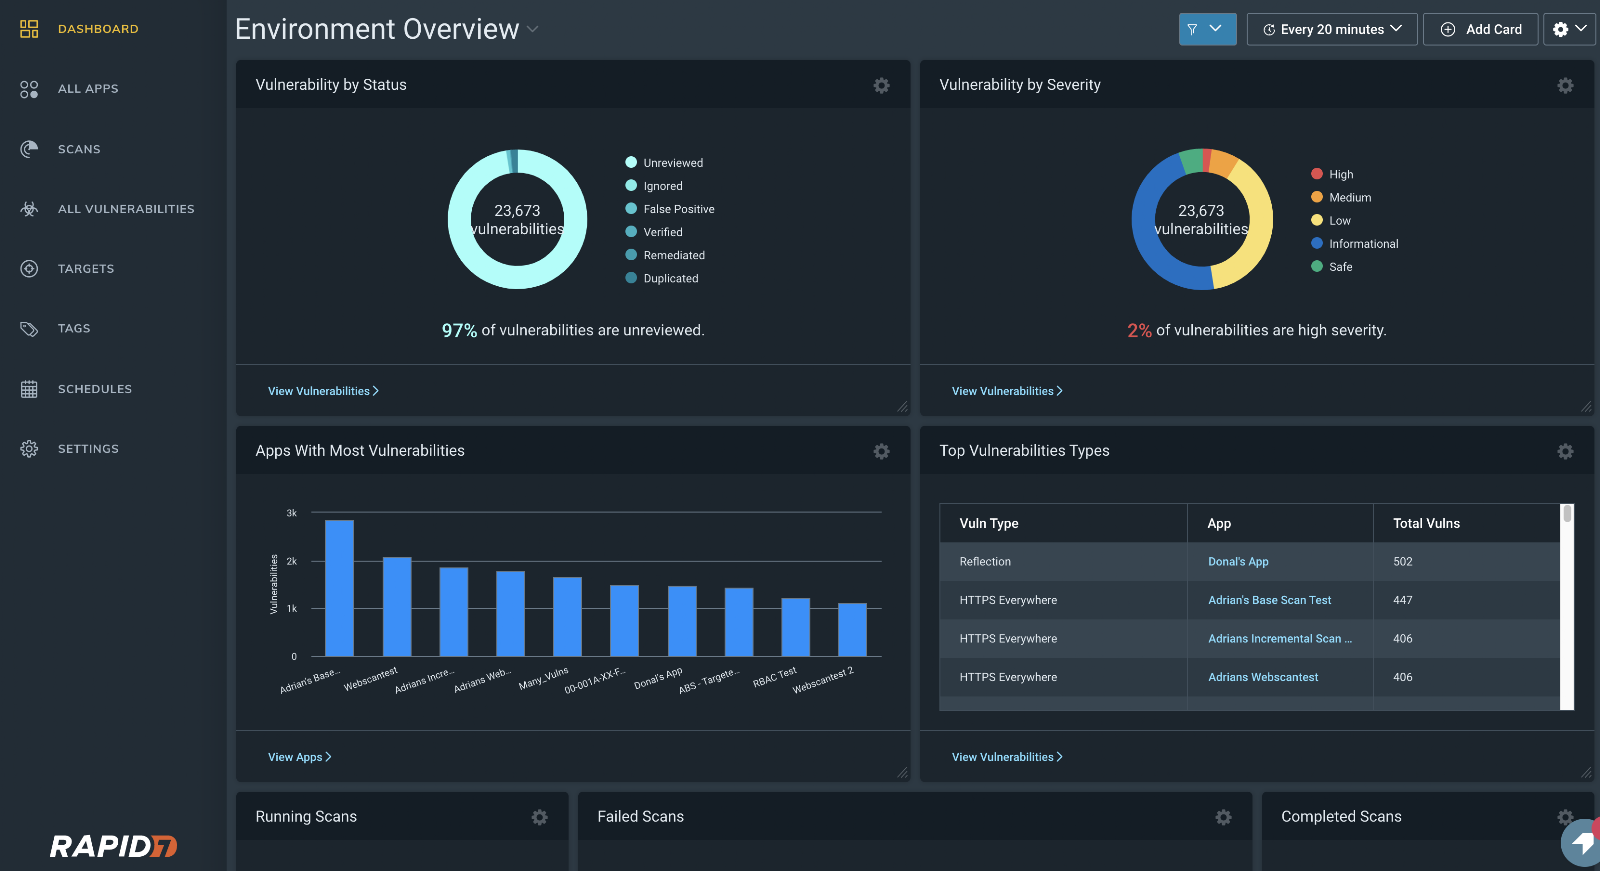
Rapid7's InsightAppSec combines the proven AppSpider engine with a modern cloud platform. It leverages deep vulnerability management heritage (and Metasploit's exploit research) to deliver platform-integrated pentesting with expert consultation via a cloud portal that streams live results.
Key Features
Scanner Capacity: Web applications, APIs (REST, JSON, AMF), cloud workloads
Accuracy: Automation-heavy — noisy results may need manual triage
Scan Behind Logins: Yes — with attack-replay scripts for developer reproduction
Compliance: PCI DSS, HIPAA, ISO 27001, SOC 2 reporting
Integrations: Deep ties with Atlassian Jira & ServiceNow ITSM
Pricing: ~$2,100/year per application; scales steeply with scope
PROS
✓ Easy-to-navigate UI with strong reporting
✓ Business logic testing via expert consultants
✓ In-depth network visibility (InsightVM ecosystem)
✓ Custom exploit development from Metasploit team
CONS
− Easy-to-navigate UI with strong reporting
− Business logic testing via expert consultants
− In-depth network visibility (InsightVM ecosystem)
− Custom exploit development from Metasploit team
3
TechMagic
Best for: Complex business-logic testing

TechMagic is a security-engineering services firm offering custom-scoped pentests for SaaS, fintech, and healthcare applications. Their teams focus on manual exploitation of business-logic flaws that scanners miss — auth chains, workflow abuse, multi-step exploits.

Key Features
Scanner Capacity: Manual-only — no proprietary scanner
Accuracy: Human-verified findings, low false-positive rate
Scan Behind Logins: Yes — full authenticated testing
Compliance: ISO 27001, SOC 2, HIPAA reporting
Integrations: Jira, Slack via project-based delivery
Pricing: ~Quote-based; engagement-style billing
PROS
✓ Deep manual expertise on logic flaws
✓ Tailored scoping per engagement
✓ Strong SaaS and fintech domain knowledge
CONS
− No continuous scanning platform — point-in-time only
− Slower turnaround vs. PTaaS vendors
− Opaque pricing; no published rate card
− No publicly verifiable security certificate
4
Acunetix
Best for: Automated web vulnerability scanning

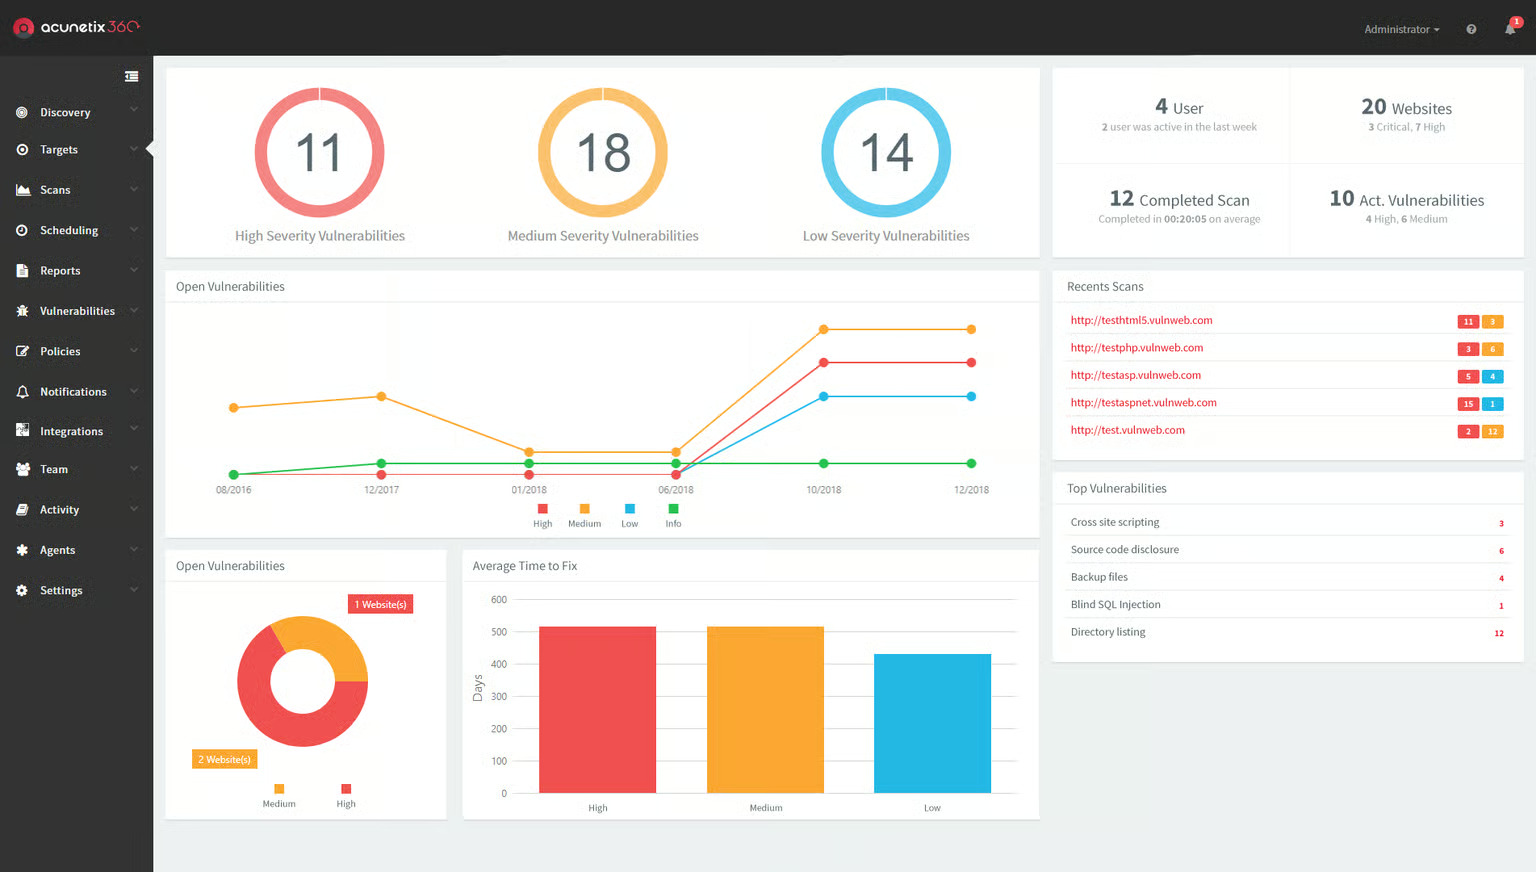
Acunetix (by Invicti) is a fully automated DAST tool that scans for 7,000+ vulnerabilities including OWASP Top 10, SQL injection, and XSS variants. It supports SPAs, HTML5, and script-heavy sites with developer-friendly IDE and CI/CD integrations.
Key Features
Scanner Capacity: Web applications, SPAs, basic API scanning
Accuracy: Proof-of-concept videos reduce noise; no zero-FP guarantee
Scan Behind Logins: Yes — session-based authentication
Compliance: OWASP, PCI DSS, HIPAA, ISO 27001 reports
Integrations: Jira, GitHub, GitLab, Jenkins, IDE plugins
Pricing: From ~$7,000/year for 5 targets; scales by scope
PROS
✓ User-friendly UI, fast to configure
✓ Detailed PoC + remediation guidance per finding
✓ Strong SPA & JavaScript-heavy site coverage
✓ Automates retest of fixed vulnerabilities
CONS
− No expert remediation assistance
− Self-served pentest — not vetted by humans
− Dated interface vs. modern PTaaS competitors
− No published pricing; quote-only
5
CrowdStrike
Best for: Adversary emulation & red teaming

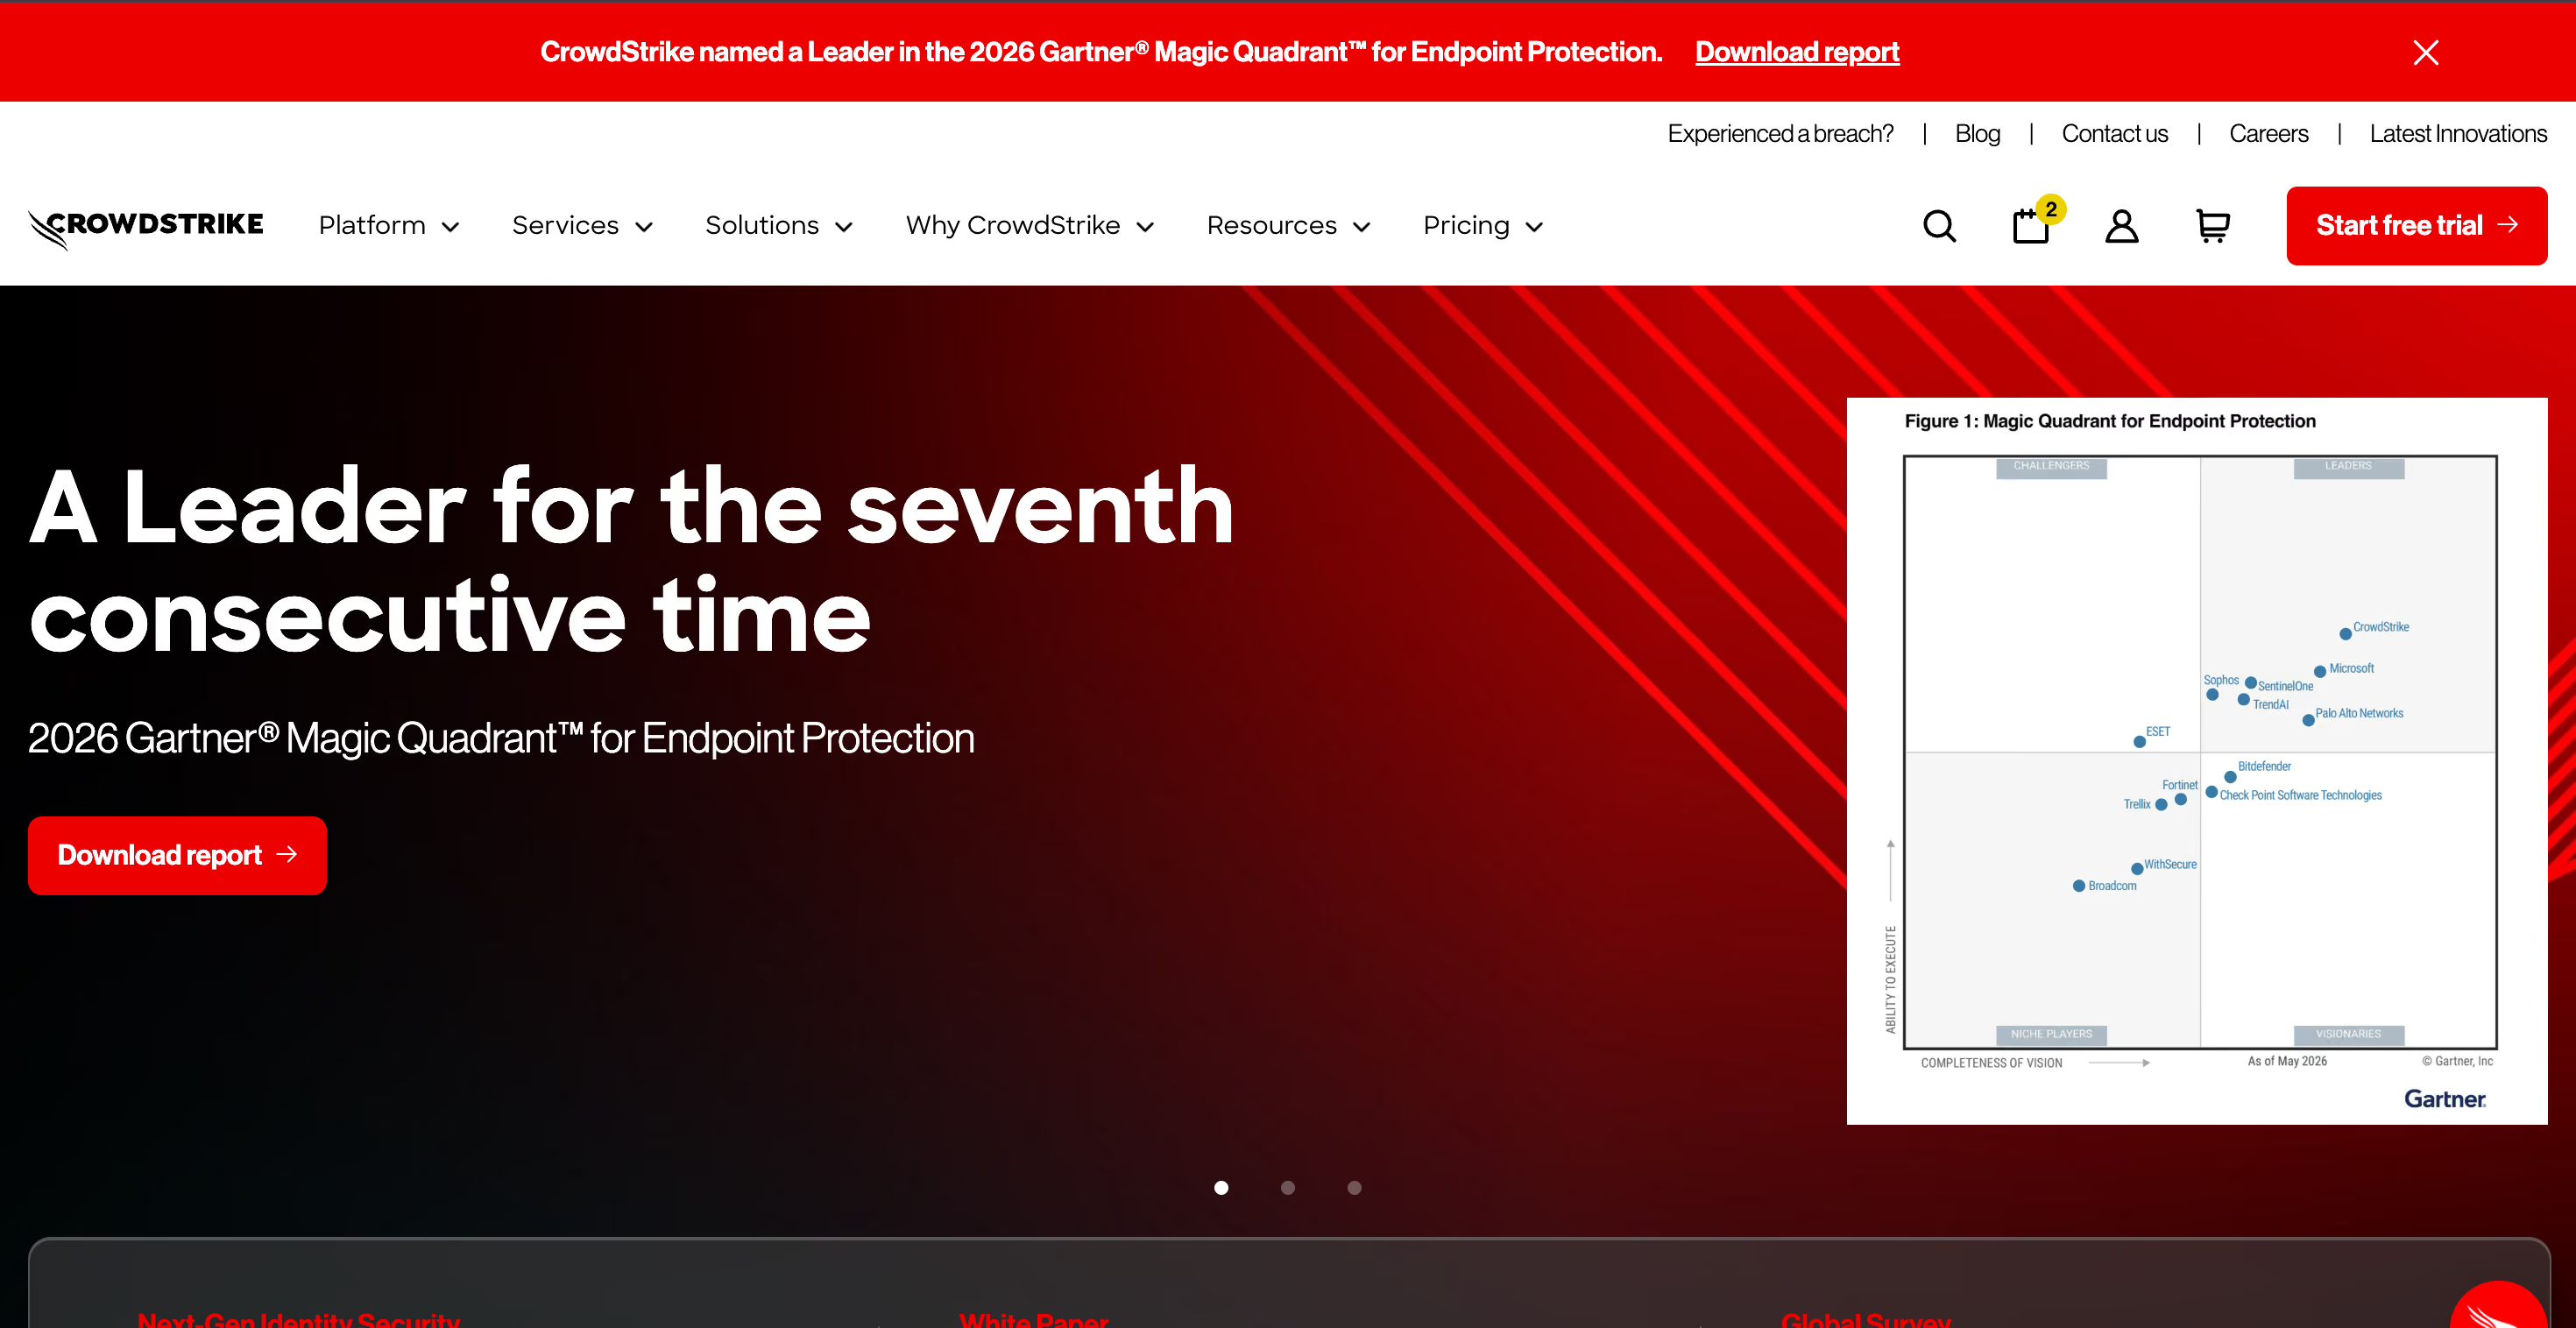
CrowdStrike's Falcon Overwatch team runs intel-driven adversary emulation and red-team exercises using real-world nation-state TTPs. Best fit for large enterprises that already use Falcon for EDR/MDR and want testing aligned to that telemetry.
Key Features
Scanner Capacity: Endpoint, network, cloud, adversary emulation
Accuracy: Intel-led; real attacker TTPs, not generic checklists
Scan Behind Logins: Yes — full red team scope
Compliance: Aligns with NIST, MITRE ATT&CK; lighter on SOC 2/PCI
Integrations: Native Falcon EDR + cloud protection telemetry
Pricing: $75K+ per engagement; 3–6 week timelines
PROS
✓ Threat-intel driven simulations (real-world TTPs)
✓ Strong red team & incident response alignment
✓ Best-in-class for enterprises on Falcon platform
CONS
− Overkill for checkbox compliance pentests
− Not cost-effective for audit-only needs
− Value drops without existing Falcon telemetry
− Long engagement timelines (3–6 weeks)
6
Intruder
Best for: Cloud & external attack-surface scanning

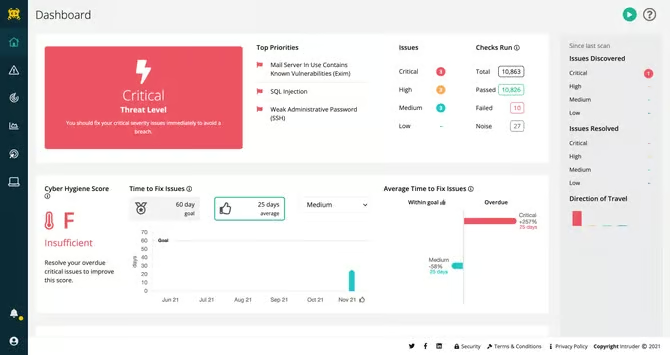
Intruder is a cloud-based vulnerability scanner focused on external attack surface and cloud infrastructure. Lightweight to deploy and priced for smaller teams, it's a popular starting point for orgs that need continuous external monitoring without enterprise-tier complexity.
Key Features
Scanner Capacity: External infra, cloud workloads, basic web app scanning
Accuracy: Tenable & OpenVAS engines; noise filtering on by default
Scan Behind Logins: Limited authenticated scanning
Compliance: SOC 2, ISO 27001 evidence reports
Integrations: AWS, GCP, Azure connectors; Slack & Jira
Pricing: $1,188–$2,880/year depending on tier
PROS
✓ Cost-competitive entry tier for startups
✓ Strong external attack-surface coverage
✓ Quick onboarding; minimal configuration
CONS
− No manual pentesting — scanner only
− Shallower web app coverage than dedicated DAST
− No publicly verifiable security certificate
− Limited remediation support
7
Indusface WAS
Best for: Web app security with managed WAF

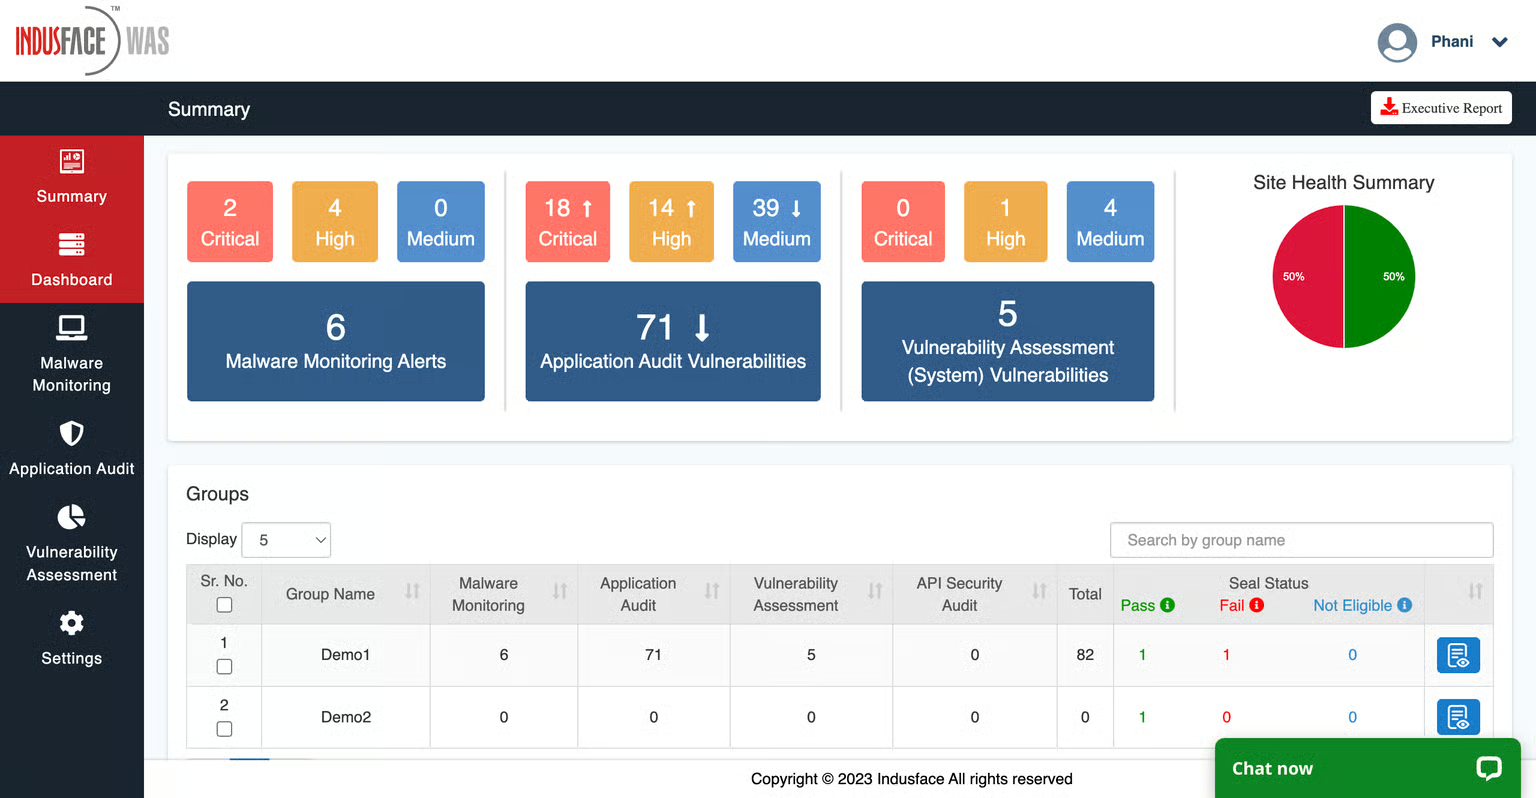
Indusface WAS combines automated scanning with manual penetration testing and managed security services. It detects OWASP Top 10 and business-logic errors, with strong intelligent-crawl support for SPAs and unlimited scan tiers.
Key Features
Scanner Capacity: Web apps, APIs, SPA-aware crawler
Accuracy: Promises zero false positives with manual validation
Scan Behind Logins: Yes — authenticated scans supported
Compliance: PCI DSS, ISO 27001, OWASP, WASC reports
Integrations: CI/CD pipelines, AppTrana WAF tie-in
Pricing: Quote-based; bundled with AppTrana WAF
PROS
✓ Short learning curve; fast asset discovery
✓ Zero-FP promise with remediation assistance
✓ Strong managed-WAF bundle option (AppTrana)
CONS
− Limited to web app surface — no network/cloud depth
− Heavy AI reliance can produce false negatives
− No publicly verifiable security certificate
− Pricing not transparent — quote-only model
8
BreachLock
Best for: AI-augmented hybrid pentesting

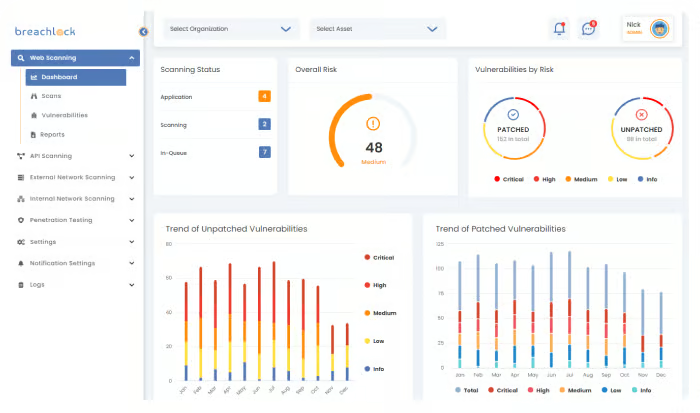
BreachLock is a US-based, CREST-certified PTaaS provider running AI-augmented pentests with human validation. It combines automated baseline coverage with manual testing for applications, APIs, cloud, network, and mobile — with audit-ready compliance reports.
Key Features
Scanner Capacity: Web, API, network, cloud, mobile
Accuracy: AI + manual hybrid; not zero-FP guaranteed
Scan Behind Logins: Yes — authenticated tests included
Compliance: SOC 2, PCI DSS, HIPAA, ISO 27001 reports
Integrations: Jira, ServiceNow; client portal for findings
Pricing: Custom quote; enterprise-tier project management
PROS
✓ CREST-certified with audit-ready reports
✓ Hybrid AI + human model keeps costs reasonable
✓ Easy-to-use portal with prioritized findings
✓ Broad coverage (web, API, cloud, network, mobile)
CONS
− Custom-quote pricing; no transparent rate card
− Less aggressive false-positive elimination than peers
− No publicly verifiable security certificate
− Heavier sales process for SMB buyers
9
SecureWorks
Best for: MSSP-style security consulting

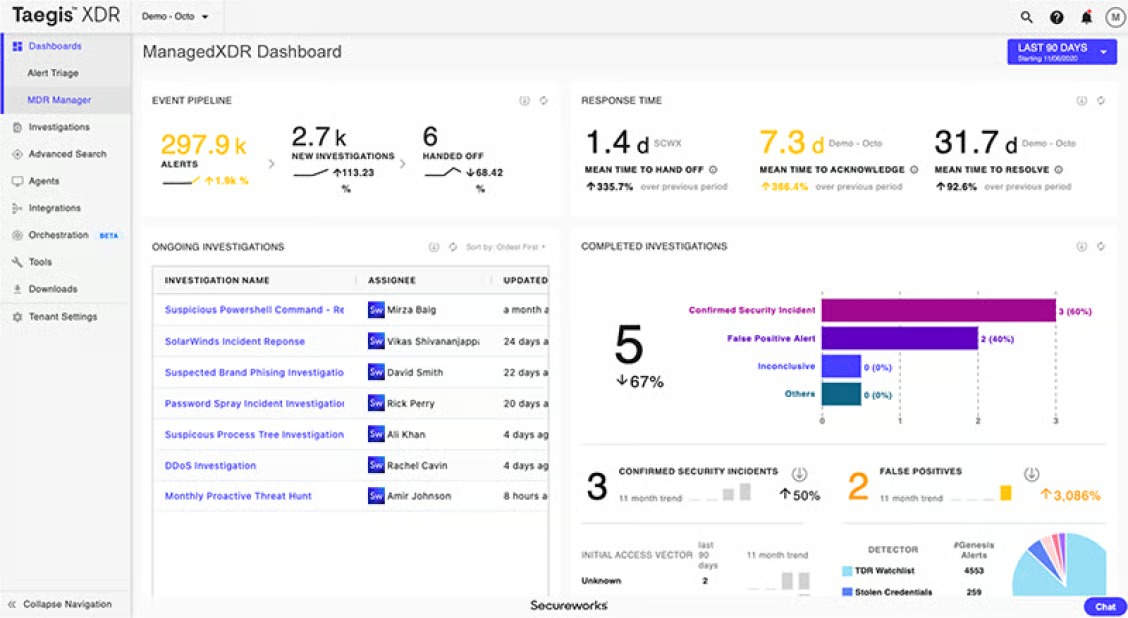
SecureWorks (now part of Sophos) is a Managed Security Services Provider delivering pentesting deeply integrated with its proprietary Counter Threat Unit (CTU) intelligence. Best for regulated industries needing FFIEC, HIPAA, and PCI-oriented engagements with multi-vector attack simulation.
Key Features
Scanner Capacity: Web, mobile, networks, APIs, phishing
Accuracy: CTU-intelligence backed; expert-led delivery
Scan Behind Logins: Yes — full-scope engagement model
Compliance: FFIEC, HIPAA, PCI DSS, ISO 27001
Integrations: SecureWorks Taegis XDR platform tie-in
Pricing: Quote-only; enterprise consulting model
PROS
✓ Strong threat-intel integration via CTU
✓ Multi-vector attack simulation (external + internal + phishing)
✓ Intuitive interface; consistent service delivery
✓ Compliance-friendly for regulated verticals
CONS
− Recently acquired by Sophos roadmap uncertainty
− Slow, consulting-style engagements vs. PTaaS
− No published pricing; enterprise sales cycles
− No publicly verifiable security certificate

How much does a penetration test cost?

Industry pricing ranges from $5,000 to $50,000+ per engagement. Astra's PTaaS model starts at $1,999/year for automated scanning, with expert manual pentesting at $5,999/year — typically 60-80% less than traditional engagement-based pricing.

How long does a penetration test take?

Automated scans complete within 24-72 hours. Manual pentesting takes 5-10 business days depending on scope. You receive findings as they're discovered, not just at the end.

Does SOC 2 require penetration testing?

While SOC 2 doesn't explicitly mandate pentesting, most auditors expect it as evidence of security control effectiveness. Astra's reports are formatted for SOC 2 auditor review with mapped controls and documented evidence.

What makes Astra different from other pentesting companies?

Three things: (1) Automated scanning + manual testing on one platform. (2) Zero false positives — every finding verified by a security engineer. (3) A publicly verifiable security certificate after remediation, not just a PDF report.

Can I integrate Astra into my CI/CD pipeline?

Yes. Native integrations with Jira, GitHub, GitLab, Slack, and Jenkins. Scans trigger on every deploy with vulnerability alerts sent directly to your team's workflow.

Ready to shift left and ship right?

Let's chat about making your releases faster and more secure
Click here to update your cookies settings