Audit-ready reports in hours for DORA, GDPR, ISO 27001, SOC 2, and
PCI-DSS. Compliance gap mapping included.
No false positives. Every finding verified by a CREST-certified expert
with video PoC, impact context, and clear remediation guidance.
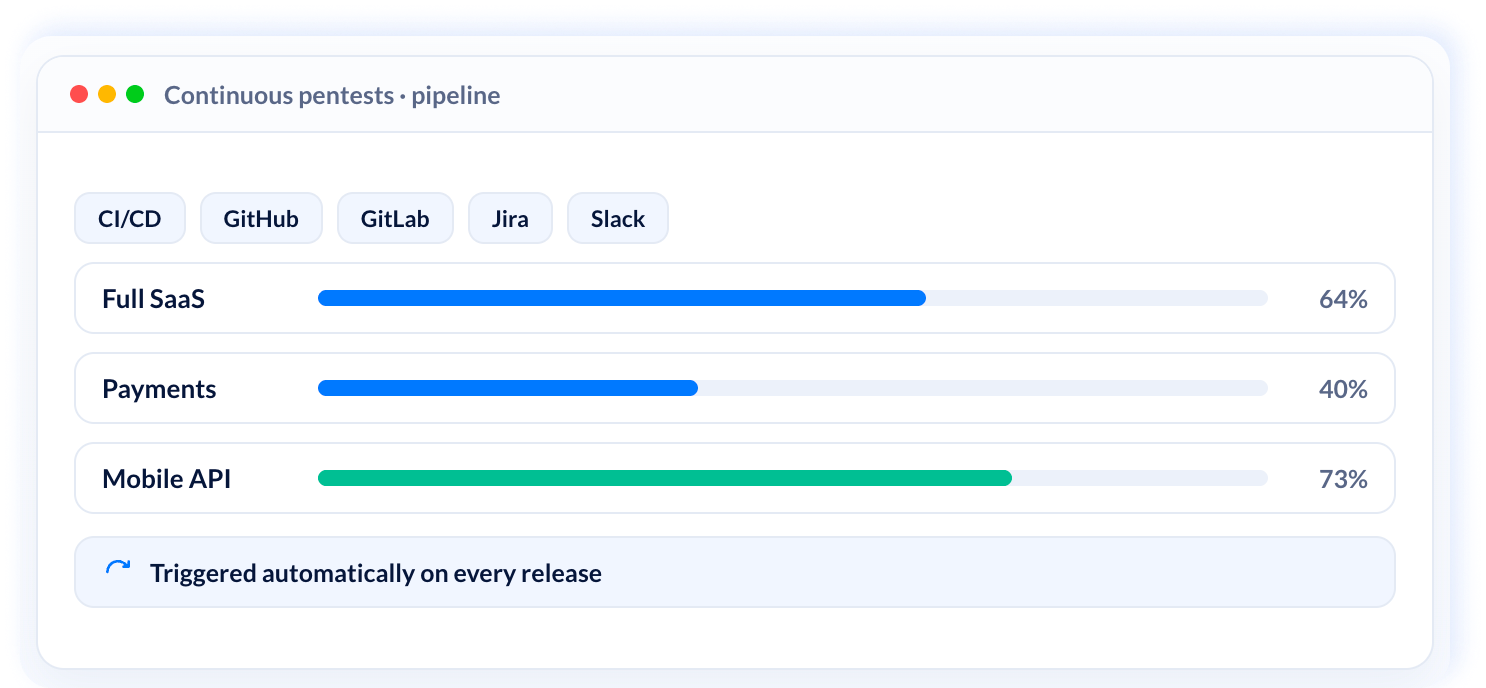
Continuous scanning plugged into CI/CD, GitHub, GitLab, Jira, and Slack
to catch vulnerabilities before you ship.
Support from a dedicated account manager and re-test vulnerabilities to
confirm remediation.
One pentest partner for every attack surface
Autonomous Pentesting
Continuous Pentesting (PTaaS)
DAST Vulnerability Scanner
API Security Platform
Mobile (iOS and Android)
Cloud Scanner
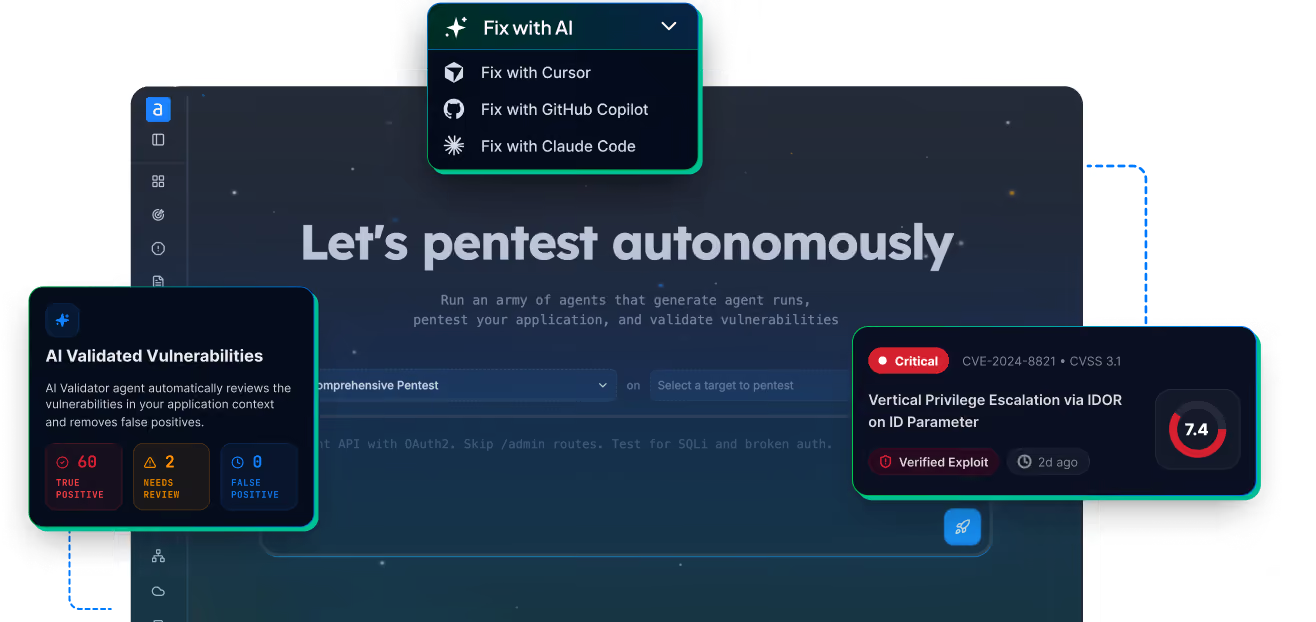
Deploy AI agents trained on 10M+ vulnerabilities to map web apps and APIs, build threat models, uncover business logic flaws, and chain exploits
Get your first finding in under a minute. No setup, no scope calls. Every finding validated before it reaches you.
Pentest every new feature at your dev speed, integrated into CI/CD, GitHub, GitLab, Jira, and Slack
Test across web apps, cloud infra, mobile apps, APIs, and source code
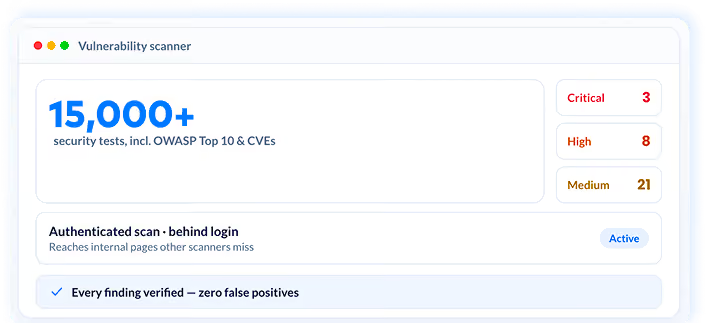
Scan for 10,000+ vulnerabilities including OWASP Top 10, CVEs, and broken access control, with authenticated scans behind login screens
Eliminate false positives with every finding verified by a certified engineer before it reaches you
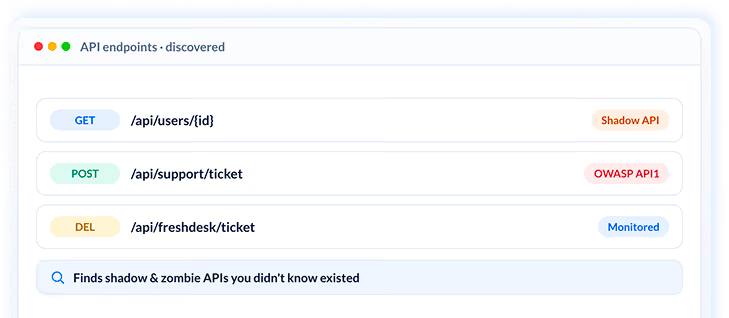
Discover shadow, zombie, and undocumented APIs and scan for OWASP API Top 10, broken access control, and CVEs
Monitor continuously with Jira, Slack, and CI/CD integrations
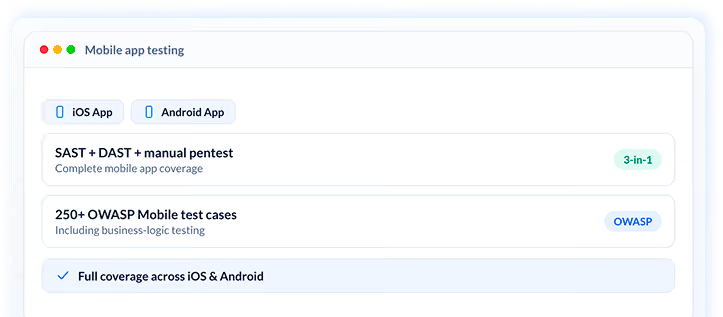
Combine SAST, DAST, and manual pentesting for complete mobile app coverage
Cover 250+ test cases based on OWASP Mobile Top 10, including business logic testing
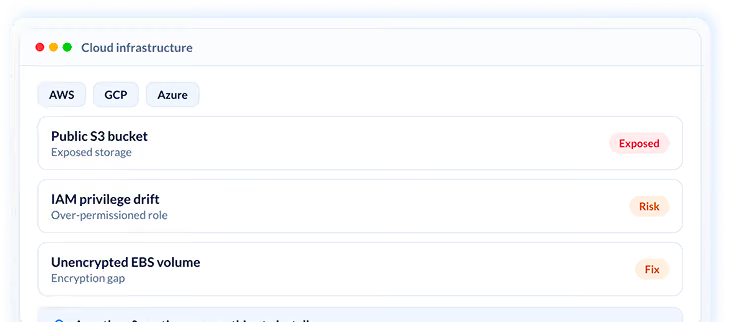
Detect misconfigurations and risks across AWS, GCP, and Azure, agentless and continuous
Check for IAM drift, exposed storage, insecure encryption, network, and logging gaps
Our pentesting services combine manual testing with automated scanning to help you find
and remediate real-world vulnerabilities faster.


We don’t just find vulnerabilities; we help businesses eliminate risks before they become costly breaches.


Offensive DAST vulnerability scanner that scans behind login for 15,000+
test cases like OWASP Top 10, ports, CVEs & more


Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, IP, website, API etc.
If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.
You get 5 target slots, with the ability to change targets in those slots with a 30-day cooling period. Example: Scan 5 targets, after 30 days scan 5 new targets.
Target Explained: Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, website, API etc. If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, IP, website, API etc.
If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.
You get 5 target slots, with the ability to change targets in those slots with a 30-day cooling period. Example: Scan 5 targets, after 30 days scan 5 new targets.
Target Explained: Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, website, API etc. If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.
Hacker-style pentest by Autonomous AI & certified experts at dev speed, built to meet & exceed
SOC2, ISO, & HIPAA requirement
One web or SaaS app counts as one target, including all APIs consumed.
Mobile is per platform, so an Android app and an iOS app are two targets
Networks, cloud, IPs and standalone APIs are 1 target each


One web or SaaS app counts as one target, including all APIs consumed.
Mobile is per platform, so an Android app and an iOS app are two targets
Networks, cloud, IPs and standalone APIs are 1 target each

Weekly vulnerability scans with 3000+ tests (OWASP, SANS etc.)
Essential features like pentest dashboard, PDF reports and scan behind login
Continuously discover & scan every API in your infrastructure for broken access control, authorization flaws, OWASP Top 10 & more
Astra continuously scans AWS, Azure, and GCP for misconfigs, IAM risks, and vulnerabilities, validating every finding before it reaches you
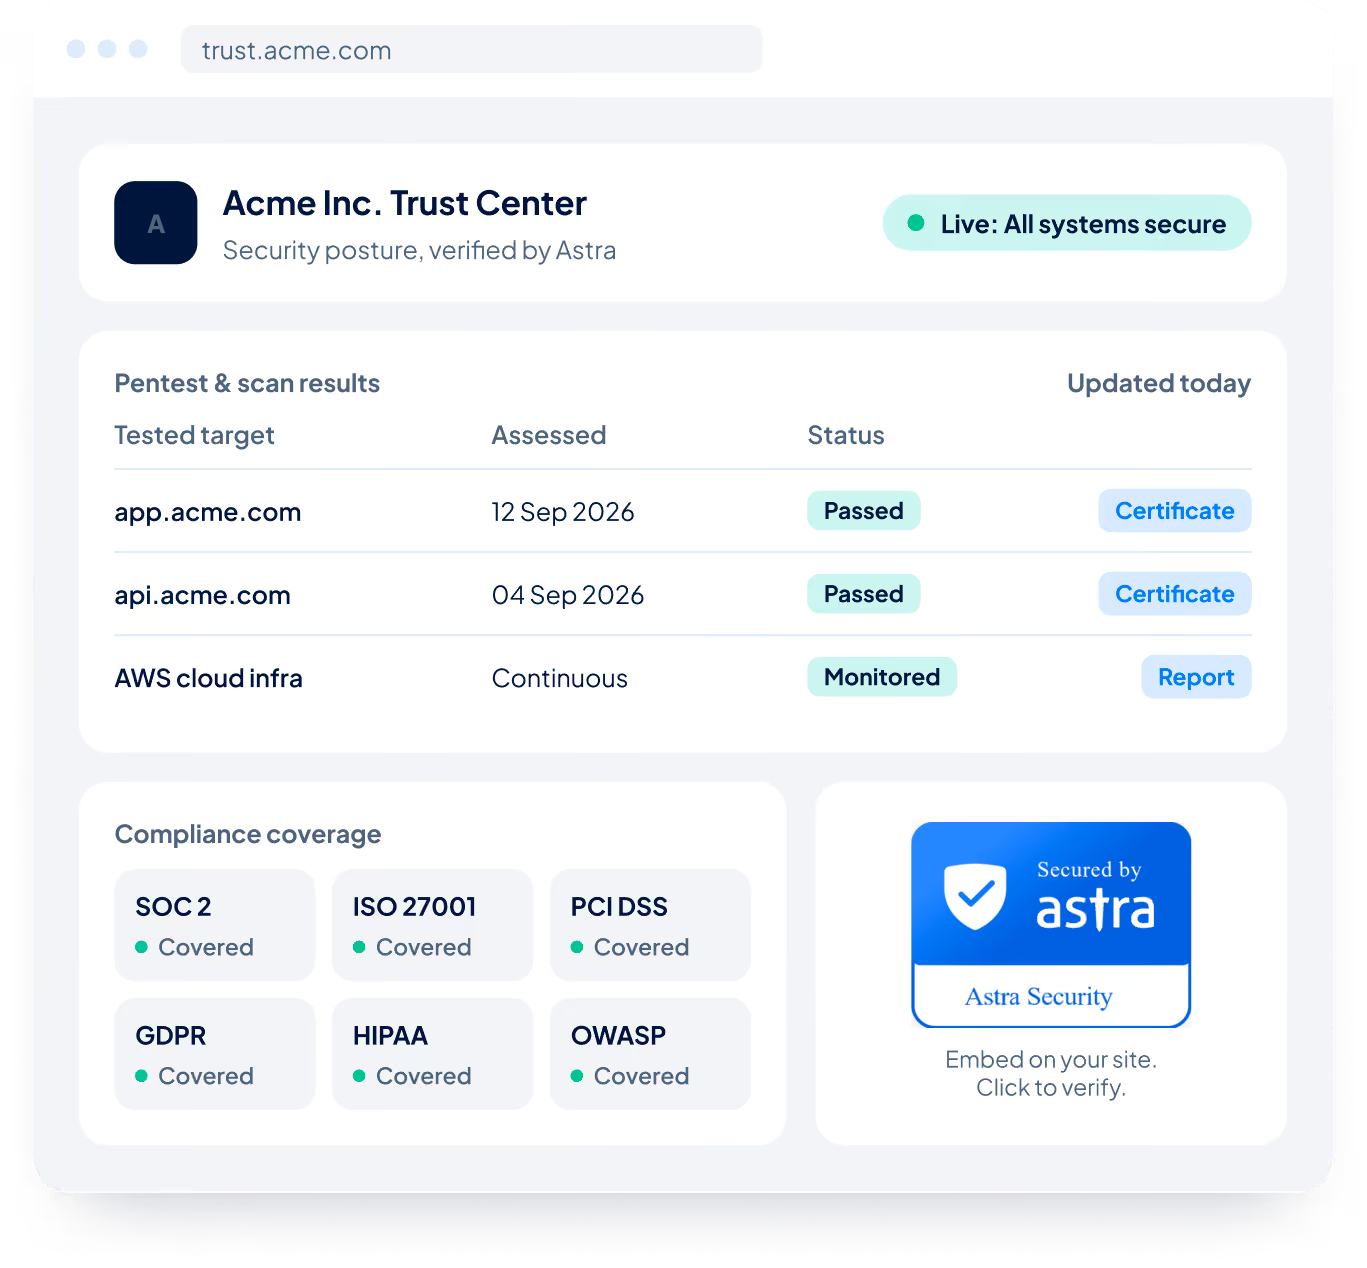
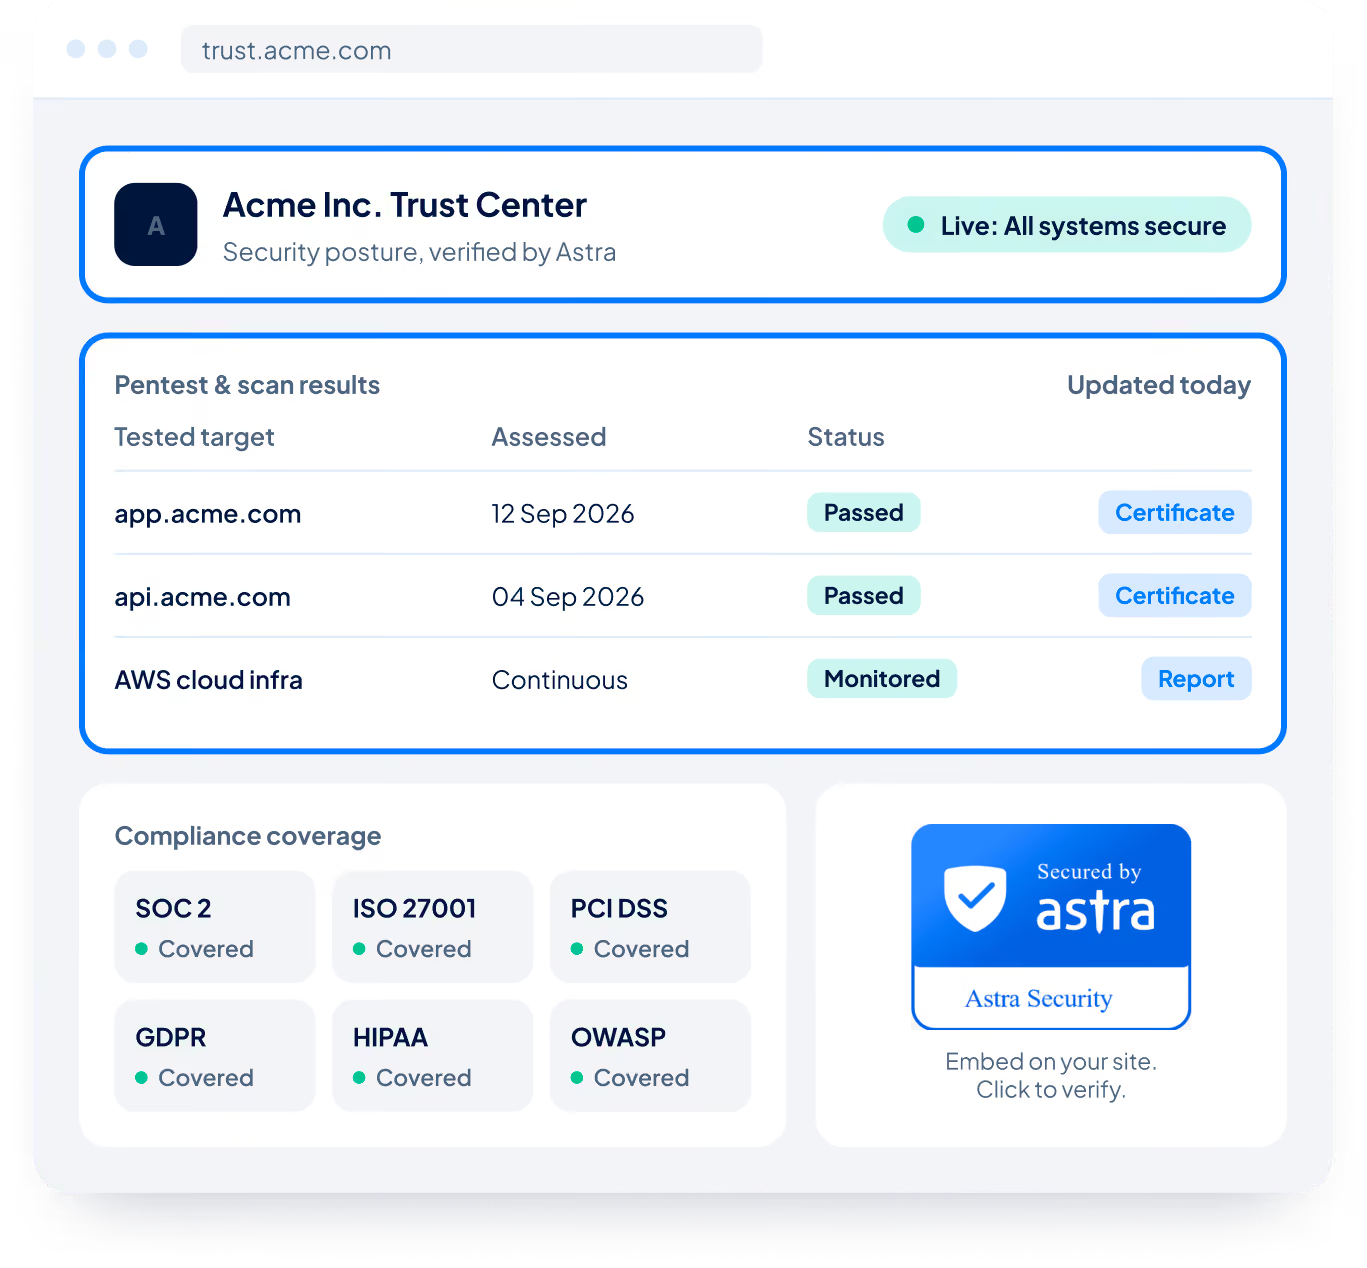
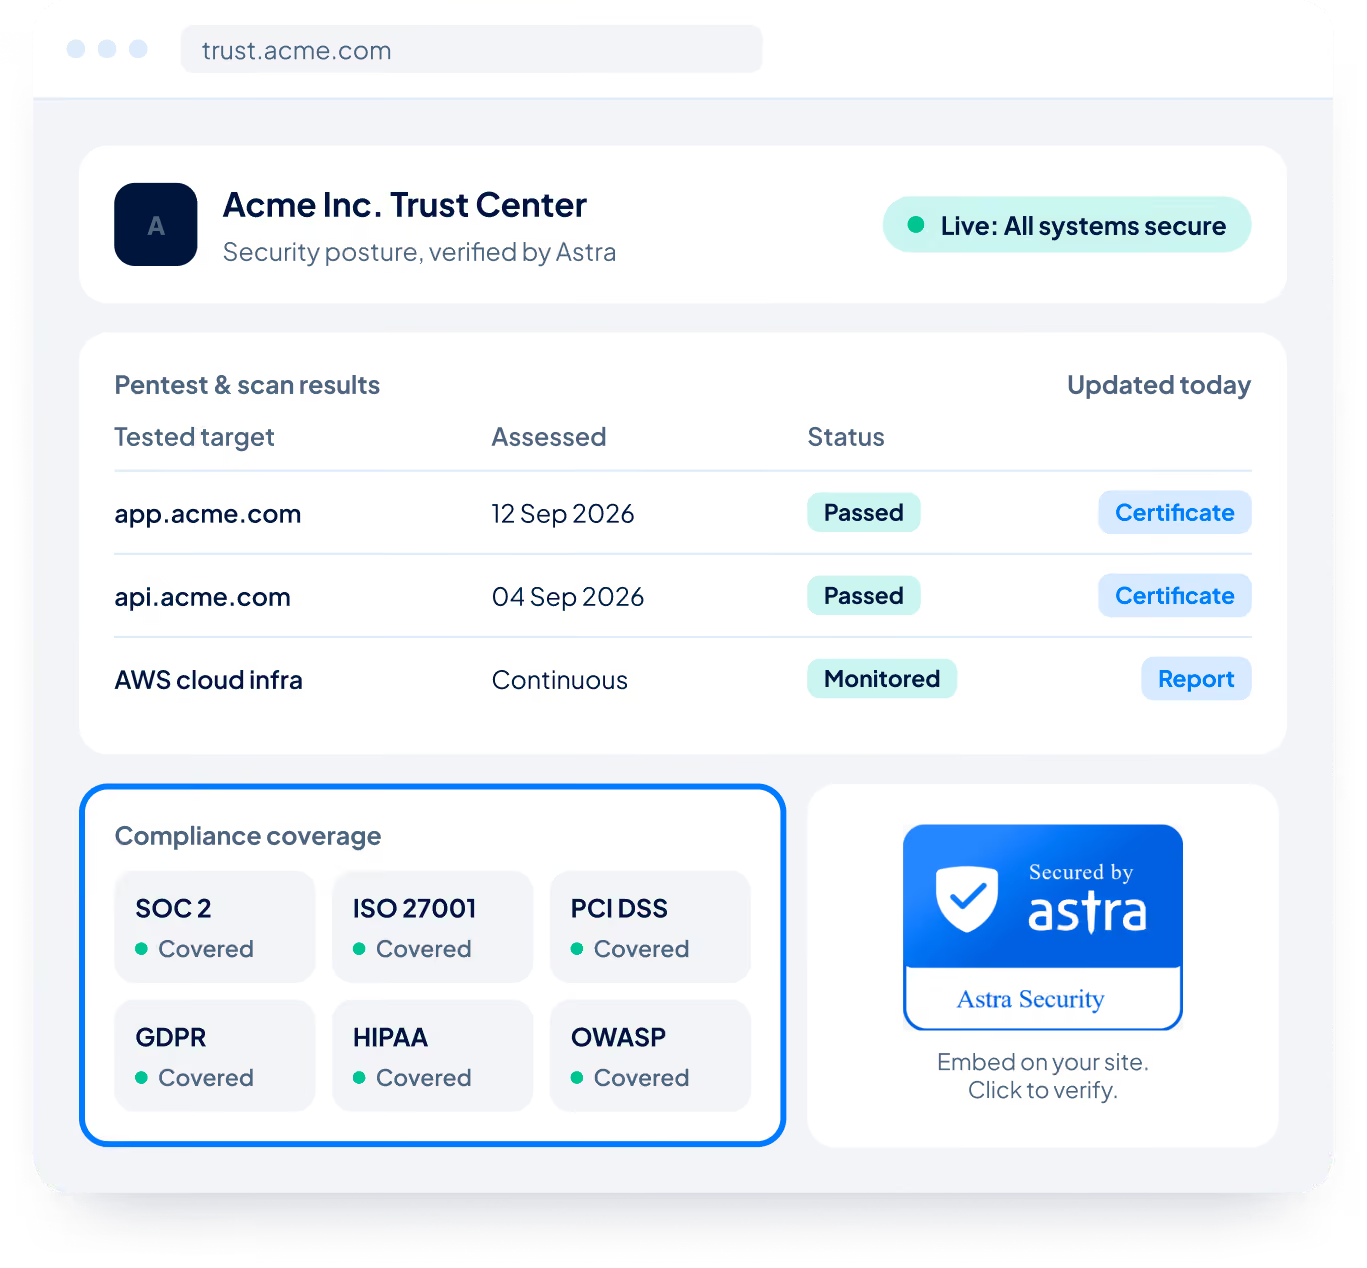
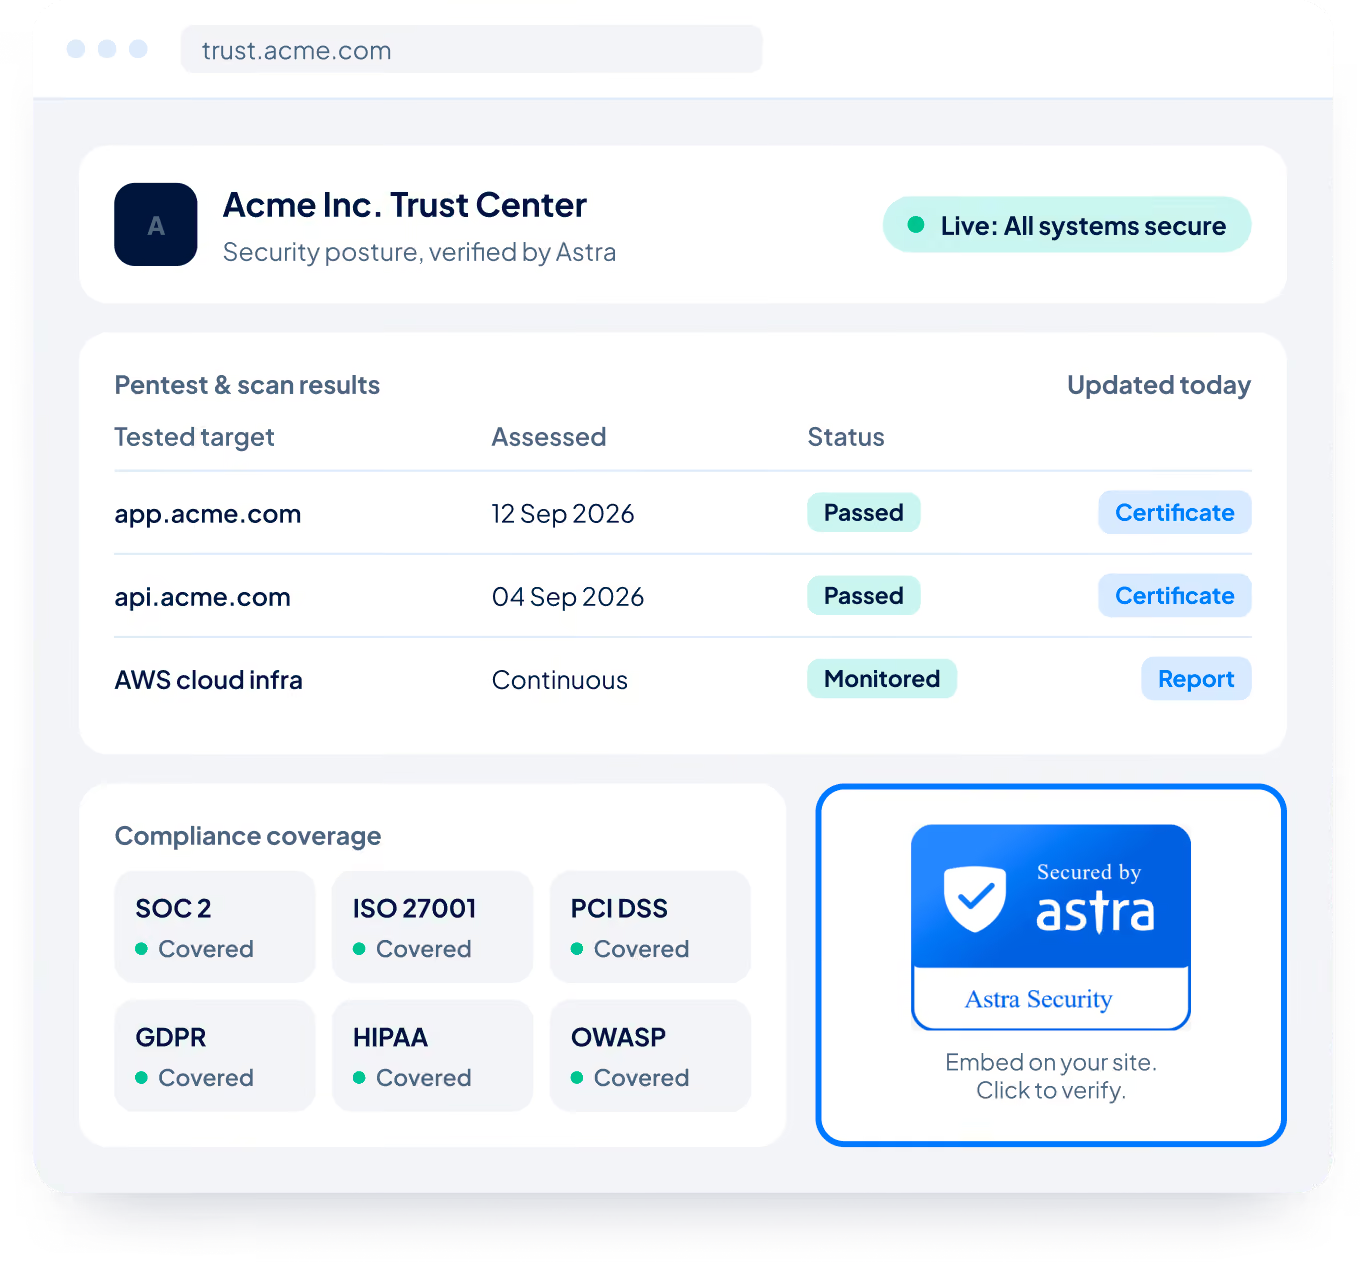
A dedicated Trust Center
Pentest proof and scan results
Compliance coverage
Branded Trust Center and Trust Seal
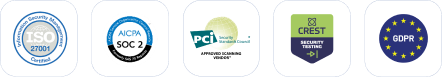
Astra meets global standards with accreditations from



We are impressed by Astra's commitment to continuous rather than sporadic testing.


Astra not only uncovers vulnerabilities proactively but has helped us move from DevOps to DevSecOps


Their website was user-friendly & their continuous vulnerability scans were a pivotal factor in our choice to partner with them.


The combination of pentesting for SOC 2 & automated scanning that integrates into our CI pipelines is a game-changer.


I like the autonomy of running and re-running tests after fixes. Astra ensures we never deploy vulnerabilities to production.


We are impressed with Astra's dashboard and its amazing ‘automated and scheduled‘ scanning capabilities. Integrating these scans into our CI/CD pipeline was a breeze and saved us a lot of time.


Sharing a detailed pentest report is never a great idea. Now we have a way to share a certificate with our customers.
Astra Security’s responsive team and comprehensive testing helped us achieve compliance faster, uncover hidden vulnerabilities, and simplify remediation. Their verifiable pentest certificate gives us confidence our systems are secure.
We are impressed by Astra's commitment to continuous rather than sporadic testing.
Astra not only uncovers vulnerabilities proactively but has helped us move from DevOps to DevSecOps
Their website was user-friendly & their continuous vulnerability scans were a pivotal factor in our choice to partner with them.
The combination of pentesting for SOC 2 & automated scanning that integrates into our CI pipelines is a game-changer.
I like the autonomy of running and re-running tests after fixes. Astra ensures we never deploy vulnerabilities to production.
We are impressed with Astra's dashboard and its amazing ‘automated and scheduled‘ scanning capabilities. Integrating these scans into our CI/CD pipeline was a breeze and saved us a lot of time.

Sharing a detailed pentest report is never a great idea. Now we have a way to share a certificate with our customers.
Astra Security’s responsive team and comprehensive testing helped us achieve compliance faster, uncover hidden vulnerabilities, and simplify remediation. Their verifiable pentest certificate gives us confidence our systems are secure.