Audit-ready reports in hours for DORA, GDPR, ISO 27001, SOC 2, and PCI-DSS. Compliance gap mapping included.
No false positives. Every finding verified by a CREST-certified expert with video PoC, impact context, and clear remediation guidance.
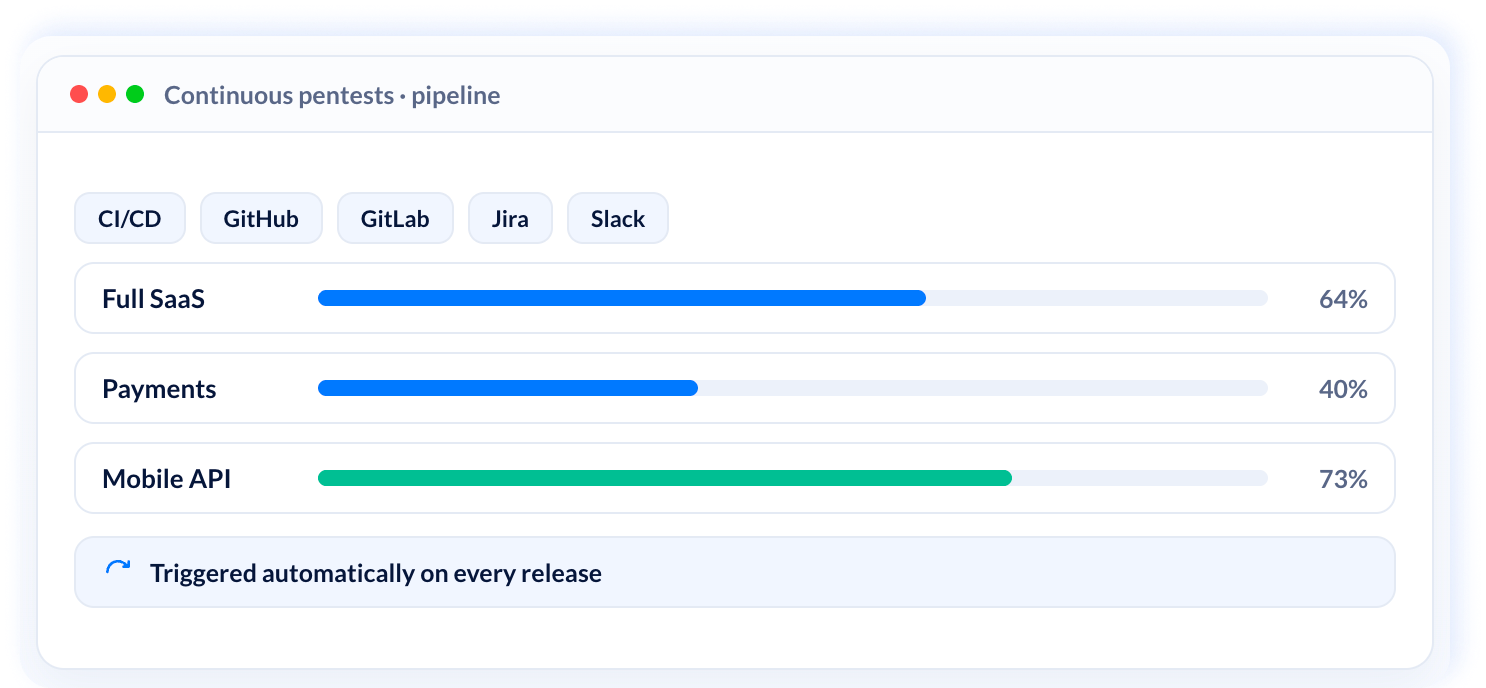
Continuous scanning plugged into CI/CD, GitHub, GitLab, Jira, and Slack to catch vulnerabilities before you ship.
Support from a dedicated account manager and re-test vulnerabilities to confirm remediation.
One pentest partner for every attack surface
Autonomous Pentesting
Continuous Pentesting (PTaaS)
DAST Vulnerability Scanner
API Security Platform
Mobile (iOS and Android)
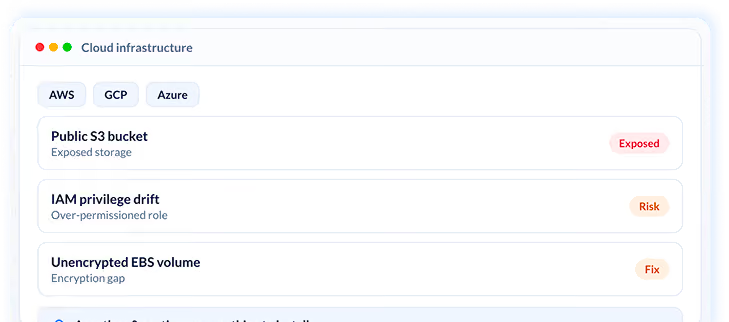
Cloud Scanner
Deploy AI agents trained on 10M+ vulnerabilities to map web apps and APIs, build threat models, uncover business logic flaws, and chain exploits
Get your first finding in under a minute. No setup, no scope calls. Every finding validated before it reaches you.
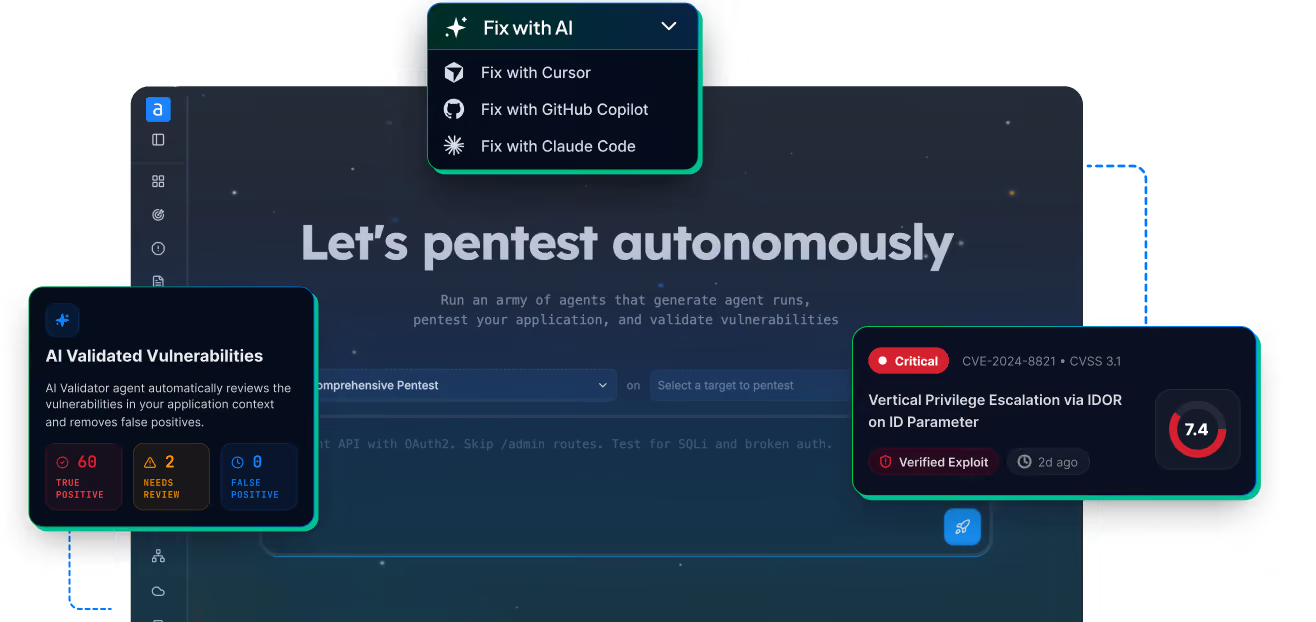
Pentest every new feature at your dev speed, integrated into CI/CD, GitHub, GitLab, Jira, and Slack
Test across web apps, cloud infra, mobile apps, APIs, and source code
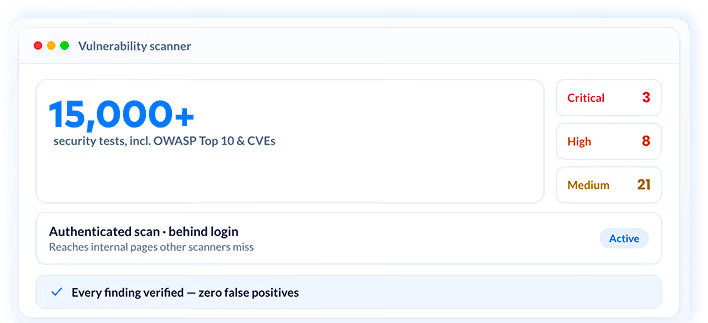
Scan for 10,000+ vulnerabilities including OWASP Top 10, CVEs, and broken access control, with authenticated scans behind login screens
Eliminate false positives with every finding verified by a certified engineer before it reaches you
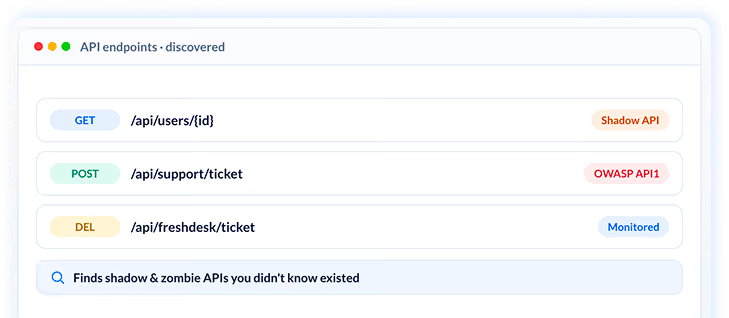
Discover shadow, zombie, and undocumented APIs and scan for OWASP API Top 10, broken access control, and CVEs
Monitor continuously with Jira, Slack, and CI/CD integrations
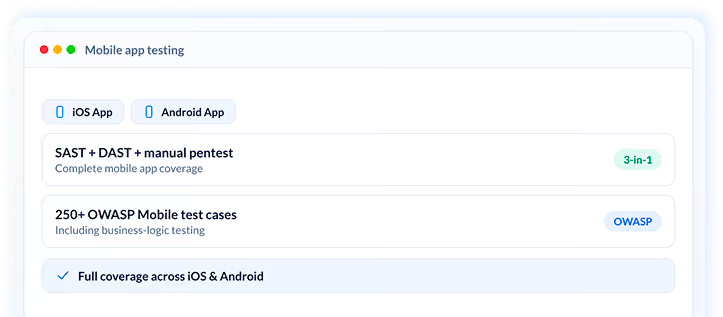
Combine SAST, DAST, and manual pentesting for complete mobile app coverage
Cover 250+ test cases based on OWASP Mobile Top 10, including business logic testing
Detect misconfigurations and risks across AWS, GCP, and Azure, agentless and continuous
Check for IAM drift, exposed storage, insecure encryption, network, and logging gaps
Our pentesting services combine manual testing with automated scanning to help you find
and remediate real-world vulnerabilities faster.


We don’t just find vulnerabilities; we help businesses eliminate risks before they become costly breaches.


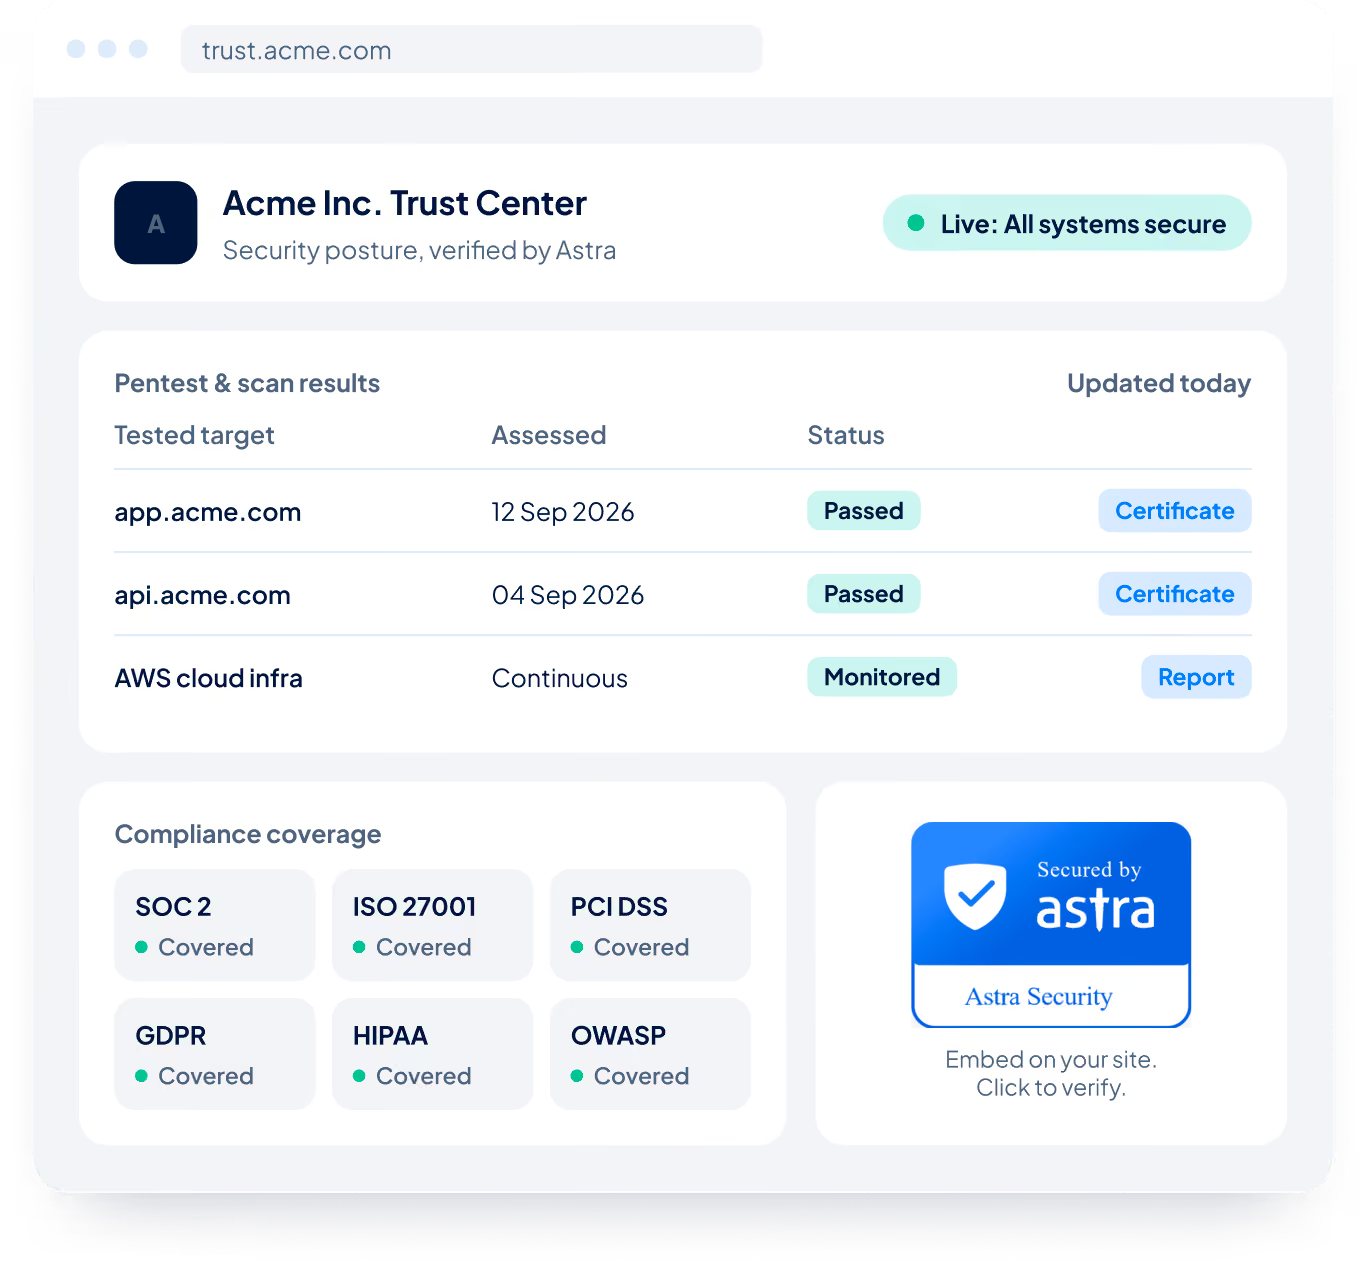
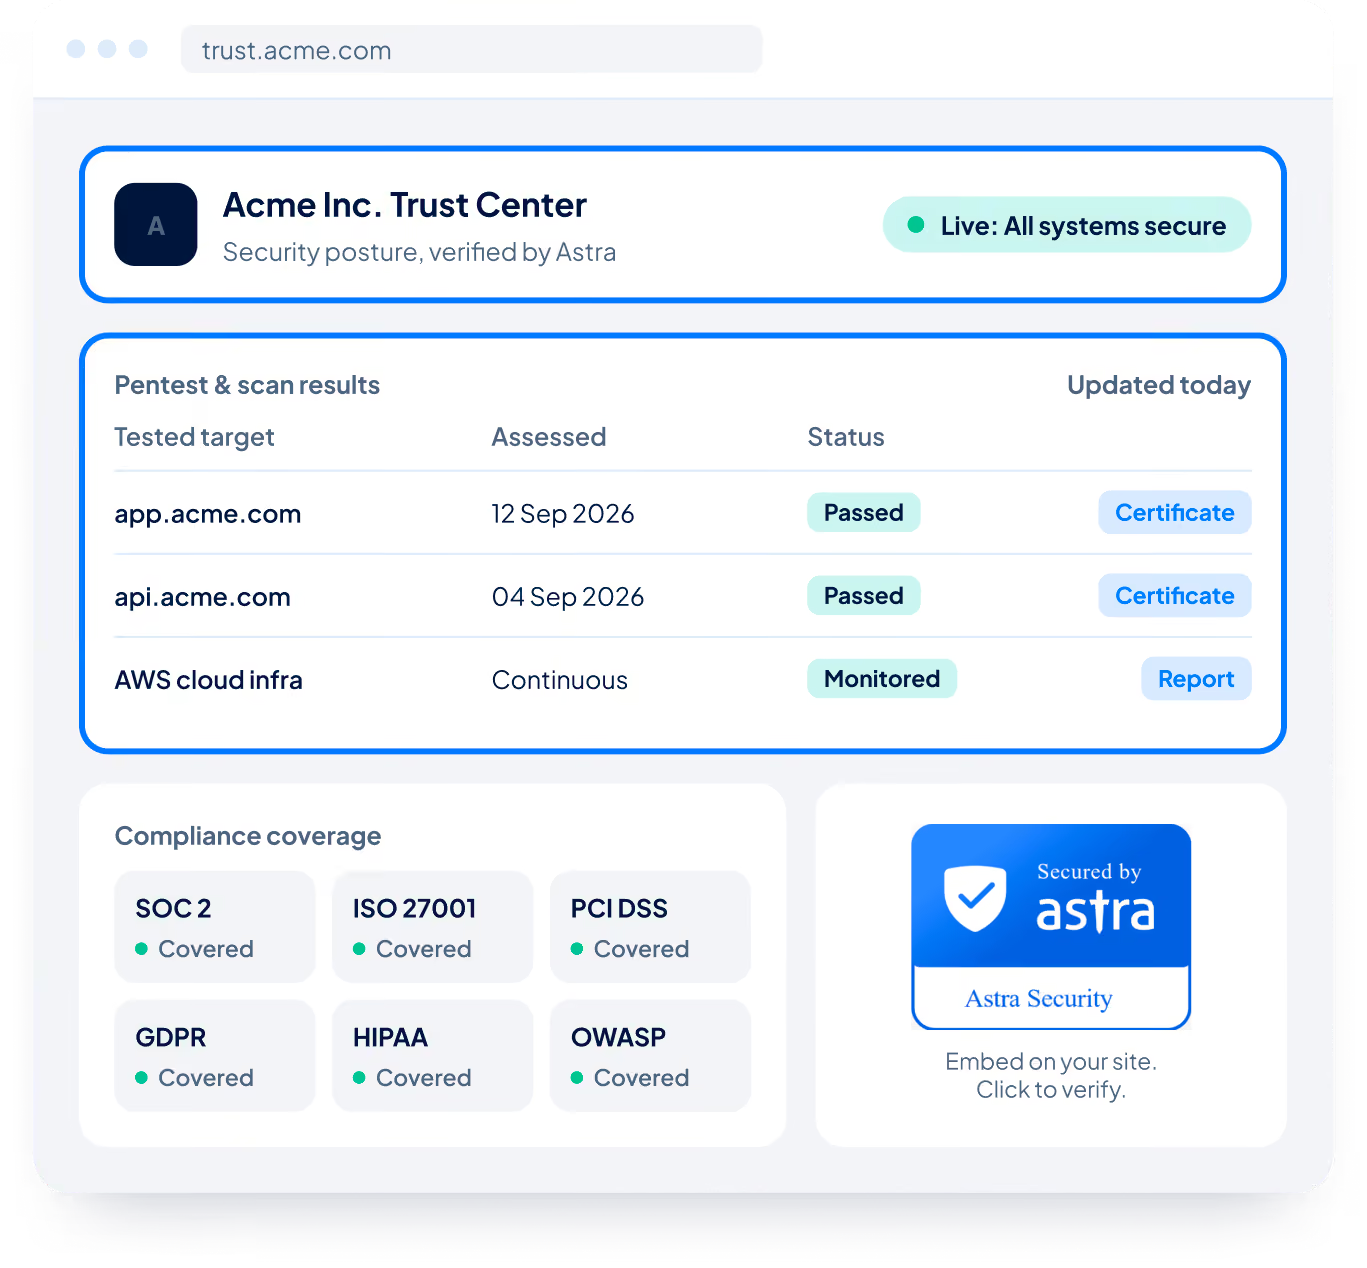
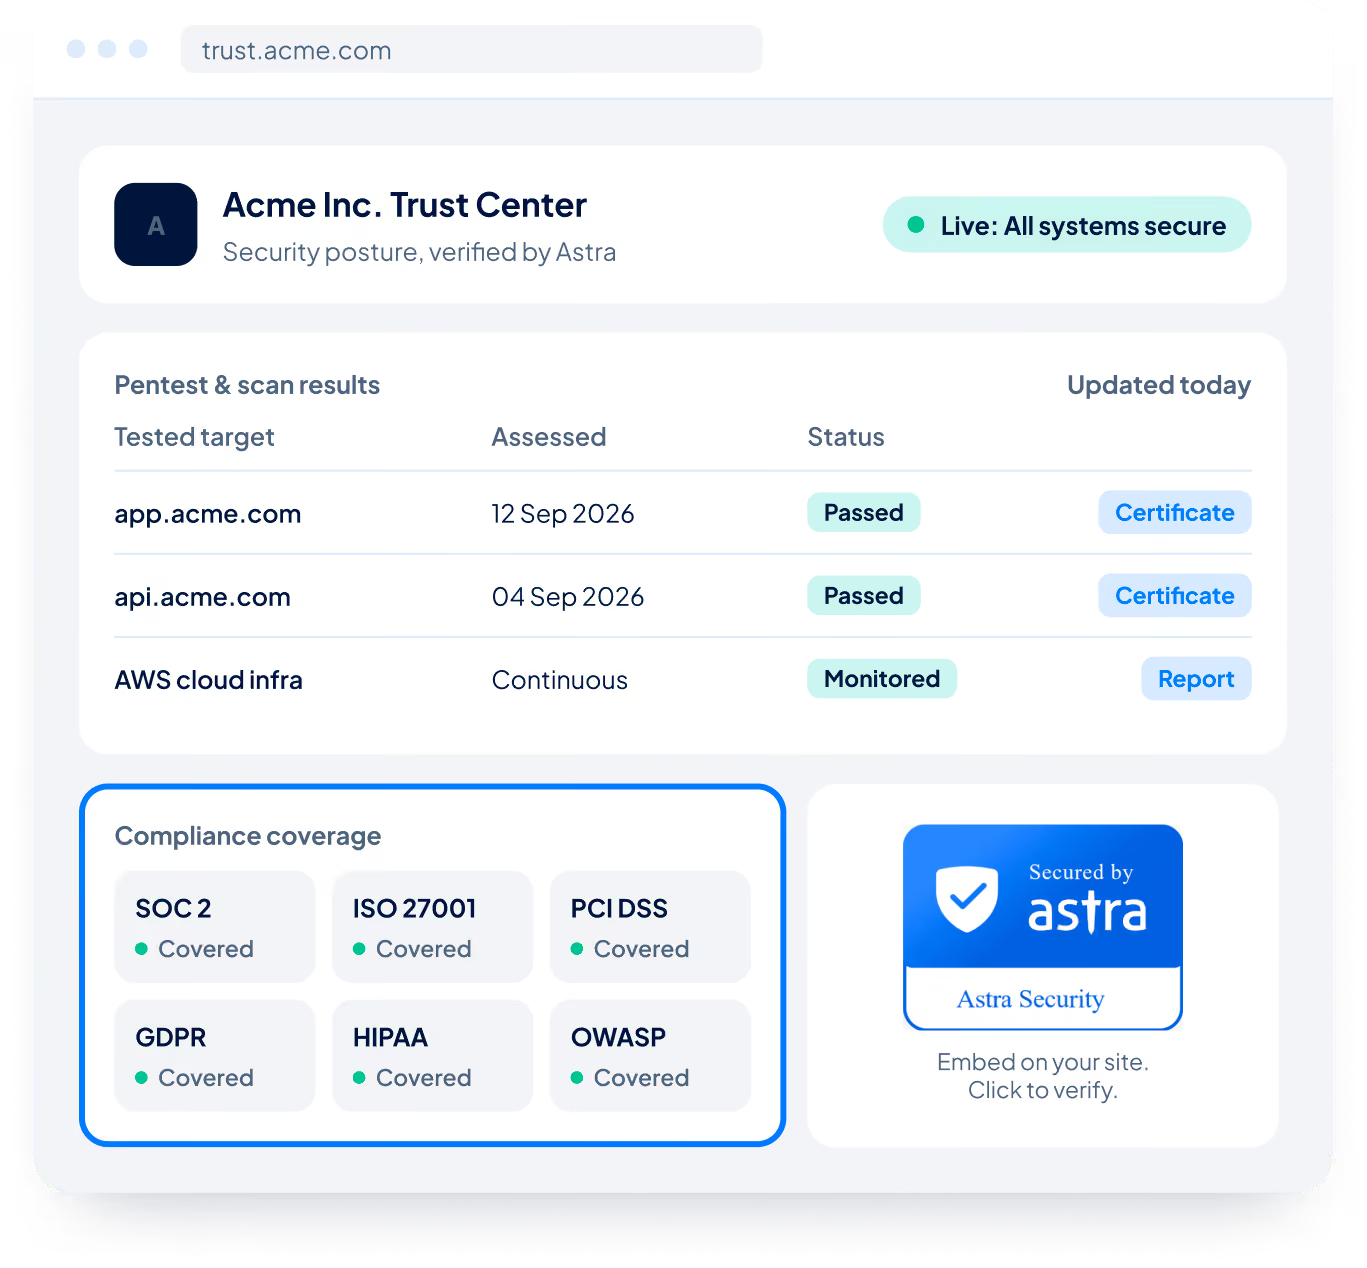
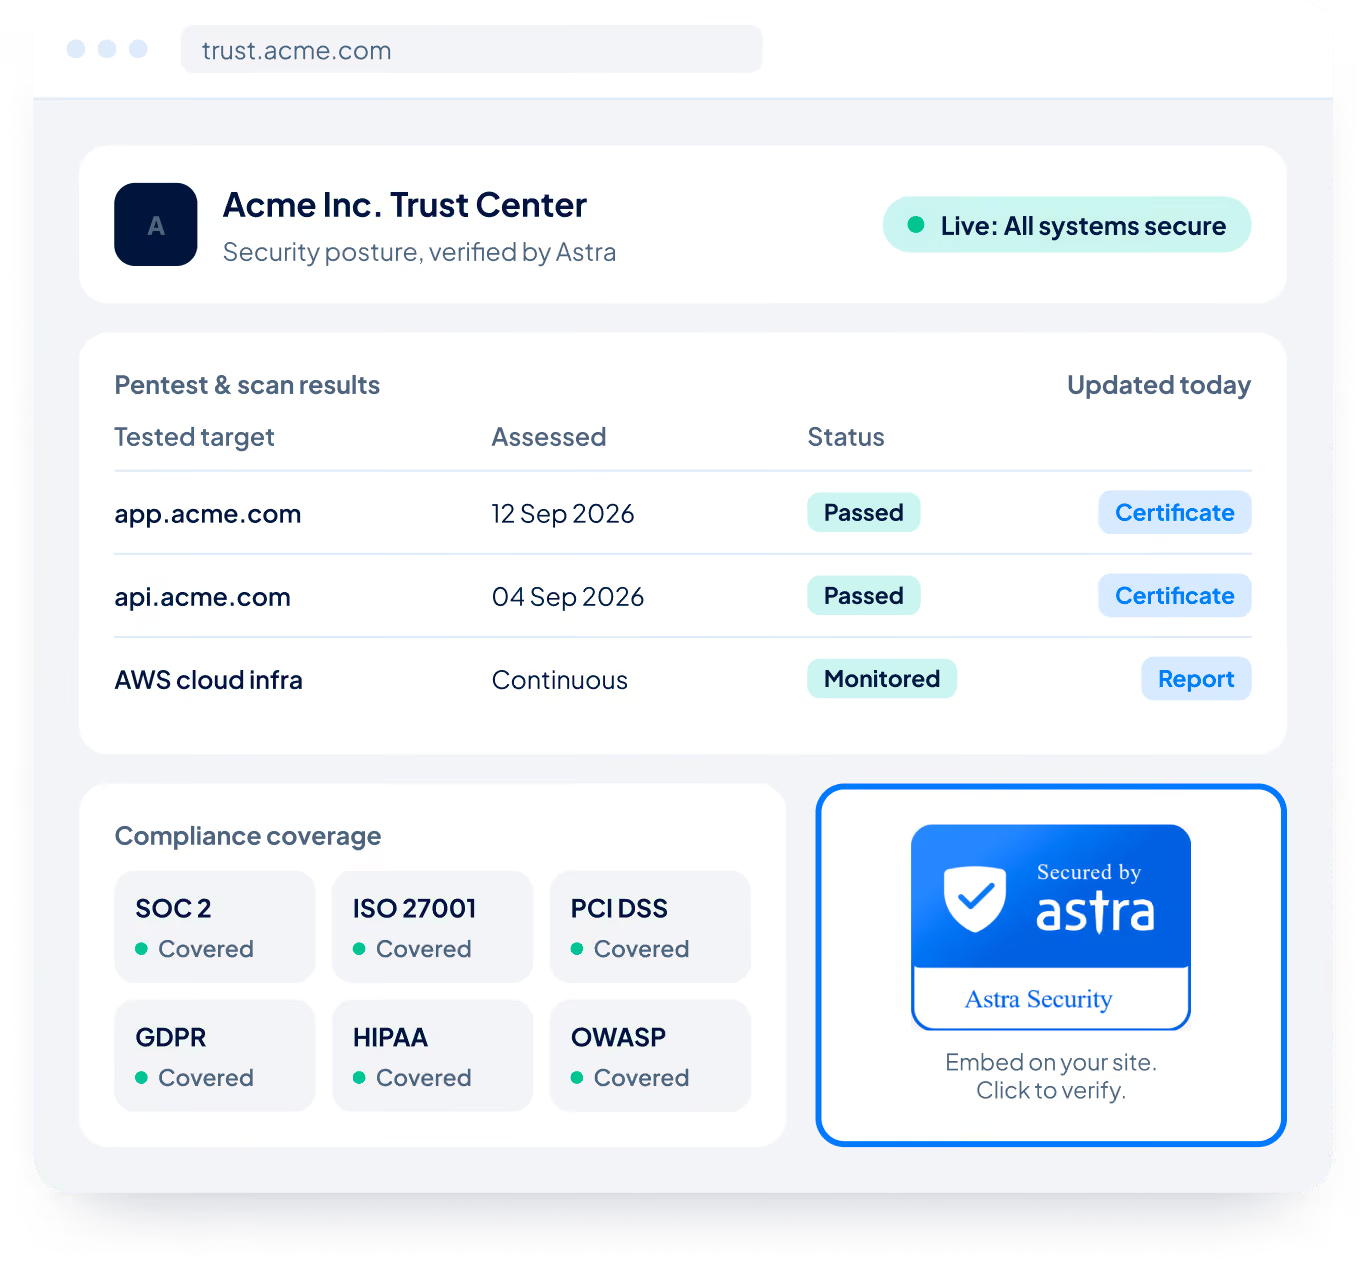
A dedicated Trust Center
A dedicated Trust Center
A dedicated Trust Center
A dedicated Trust Center
Generate in-depth vulnerability reports with detailed
steps for remediation and lightning-fast custom formats for execs & developers.
Astra meets global standards with accreditations from



We are impressed by Astra's commitment to continuous rather than sporadic testing.


Astra not only uncovers vulnerabilities proactively but has helped us move from DevOps to DevSecOps


Their website was user-friendly & their continuous vulnerability scans were a pivotal factor in our choice to partner with them.


The combination of pentesting for SOC 2 & automated scanning that integrates into our CI pipelines is a game-changer.


I like the autonomy of running and re-running tests after fixes. Astra ensures we never deploy vulnerabilities to production.


We are impressed with Astra's dashboard and its amazing ‘automated and scheduled‘ scanning capabilities. Integrating these scans into our CI/CD pipeline was a breeze and saved us a lot of time.


We are impressed by Astra's commitment to continuous rather than sporadic testing.
Astra not only uncovers vulnerabilities proactively but has helped us move from DevOps to DevSecOps
Their website was user-friendly & their continuous vulnerability scans were a pivotal factor in our choice to partner with them.
The combination of pentesting for SOC 2 & automated scanning that integrates into our CI pipelines is a game-changer.
I like the autonomy of running and re-running tests after fixes. Astra ensures we never deploy vulnerabilities to production.
We are impressed with Astra's dashboard and its amazing ‘automated and scheduled‘ scanning capabilities. Integrating these scans into our CI/CD pipeline was a breeze and saved us a lot of time.