

Best cloud security posture management (CSPM) solution
Astra’s CSPM tool redefines how you secure AWS, Azure, and GCP. Detect risks faster.
Validate them instantly. Prove your security continuously.


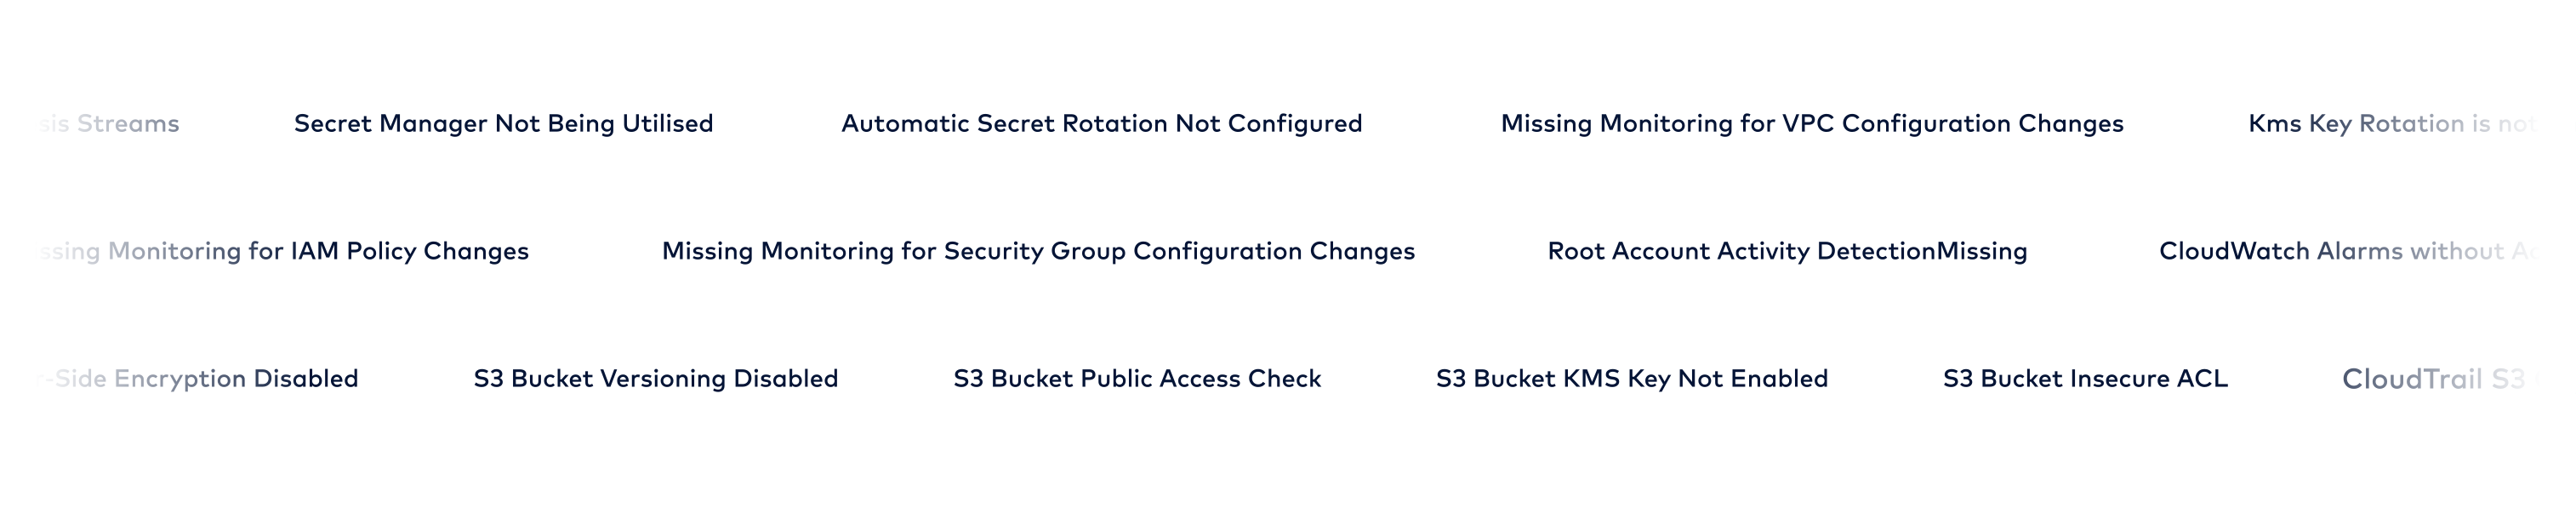
Your cloud evolves in minutes.
Most CSPM tools don’t.
Every new commit, IAM role, or container shifts your security posture. But most teams only learn
about those shifts days, sometimes weeks later.
CSPM software dashboards display snapshots of yesterday’s risks, but your infrastructure has already changed. Alerts pile up. Context is lost. Teams are stuck chasing ghosts instead of real issues.

45%
of critical misconfigurations appear after deployment.
62%
of organizations experience posture drift within just 24 hours of a change.
71%
of security teams spend more time revalidating fixes than actually fixing them.
The result? A security posture that appears “green” but isn’t, and teams that struggle to prove what’s truly safe.
Traditional CSPM Solutions Vs Astra CSPM
Don’t just find risks. Validate them.
Fix them. Prove them.
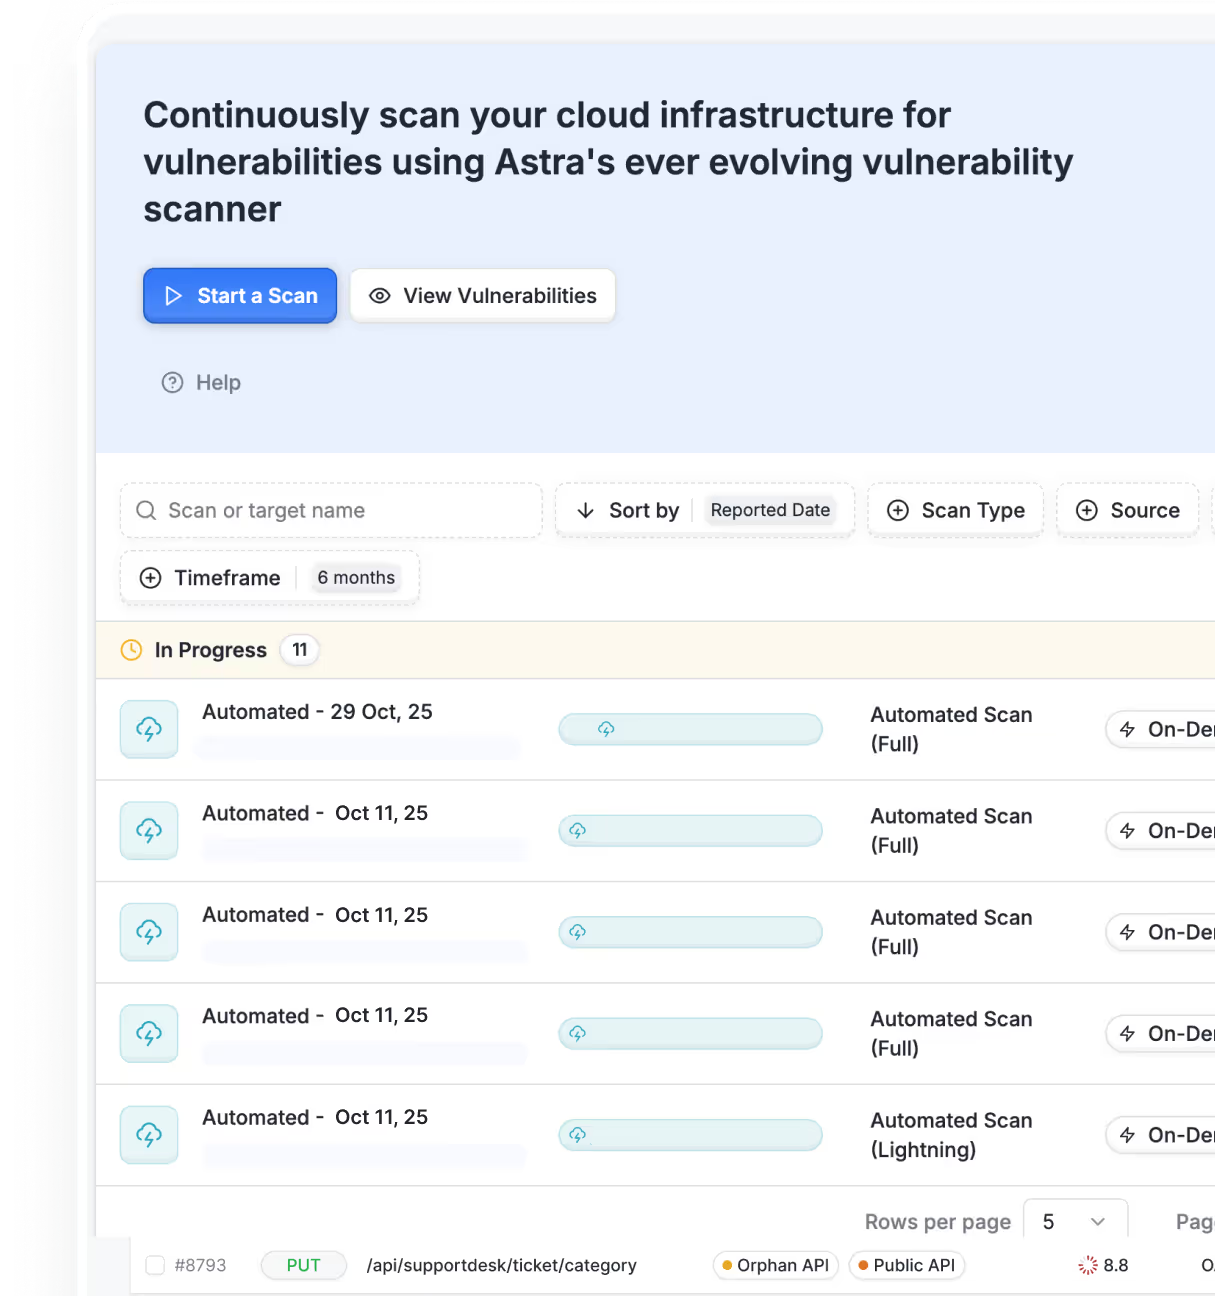
Astra’s CSMP tool continuously validates replacing noisy rule-based posture scans with a four-step offensive model:
Assets, misconfigs, IAM policies, and exposures across AWS, Azure, and GCP.
Simulate hacker behavior to confirm real exploit paths.
Create compliance-mapped, proof-driven insights instantly.
Guide fixes and re-validate automatically.
Other CSPMs solutions tell you posture.
Astra shows you proof.
We don’t just list alerts, we validate what’s real. Astra’s CSPM tool's offensive-first engine runs
beyond rule-based posture checks to confirm what attackers can actually exploit.
Continuous posture check
Validates findings through real exploit simulation.
Multi-cloud coverage
AWS, Azure, and GCP in one unified view.
Actionable guidance
Context, impact, and fix steps included.
Auto-validation
Every fix is rechecked automatically, with no manual effort.
Unified security
Integrates cloud, API, and web scanning under one suite.

What stands out to me about Astra is its accuracy.
The cloud security scanner significantly reduces
false positives, integrates smoothly into CI/CD
pipelines and helps teams remediate real cloud
risks without slowing deployments, which is a major
time saver for security engineering teams

What I love is the clarity. Other tools tell you a
hundred things might be wrong. Astra’s cloud
vulnerability scanner tells you the five things that
actually matter and proves it. Our cloud security
posture finally feels manageable.

Astra makes cloud security feel
straightforward again. You open the
dashboard and instantly see what matters:
real findings, real context, real fixes.

What security experts say
See how Astra Cloud Vulnerability Scanner is helping
security teams cut through the noise and focus on what matters
Cloud breaches aren’t complex;
they’re overlooked. Astra helps
teams identify and resolve real
misconfigurations early.

Astra combines agentless scanning with 400+ offensive
security checks to validate real risks. It flags IAM drift,
privilege bloat, and storage issues that truly matter to cloud
security teams.
Astra’s Cloud Vulnerability Scanner focuses on what truly
matters: visibility, posture, and proactive risk reduction.
Simple dashboard, real-time insights, and strong security
fundamentals.
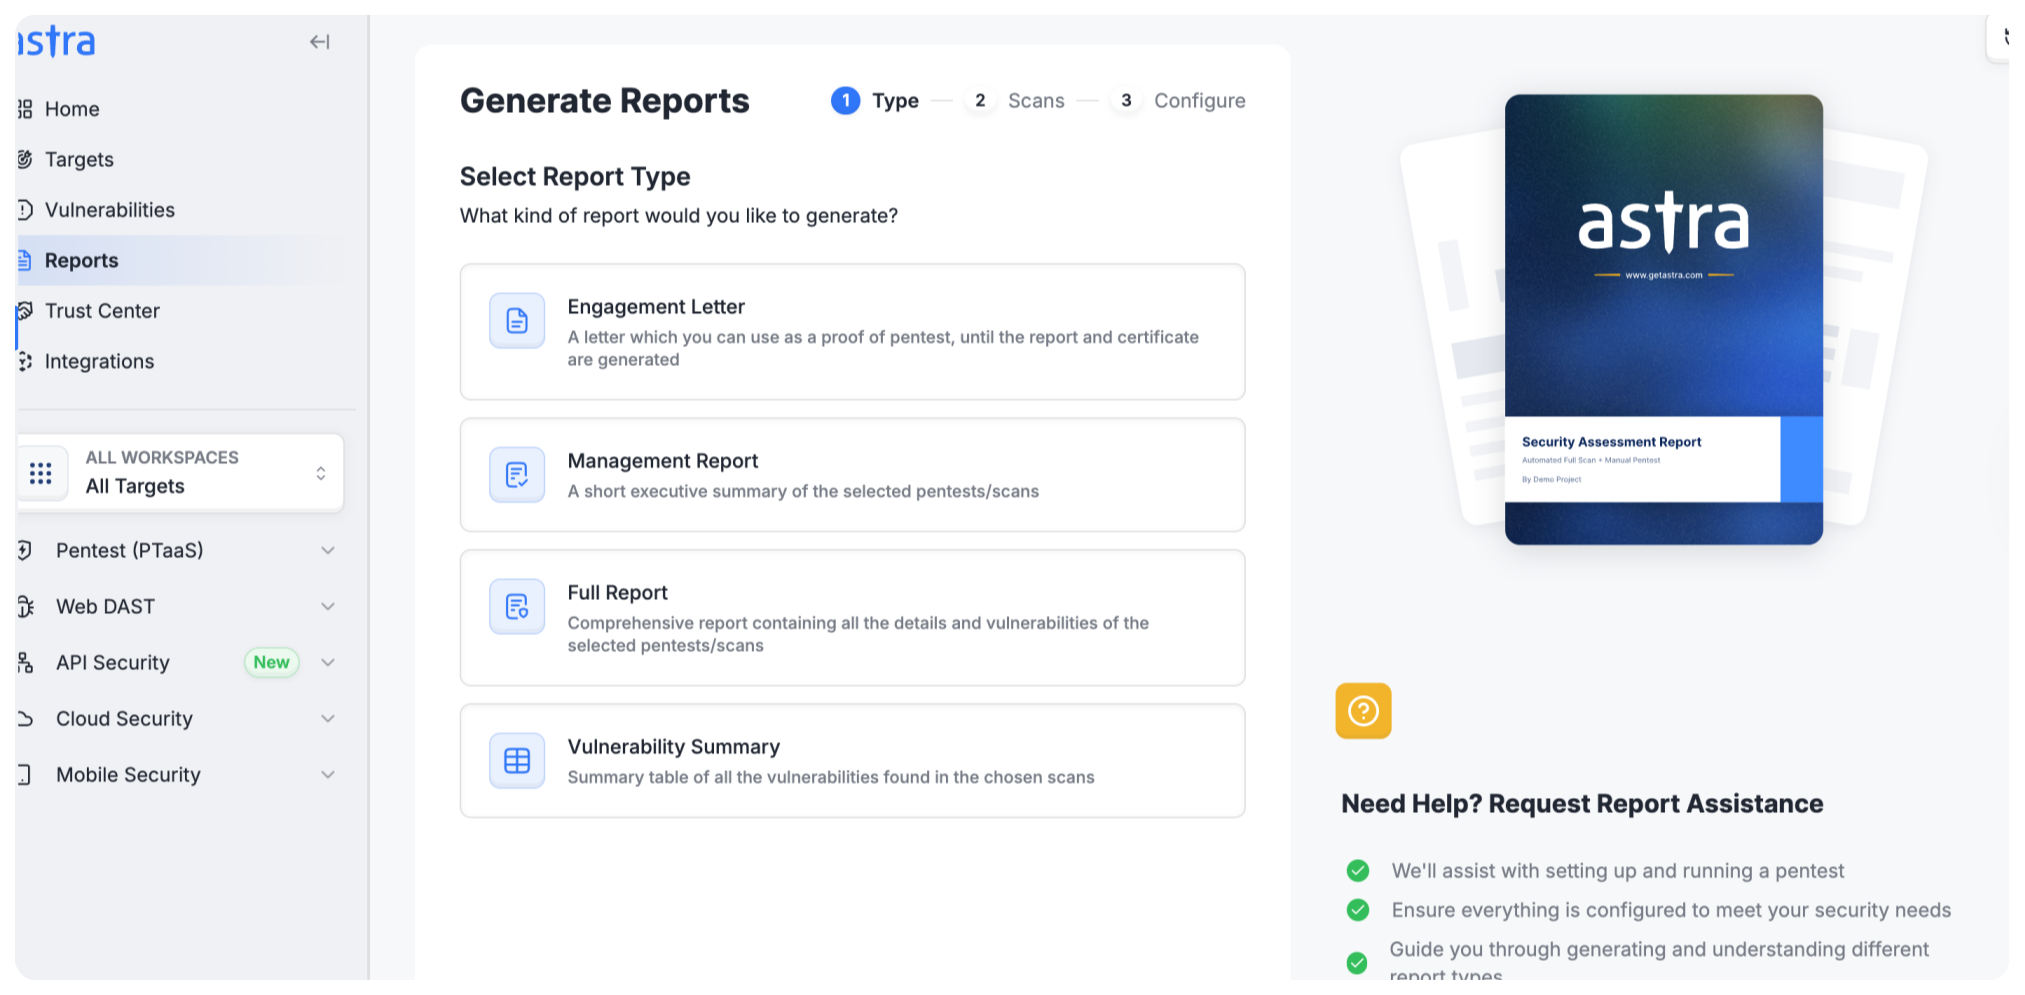
Trust our reports for accuracy and audit readiness.
No more static compliance PDFs. Astra transforms your scans into living evidence with the Trust Center,
which provides continuously updated reports that are proof-verified and mapped to
CIS, SOC2, ISO 27001, and more.
Your CSPM tool shouldn't stand alone.
Astra CSPM solution is part of a broader ecosystem alongside DAST, API, and PTaaS, giving you complete visibility across applications, APIs, and cloud infrastructure from one dashboard.


Frequently asked questions
What is Astra Cloud Vulnerability Scanner, and how is it different from traditional CSPM tools?
How accurate are the findings? Will it generate false positives?
Can Astra CSPM tool help with compliance and security reporting?
Does Astra support multi-cloud environments?
Yes. Astra continuously scans AWS, Azure, and GCP from a single dashboard. Whether you’re running one cloud or many, you get unified visibility into misconfigurations, identity risks, and security gaps without managing separate CSPM tools.
Is the scanner agentless, and how long does setup take?
