ASTRA VS BREACHLOCK

Breachlock alternative
that actually fits into
your DevSecOps flow

  • AI-powered continuous scanning and offensive pentesting for web, API, cloud, and mobile assets.

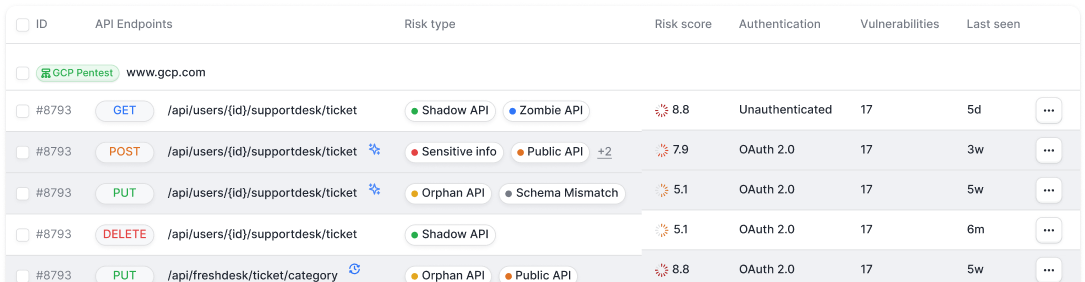
  • Dedicated API Security Platform that discovers, monitors, and classifies shadow, zombie, and orphan APIs.

  • Official PCI Approved Scanning Vendor (ASV)  trusted for PCI-DSS and global compliance validation.

Audit-ready SOC 2 and ISO 27001 pentest reports delivered within hours, starting at $2,999/year.
Trusted by 1000+ modern engineering teams
ROI COMPARISON

ROI Comparison: Astra vs. Breachlock

When comparing Breachlock pricing to Astra, it’s clear that Astra offers deeper security insights, expert-
driven testing, and compliance support—all within a single, predictable pricing structure.

Features
Pricing model
Vulnerability scans
False-positive reduction
Pentesting
Business-logic testing
Cloud Security Review
API security
Integrations & DevSecOps
Enterprise support
Retests / re-scans
Pricing Transparency
Trial access
ASTRA
Fixed, asset-based plans: US $199/mo (DAST) & US $5,999 yr (Pentest)
Unlimited automated DAST scans (10000 + tests) included in every plan
Zero-false-positive guarantee—results manually vetted by expert pentesters; 4 expert-reviewed reports/yr included
Full manual pentest bundled into the US $5,999 plan; CREST-accredited testers

Included in Pentest & Enterprise plans
AWS, GCP & Azure config hardening checks baked into Pentest plans—no up-charge
Dedicated API scanner plus continuous runtime API discovery
Unlimited CI/CD, Jira, Slack, Postman, GitHub, etc., connectors in every tier
Named Customer-Success Manager, shared Slack Connect channel, on-demand expert consults included
Up to 4 free re-scans within 90 days to validate fixes—no subscription lock-in
Public price list & plan comparison page
Free trial/product tour available (DAST scanner & dashboard)
BREACHLOCK
Quote-only; itemised by service (PTaaS, ASM, Red Team, etc.)
 Scans available, but cadence & asset limits depend on negotiated scope (continuous pentest tier upsells)
Relies on PoC evidence to reduce false positives, but no explicit guarantee or SLA

Pentest priced separately (PTaaS) or as an add-on service

Available, but usually part of custom manual scope—extra effort & cost
Offered only as a dedicated Cloud Pen Test engagement
Primarily manual API pentest; automated scans require importing definitions—no passive discovery
Integrations exist but are tied to PTaaS portal and license limits per workspace
“Unlimited support” marketed, but priority/SLAs vary by purchased service bundle
Unlimited retests while PTaaS subscription active; stops if you don’t renew
No public pricing; “Get-a-Quote” required for every service
No self-serve trial—must book sales demo
ROI Advantage
Transparent, predictable spend—easier budget approval & no “custom-quote” delays
More coverage day one, no pay-per-scan bottlenecks
Fewer wasted developer hours chasing noise
No surprise add-ons—total cost of ownership stays low
Deeper, real-world flaw coverage without extra SOWs
Saves thousands on separate cloud audits
Better protection for rapidly changing micro-service estates
No upgrade tax for essential workflow tooling
Premier-level help without premium-tier pricing
Encourages faster remediation without annual-renewal pressure
Full cost visibility up front
Try before you buy reduces purchase risk

ROI comparison: Astra pricing  vs Intruder pricing

Astra Security stands out as the best Intruder alternative, offering a full range of security solutions that go beyond automated scanning.

Features
Pricing model
Vulnerability scans
False-positive reduction
Pentesting
Business-logic testing
Cloud Security Review
API security
Integrations & DevSecOps
Enterprise support
Retests / re-scans
Pricing Transparency
Trial access

Try Astra

Trusted by 1000+ security-conscious teams

Offensive DAST vulnerability scanner that scans behind login for 15,000+ test cases like OWASP Top 10, ports, CVEs & more

LIMITED OFFER

Try DAST Scanner for a full week — just $7

Get platform access · No credit card commitment · Cancel anytime

Start $7 Trial

BEST FOR SMALL TEAMS
Scanner Lite
Schedule monthly vulnerability scans

$69/m

Astra
1 Target

Here's how the target is defined

Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, IP, website, API etc.

‍

If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

‍

Astra
Supported for
15,000+ test cases
3 vulnerability scans a month
Authenticated scanning
1 Integration (Slack, Jira, CI/CD etc.)
Vulnerability management console
Auto re-scan after fixes
AI fix assistance
Email support
⭐ Popular
BEST FOR SMALL TEAMS
Scanner
Unlimited security scans at dev speed

$199/m

1 Target

Here's how the target is defined

Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, IP, website, API etc.

‍

If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

Supported for
All Scanner Lite features, plus
Unlimited vulnerability scans
4 vetted scans (annual billing)
Unlimited integrations
BEST FOR SMALL TEAMS
Scanner Agency
Unlimited scans on a rotating pool

$499/m

5 Target Pool

Target

You get 5 target slots, with the ability to change targets in those slots with a 30-day cooling period. Example: Scan 5 targets, after 30 days scan 5 new targets.

Target Explained: Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, website, API etc. If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

‍

Get Started
Supported for
All Scanner features, plus
5-target pool, swap every 30 days
4 expert vetted scans (any billing)
Customer success manager
LIMITED OFFER

Try DAST Scanner for a full week — just $7

Get platform access · No credit card commitment · Cancel anytime

Start $7 Trial

BEST FOR SMALL TEAMS
Scanner Lite
Schedule monthly vulnerability scans

$699/yr

Astra
1 Target

Here's how the target is defined

Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, IP, website, API etc.

‍

If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

‍

Astra
Supported for
15,000+ test cases
3 vulnerability scans a month
Authenticated scanning
1 Integration (Slack, Jira, CI/CD etc.)
Vulnerability management console
Auto re-scan after fixes
AI fix assistance
Email support
⭐ Popular
BEST FOR SMALL TEAMS
Scanner
Unlimited security scans at dev speed

$1999/yr

1 Target

Here's how the target is defined

Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, IP, website, API etc.

‍

If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

Supported for
All Scanner Lite features, plus
Unlimited vulnerability scans
4 vetted scans (annual billing)
Unlimited integrations
BEST FOR SMALL TEAMS
Scanner Agency
Unlimited scans on a rotating pool

$4999/yr

5 Target Pool

Target

You get 5 target slots, with the ability to change targets in those slots with a 30-day cooling period. Example: Scan 5 targets, after 30 days scan 5 new targets.

Target Explained: Simply put, a domain with all its site tree URLs is a target. Target can be the URL of a web application, website, API etc. If your website makes API calls to different domains (eg: api.example.com), you can add them as an extra host during setup without having to purchase another target for it, and all calls to api.examples.com from example.com will be scanned.

‍

Get Started
Supported for
All Scanner features, plus
5-target pool, swap every 30 days
4 expert vetted scans (any billing)
Customer success manager
For Partners

Think your customers would love Astra too? Let's join forces.

Perfect for
Compliance platforms
MSSPs
Insurance providers
Auditors

Hacker-style pentest by Autonomous AI & certified experts at dev speed, built to meet & exceed
SOC2, ISO, & HIPAA requirement

BEST FOR SMALL TEAMS
Pentest Auto
1 Target

One web or SaaS app counts as one target, including all APIs consumed.
Mobile is per platform, so an Android app and an iOS app are two targets
Networks, cloud, IPs and standalone APIs are 1 target each

Hacker style autonomous pentest at machine speed

$2999/yr

$199/mo

Astra
1 Target
Astra
Astra
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Click the 🛈 icon to know more.
Pentest for SOC2, ISO 27001, HIPAA etc.
Supported for
Real-world attack simulation
Vulnerability management console
Role based graybox pentest
AI auto-fixes
Trust Center
1 human re-scan
Email support
1 Integration
⭐ Popular
BEST FOR SMALL TEAMS
Pentest Expert
1 Target

One web or SaaS app counts as one target, including all APIs consumed.
Mobile is per platform, so an Android app and an iOS app are two targets
Networks, cloud, IPs and standalone APIs are 1 target each

Offensive pentests by certified pentesters & autonomous agents

$5999/yr

Pentest for SOC2, ISO 27001, HIPAA etc.
Supported for
All Pentest Auto features, plus
Manual pentest by certified experts
CREST, PCI-ASV, CERT-IN reports
Unlimited web DAST scans
AI component pentesting
2 human re-scans
Customer success manager
Unlimited integrations
BEST FOR SMALL TEAMS
Enterprise
Autonomous testing & certified pentesters, tailored to your infra

$9999/yr onwards

Run a world class continuous pentest program.
Supported for
All Pentest Expert features, plus
Security consulting
On-premise deployment
Private cloud instance
Custom SLA & payment terms
Voice on roadmap
Custom workspace management
ScannER

$999/yr

$75/mo effectively
Astra
1 Target
Astra
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Know More
Get Started
tick

Weekly vulnerability scans with 3000+ tests (OWASP, SANS etc.)

tick

Essential features like pentest dashboard, PDF reports and scan behind login

For Partners

Think your customers would love Astra too? Let's join forces.

Perfect for
Compliance platforms
MSSPs
Insurance providers
Auditors

Continuously discover & scan every API in your infrastructure for broken access control, authorization flaws, OWASP Top 10 & more

BEST FOR SMALL TEAMS
API DAST Scanner
Scheduled DAST scans on your API spec file
‍

$199/m

$199/mo

1 Target
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Click the 🛈 icon to know more.
15,000+ authenticated test cases
20 scans a month
CI/CD, JIRA & Slack
Auto re-scan after fixes
Full & management PDF reports
Email support
Extra scans at $10
⭐ Popular
BEST FOR SMALL TEAMS
API Security Pro
Continuous API discovery and scans               

$499/m

All API DAST Scanner features, plus
60 scans a month
Live API traffic capture
Continuous observability & inventory
Adds CSV & JSON reports
Orphan, shadow, zombie APIs
BEST FOR SMALL TEAMS
API Enterprise
Discovery and scanning at enterprise scale
‍

Custom

All API Security Pro features, plus
1000+ scans a year
15M+ API requests observed
Tailored test cases
Dedicated account manager
Volume-based scan pricing
BEST FOR SMALL TEAMS
API DAST Scanner
Scheduled DAST scans on your API spec file
‍

$1999/yr

$199/mo

1 Target
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Click the 🛈 icon to know more.
15,000+ authenticated test cases
20 scans a month
CI/CD, JIRA & Slack
Auto re-scan after fixes
Full & management PDF reports
Email support
Extra scans at $10
⭐ Popular
BEST FOR SMALL TEAMS
API Security Pro
Continuous API discovery and scans               

$4999/yr

All API DAST Scanner features, plus
60 scans a month
Live API traffic capture
Continuous observability & inventory
Adds CSV & JSON reports
Orphan, shadow, zombie APIs
BEST FOR SMALL TEAMS
API Enterprise
Discovery and scanning at enterprise scale
‍

Custom

All API Security Pro features, plus
1000+ scans a year
15M+ API requests observed
Tailored test cases
Dedicated account manager
Volume-based scan pricing
For Partners

Think your customers would love Astra too? Let's join forces.

Perfect for
Compliance platforms
MSSPs
Insurance providers
Auditors

Astra continuously scans AWS, Azure, and GCP for misconfigs, IAM risks, and vulnerabilities, validating every finding before it reaches you

LIMITED OFFER

Try Cloud Starter for a full week — just $7

Full platform access · AWS, Azure & GCP · No credit card commitment · Cancel anytime

Start $7 Trial

BEST FOR SMALL TEAMS
Cloud Starter
Scan for cloud security misconfigurations across your cloud account

$99/m

$199/mo

1 Target
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Click the 🛈 icon to know more.
Supported for
Security misconfigs & IAM checks
1 cloud account
Up to 250 resources
Unlimited automated scans
Auto re-scan after fixes
PDF reports
Validated findings
Unlimited Integrations
Email support
⭐ Popular
ENTERPRISE-READY (CUSTOM)
Cloud Growth
Scheduled multi-account scans with control mapping

$199/m

Supported for
All Cloud Starter features, plus
3 cloud accounts
Up to 1000 resources
Scheduled scans
Control mapping
JSON & management reports
BEST FOR LARGE TEAMS
Cloud Enterprise
Multi-cloud and hybrid scanning at enterprise scale

Custom

Supported for
All Cloud Growth features, plus
Multi-cloud & hybrid
Unlimited resources
Continuous scan scheduling
Custom dashboards
Customer Success Manager
LIMITED OFFER

Try Cloud Starter for a full week — just $7

Full platform access · AWS, Azure & GCP · No credit card commitment · Cancel anytime

Start $7 Trial

BEST FOR SMALL TEAMS
Cloud Starter
Automated configuration scans on your cloud account

$999/yr

$199/mo

1 Target
A target is a URL that will be tested by our vulnerability scanner. It can be the URL of a web application, website, API etc.

If your website makes API calls to different domains, you can add them as an extra host without having to purchase another domain.

Let's say you have a customer dashboard at https://app.example.com/ and an admin dashboard at https://admin.example.com/ with different login pages, then you will need 2 targets.

Click the 🛈 icon to know more.
Supported for
Security misconfigs & IAM checks
1 cloud account
Unlimited automated scans
Up to 250 resources
Auto re-scan after fixes
PDF reports
Validated findings
Unlimited Integrations
Email support
⭐ Popular
Cloud Growth
ENTERPRISE-READY (CUSTOM)
Scheduled multi-account scans with control mapping

$1999/yr

Supported for
All Cloud Starter features, plus
3 cloud accounts
Up to 1000 resources
Scheduled scans
Control mapping
JSON & management reports
BEST FOR LARGE TEAMS
Cloud Enterprise
Multi-cloud and hybrid scanning at enterprise scale

Custom

Supported for
All Cloud Growth features, plus
Multi-cloud & hybrid
Unlimited resources
Continuous scan scheduling
Custom dashboards
Custom integrations & API
Customer Success Manager
For Partners

Think your customers would love Astra too? Let's join forces.

Perfect for
Compliance platforms
MSSPs
Insurance providers
Auditors

Here’s what Breachlock's users have to say:
Elise Rowan

Lots of duplicates and false-positives to filter out after receiving a report.
Audrey Flint

Their portal is not the most up-to-date compared to some of the others that we reviewed.
Julian Hartwell

They’re slow to respond, only available via email and clearly English is a second language for them making it challenging to understand what they’re asking us.

Colin Mercer

The fact that the Automated Scans and Manual Scans were in different interfaces was less than ideal.

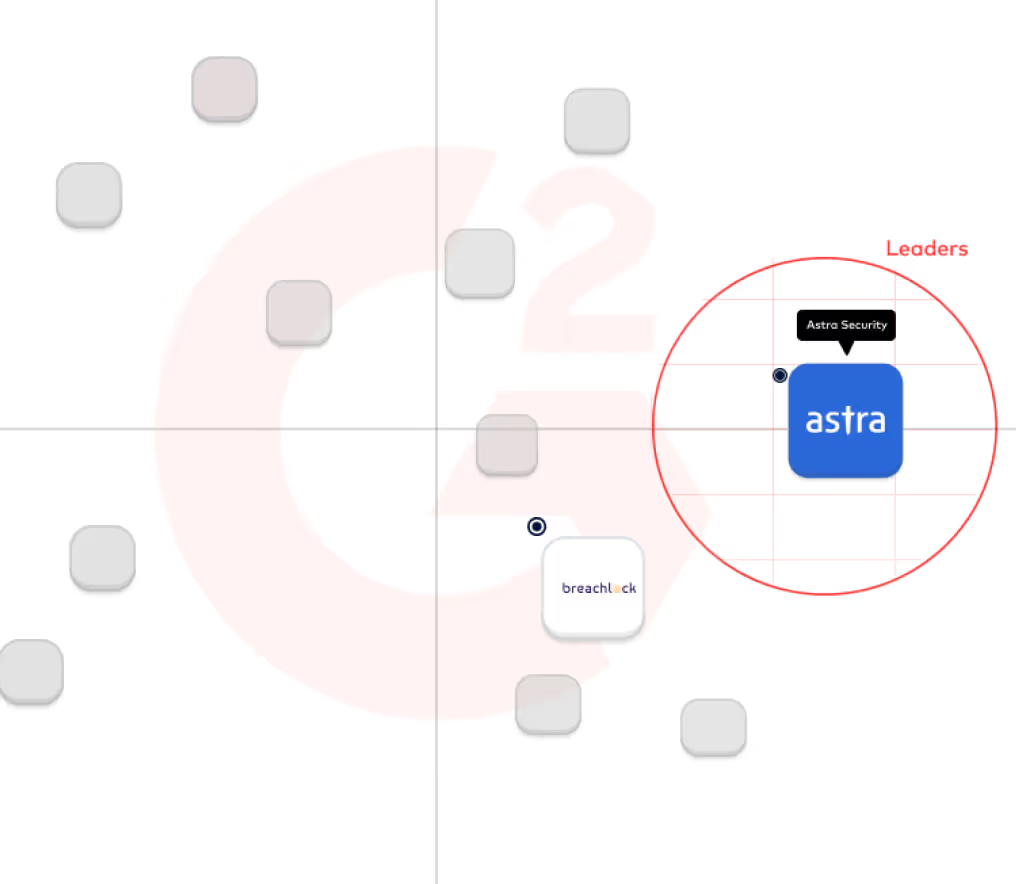
Astra Security is a G2 Momentum Leader
(Spring 2025)

Trusted by startups
to fortune 100companies

G2 Leader WinterG2 Most Implementable WInterG2 Momentum Leader WinterG2 Best Results Mid Market Winter

‍Pentesting should feel like part of your
workflow
, not a black box

BreachLock
Dashboard offers limited collaboration and context
Custom scan support is unclear and lacks flexibility
On-demand security experts are available only with an add-on subscription

No AI assistance for remediation, relies on support tickets
Astra Security
Manual pentests are built into the platform with expert-led validation
Continuous access to certified security researchers (OSCP, CEH, CREST)

Developer-first dashboard with guided remediation, fix prioritization

Built-in AI chatbot for CVSS scoring, patching logic, and exploit insights


‍ Astra reinforces your security. BreachLock just reports it
BreachLock
Certificates shared only in private PDF reports
No Trust Center to show live security status

Compliance is mapped post-facto in static reports

No AI assistance for remediation, relies on support tickets
Astra Security
Publicly verifiable Pentest Certificate you can embed anywhere
Custom reports for CXOs, engineers, and auditors, expediting fixes and demonstrating security
Real-time Trust Center: share coverage, findings, and status

Live compliance dashboard mapped to SOC 2, ISO 27001, PCI-DSS, HIPAA, GDPR


APIs evolve fast. Your security needs to be faster
BreachLock
API discovery depends on static definitions (OpenAPI, Swagger)
No capability to detect undocumented or dormant APIs
REST-focused, unclear coverage for GraphQL, mobile APIs
No mention of delta scans for changed endpoints
Astra Security
API discovery via real-time traffic (Postman, AWS/GCP mirroring, API gateways)

Flags shadow APIs, zombie APIs or exposed PII in <30 minutes


Supports REST, GraphQL, SOAP, HTTP, and mobile APIs
Offers delta scans for updated/changed endpoints 

Built for DevSecOps. Not just “DevOps adjacent”
BreachLock
No documented CI/CD integrations
No scan triggers from pipelines
Basic ticketing (Jira, Trello)

Lacks compliance tool integrations


Astra Security
Native integrations with GitHub, GitLab, Jenkins, Azure DevOps, and more
Automatically trigger tests from CI/CD after every deployment

Deep Jira integration for assigning and tracking fixes

Vanta integration for SOC 2, ISO reporting automation


Transparent pricing. Try before you buy

BreachLock
Quote-based pricing behind sales forms

No free trial publicly available

Manual pentests and integrations may cost extra
Astra Security
Public pricing starts at $1,999/year


7-day trial available with all core features
Manual PT, unlimited DAST, CI/CD integration included by default

Trust isn't claimed, it's earned

Astra meets global standards with accreditations from

Loved by 1000+ CTOs & CISOs worldwide

We are impressed by Astra's commitment to continuous rather than sporadic testing.

Wayne
Wayne Garb
CEO, OOONA

Astra not only uncovers vulnerabilities proactively but has helped us move from DevOps to DevSecOps

Vinish Vijayan
IT Manager, Muthooth Finance

Their website was user-friendly & their continuous vulnerability scans were a pivotal factor in our choice to partner with them.

Larry Crawley
CTO, Strategic Audit Solutions, Inc.

The combination of pentesting for SOC 2 & automated scanning that integrates into our CI pipelines is a game-changer.

Jack Collins
Head of Product Engineering, Naro

I like the autonomy of running and re-running tests after fixes. Astra ensures we never deploy vulnerabilities to production.

Arthur De Moulins
Web Architect, Vkard

We are impressed with Astra's dashboard and its amazing ‘automated and scheduled‘ scanning capabilities. Integrating these scans into our CI/CD pipeline was a breeze and saved us a lot of time.

Ankur Rawal
CTO, Zenduty

Overall, Astra made the penetration testing process much more manageable and helped us complete our audit requirements on time.
Grace Yu
Business Development Manager, ShipSaving

We are impressed by Astra's commitment to continuous rather than sporadic testing.

Wayne
Wayne Garb
CEO, OOONA

Astra not only uncovers vulnerabilities proactively but has helped us move from DevOps to DevSecOps

Vinish Vijayan
IT Manager, Muthooth Finance

Their website was user-friendly & their continuous vulnerability scans were a pivotal factor in our choice to partner with them.

Larry Crawley
CTO, Strategic Audit Solutions, Inc.

The combination of pentesting for SOC 2 & automated scanning that integrates into our CI pipelines is a game-changer.

Jack Collins
Head of Product Engineering, Naro

I like the autonomy of running and re-running tests after fixes. Astra ensures we never deploy vulnerabilities to production.

Arthur De Moulins
Web Architect, Vkard

We are impressed with Astra's dashboard and its amazing ‘automated and scheduled‘ scanning capabilities. Integrating these scans into our CI/CD pipeline was a breeze and saved us a lot of time.

Ankur Rawal
CTO, Zenduty

Overall, Astra made the penetration testing process much more manageable and helped us complete our audit requirements on time.

Grace Yu
Business Development Manager, ShipSaving

Ready to shift left and ship right?

Let's chat about making your releases faster and more secure
Click here to update your cookies settings