


Trusted by 1000+ Engineering Teams

Astra is a CREST-approved member, CERT-In empanelled, PCI ASV-
approved scanning vendor, and ISO 27001-certified


Why integrations matter for continuous security testing
90%
faster deployments
35%
faster vulnerability detection
50%
reduce in defect rates
10x
cheaper security remediation
80%
decrease in deployment incidents
The ecosystem that makes
continuous security effortless
CI/CD & Developer Workflows
Compliance & Governance
Communication
Project & Issue Tracking
API Traffic Connectors (Astra API Security Platform)
Custom CI/CD via API
Prevent leaks before deployment with Secret Scanner
Automatically catch exposed API keys, tokens, and credentials before they reach production.
Scans repositories and environments for hardcoded secrets
Supports custom detection rules for internal tokens or patterns unique to your stack
Runs silently alongside existing scans with no impact on workflows
Adds an extra layer of protection on top of Astra’s built-in security
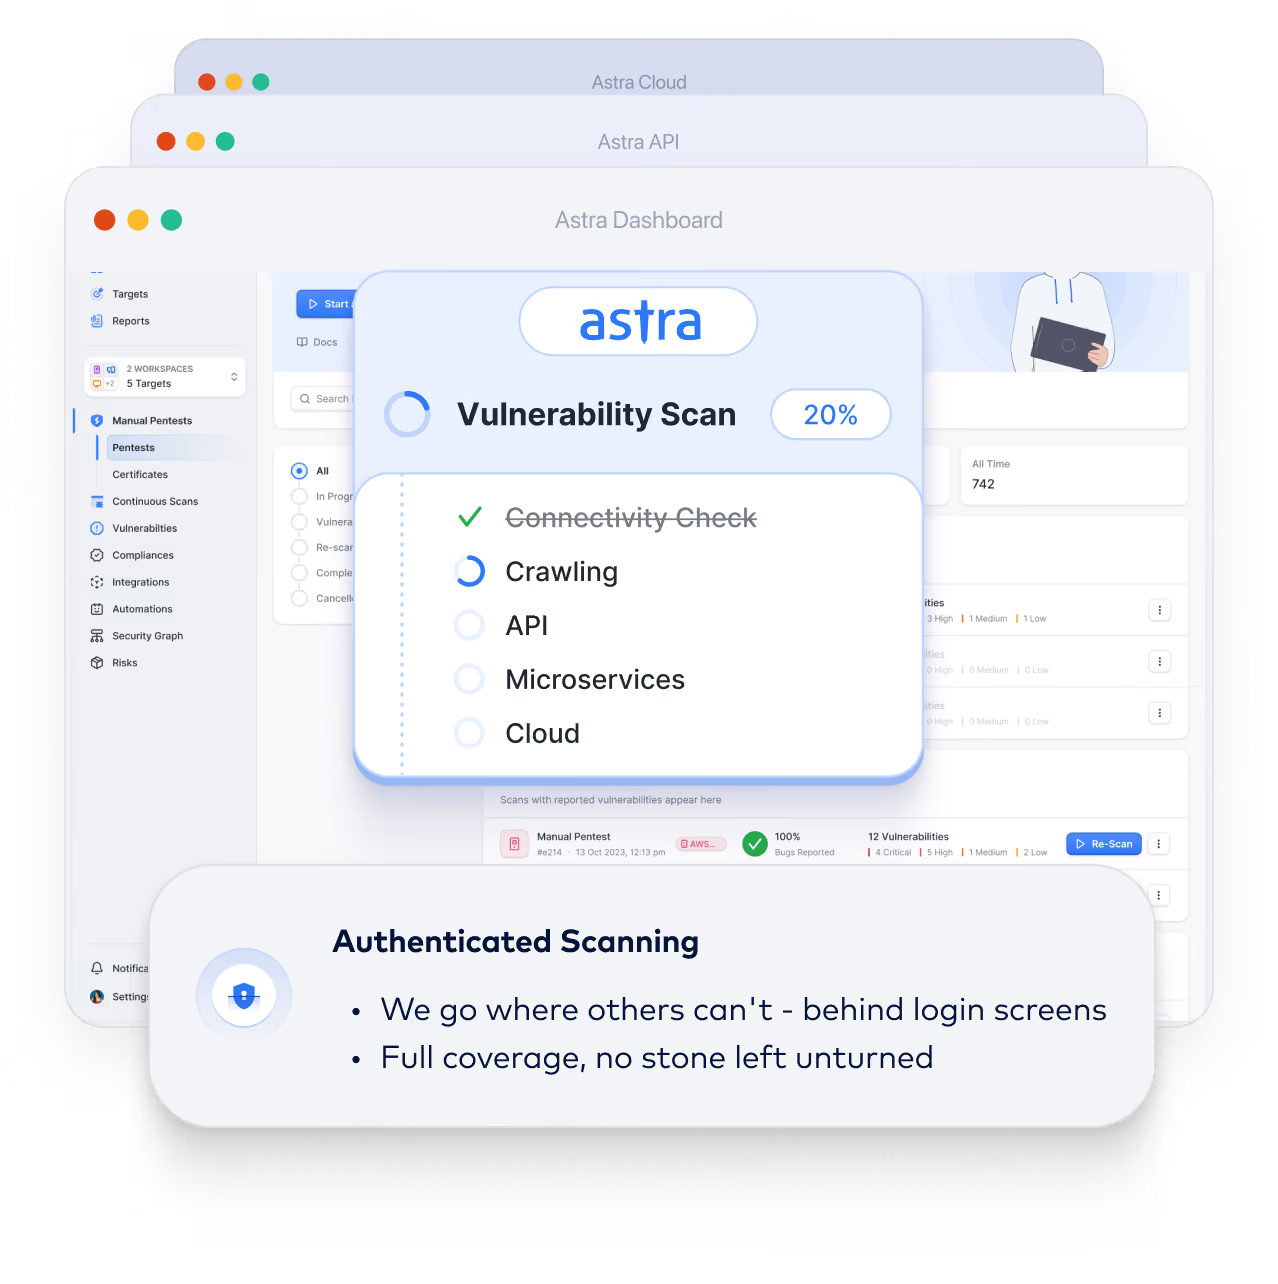
Workflows that fit into your team
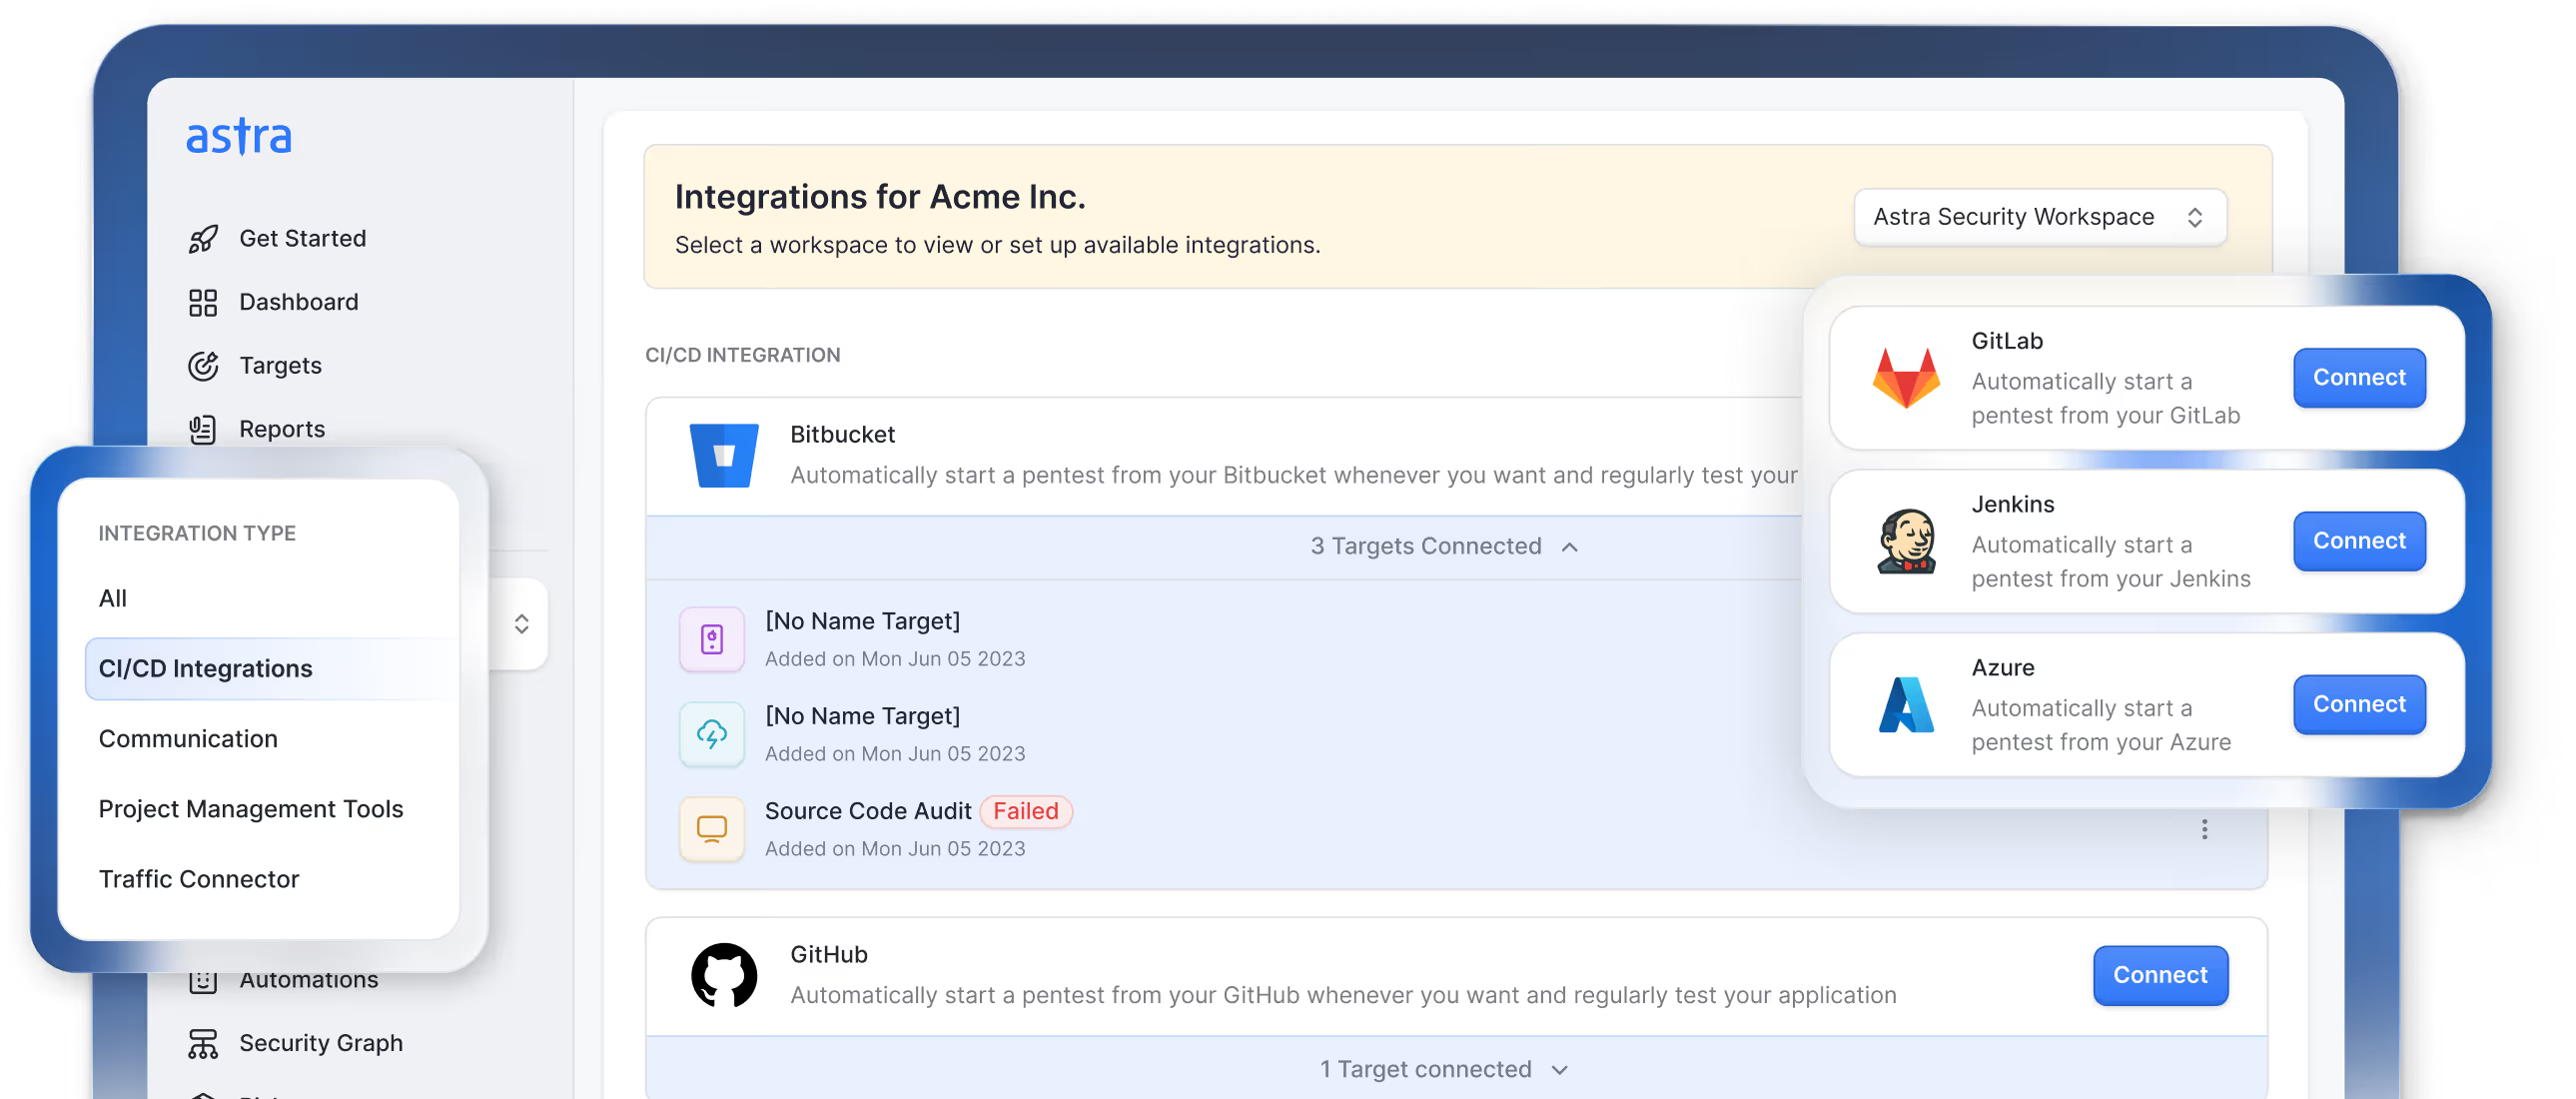
Configure Astra in GitHub, GitLab, Jenkins, Bitbucket, Azure, or CircleCFix vulnerabilities during development
Fix vulnerabilities during development
Configure Astra in GitHub, GitLab, Jenkins, Bitbucket, Azure, or CircleCFix vulnerabilities during development
Fix vulnerabilities during development
Configure Astra in GitHub, GitLab, Jenkins, Bitbucket, Azure, or CircleCFix vulnerabilities during development
Fix vulnerabilities during development
Jira integration allows vulnerabilities found in Astra to be directly pushed as Jira issues
You’ll not miss any vulnerability reported
Each vulnerability links back to Astra details for context
Faster remediation
Jira issues can be created manually from the vulnerability page inside Astra dashboard
Visibility for security teams and developers kept in loop
Vanta integration syncs Astra pentest reports into compliance dashboards
Continuously monitor compliance risks
Only available when a pentest is in Re-Scan or Certificate Awarded stage which ensures audit-ready reports
Audit prep reduced from weeks to minutes
Reports appear inside the Vanta dashboard in “Documents” tab
Directly supports GDPR, SOC 2, PCI DSS readiness
Get notified when new security issues are found
Immediate visibility of security events
Know when a scan is completed
No need to log into the dashboard everytime
Stay updated on any important changes to your account or settings
Alerts can be configured by target or channel
Loved by 1000+ companies across
70+ countries
"Approachable pentesting service with a centralised collaboration space"
"Comprehensive review"
"Very powerful tool with interactive
insights"
"Excellent support and guidance through a super comprehensive audit process"
"Our go to provider for our pentest requirements"