Mobile apps ship fast today, often at the cost of security. Mobile app pentesting tools need to test beyond the binary. They help uncover risks across local storage, runtime behavior, APIs, network traffic, third-party SDKs, authentication, and business logic.
Astra’s State of Continuous Pentesting Report 2026 analyzed 6.8 million findings and found that 80% of tracked AWS credential exposure surfaced during mobile tests, not cloud scans.
The real challenge? Picking tools that do more than scan surfaces. This list covers the most effective ones.
At a Glance Verdict
- Astra Security is the best overall pick for teams that are looking for continuous testing, certified manual pentesting, remediation support, and compliance-ready proof in one platform.
- NowSecure is the strongest mobile-first runner-up for automated testing across large iOS and Android portfolios.
- MobSF is the best open-source option for security teams comfortable running and validating an open-source testing stack.
12 Best Mobile App Penetration Testing Tools
- Astra Security
- Burp Suite Professional
- Checkmarx
- Ostor Labs
- ZAP (Zed Attack Proxy)
- Mobile Security Framework (MobSF)
- Frida
- Data Theorem
- Drozer
- NowSecure
- Apktool
- Appknox
| Tool | Best for | Testing coverage | G2 rating | |
|---|---|---|---|---|
| Astra Security | Managed mobile pentesting with continuous validation and compliance-ready reporting | Automated, autonomous, and expert-led manual testing | 4.6/5 from 211 reviews | |
| Burp Suite Professional | Hands-on testing of mobile APIs and intercepted app traffic | Proxy-based manual testing with automated web and API scanning | 4.8/5 from 129 reviews | |
| Checkmarx One | Source-first mobile security inside the SDLC | SAST, SCA, secrets, API, IaC, and broader AppSec analysis | 4.2/5 from 49 reviews | |
| Ostor Labs | Continuous mobile and API scanning with attack-surface context | Mobile, API, web, and infrastructure scanning | Not listed on G2 | |
| ZAP by Checkmarx | Free proxy testing for mobile web traffic and APIs | Intercepting proxy and DAST for web and API traffic | 4.7/5 from 14 reviews | |
| Mobile Security Framework (MobSF) | Free automated static and dynamic mobile analysis | Static, dynamic, malware, and privacy analysis | Not listed on G2 | |
| Frida | Runtime instrumentation, bypass testing, and live behavior analysis | Dynamic instrumentation and runtime analysis | Not listed on G2 | |
| Data Theorem Mobile Secure | Continuous testing of every mobile release | SAST, DAST, behavioral runtime analysis, and SDK review | 4.0/5 from 1 review | |
| Drozer | Android IPC and component security testing | Android security assessment framework | Not listed on G2 | |
| NowSecure | Mobile-first automated testing across large iOS and Android portfolios | SAST, DAST, API, behavioral, and expert testing | 4.6/5 from 27 reviews | |
| Apktool | Android reverse engineering and resource inspection | APK decoding, rebuilds, and resource analysis | Not listed on G2 | |
| Appknox | Regulated teams that need binary, dynamic, API, and compliance evidence | Binary SAST, real-device DAST, API, SBOM, and manual testing | 4.5/5 from 44 reviews |
The Best Mobile App Penetration Testing Tools
1. Astra Security
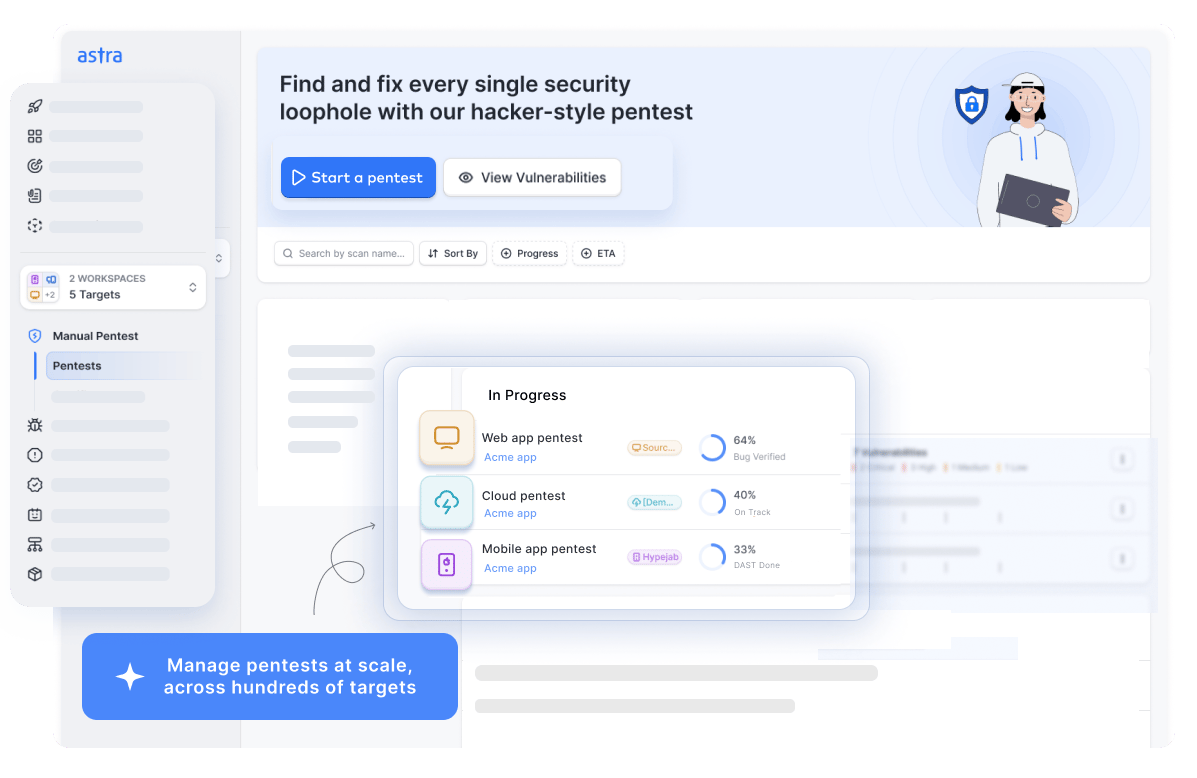
Astra Pentest empowers you to secure mobile apps early with a hybrid approach using test cases across OWASP Mobile Top 10, custom business logic tests, and SAST+DAST automation. This helps detect real-world vulnerabilities that generic tools and checklists typically overlook.
The platform makes collaboration seamless with AI-generated test flows, scan-behind-login capabilities, and integrations with Jira, Slack, GitHub, and more. You upload your APK/IPA file, our certified experts do the rest, from analysis to remediation guidance.
Astra makes compliance effortless with two free rescans, publicly verifiable certificates, and tailored reports for engineering and leadership. It offers not just pentesting but continuous assurance that your app is breach-ready and business-resilient.
Key Features:
- Scanner Capabilities: Automated scans, manual pentest, vetted scans.
- Accuracy: Zero false positives through AI-powered and expert validation.
- Compliance Support: GDPR, ISO 27001, HIPAA, SOC2, PCI ASV, CREST-In and PCI DSS.
- App Support: Both Android and iOS.
- Pricing: Trial starts at $7/week and is then $199/month.
Pros:
- Tests for reverse engineering resistance and code obfuscation.
- ombines platform speed with human validation and remediation support.
- Detects hardcoded secrets, tokens, and sensitive data.
- Validates session management and role-based access control.
- Supports CI/CD integration for continuous pentesting.
- Offers dedicated Slack/Teams channels for faster issue resolution.
Limitations:
- Trial available at $7. No free trial.
2. Burp Suite Professional
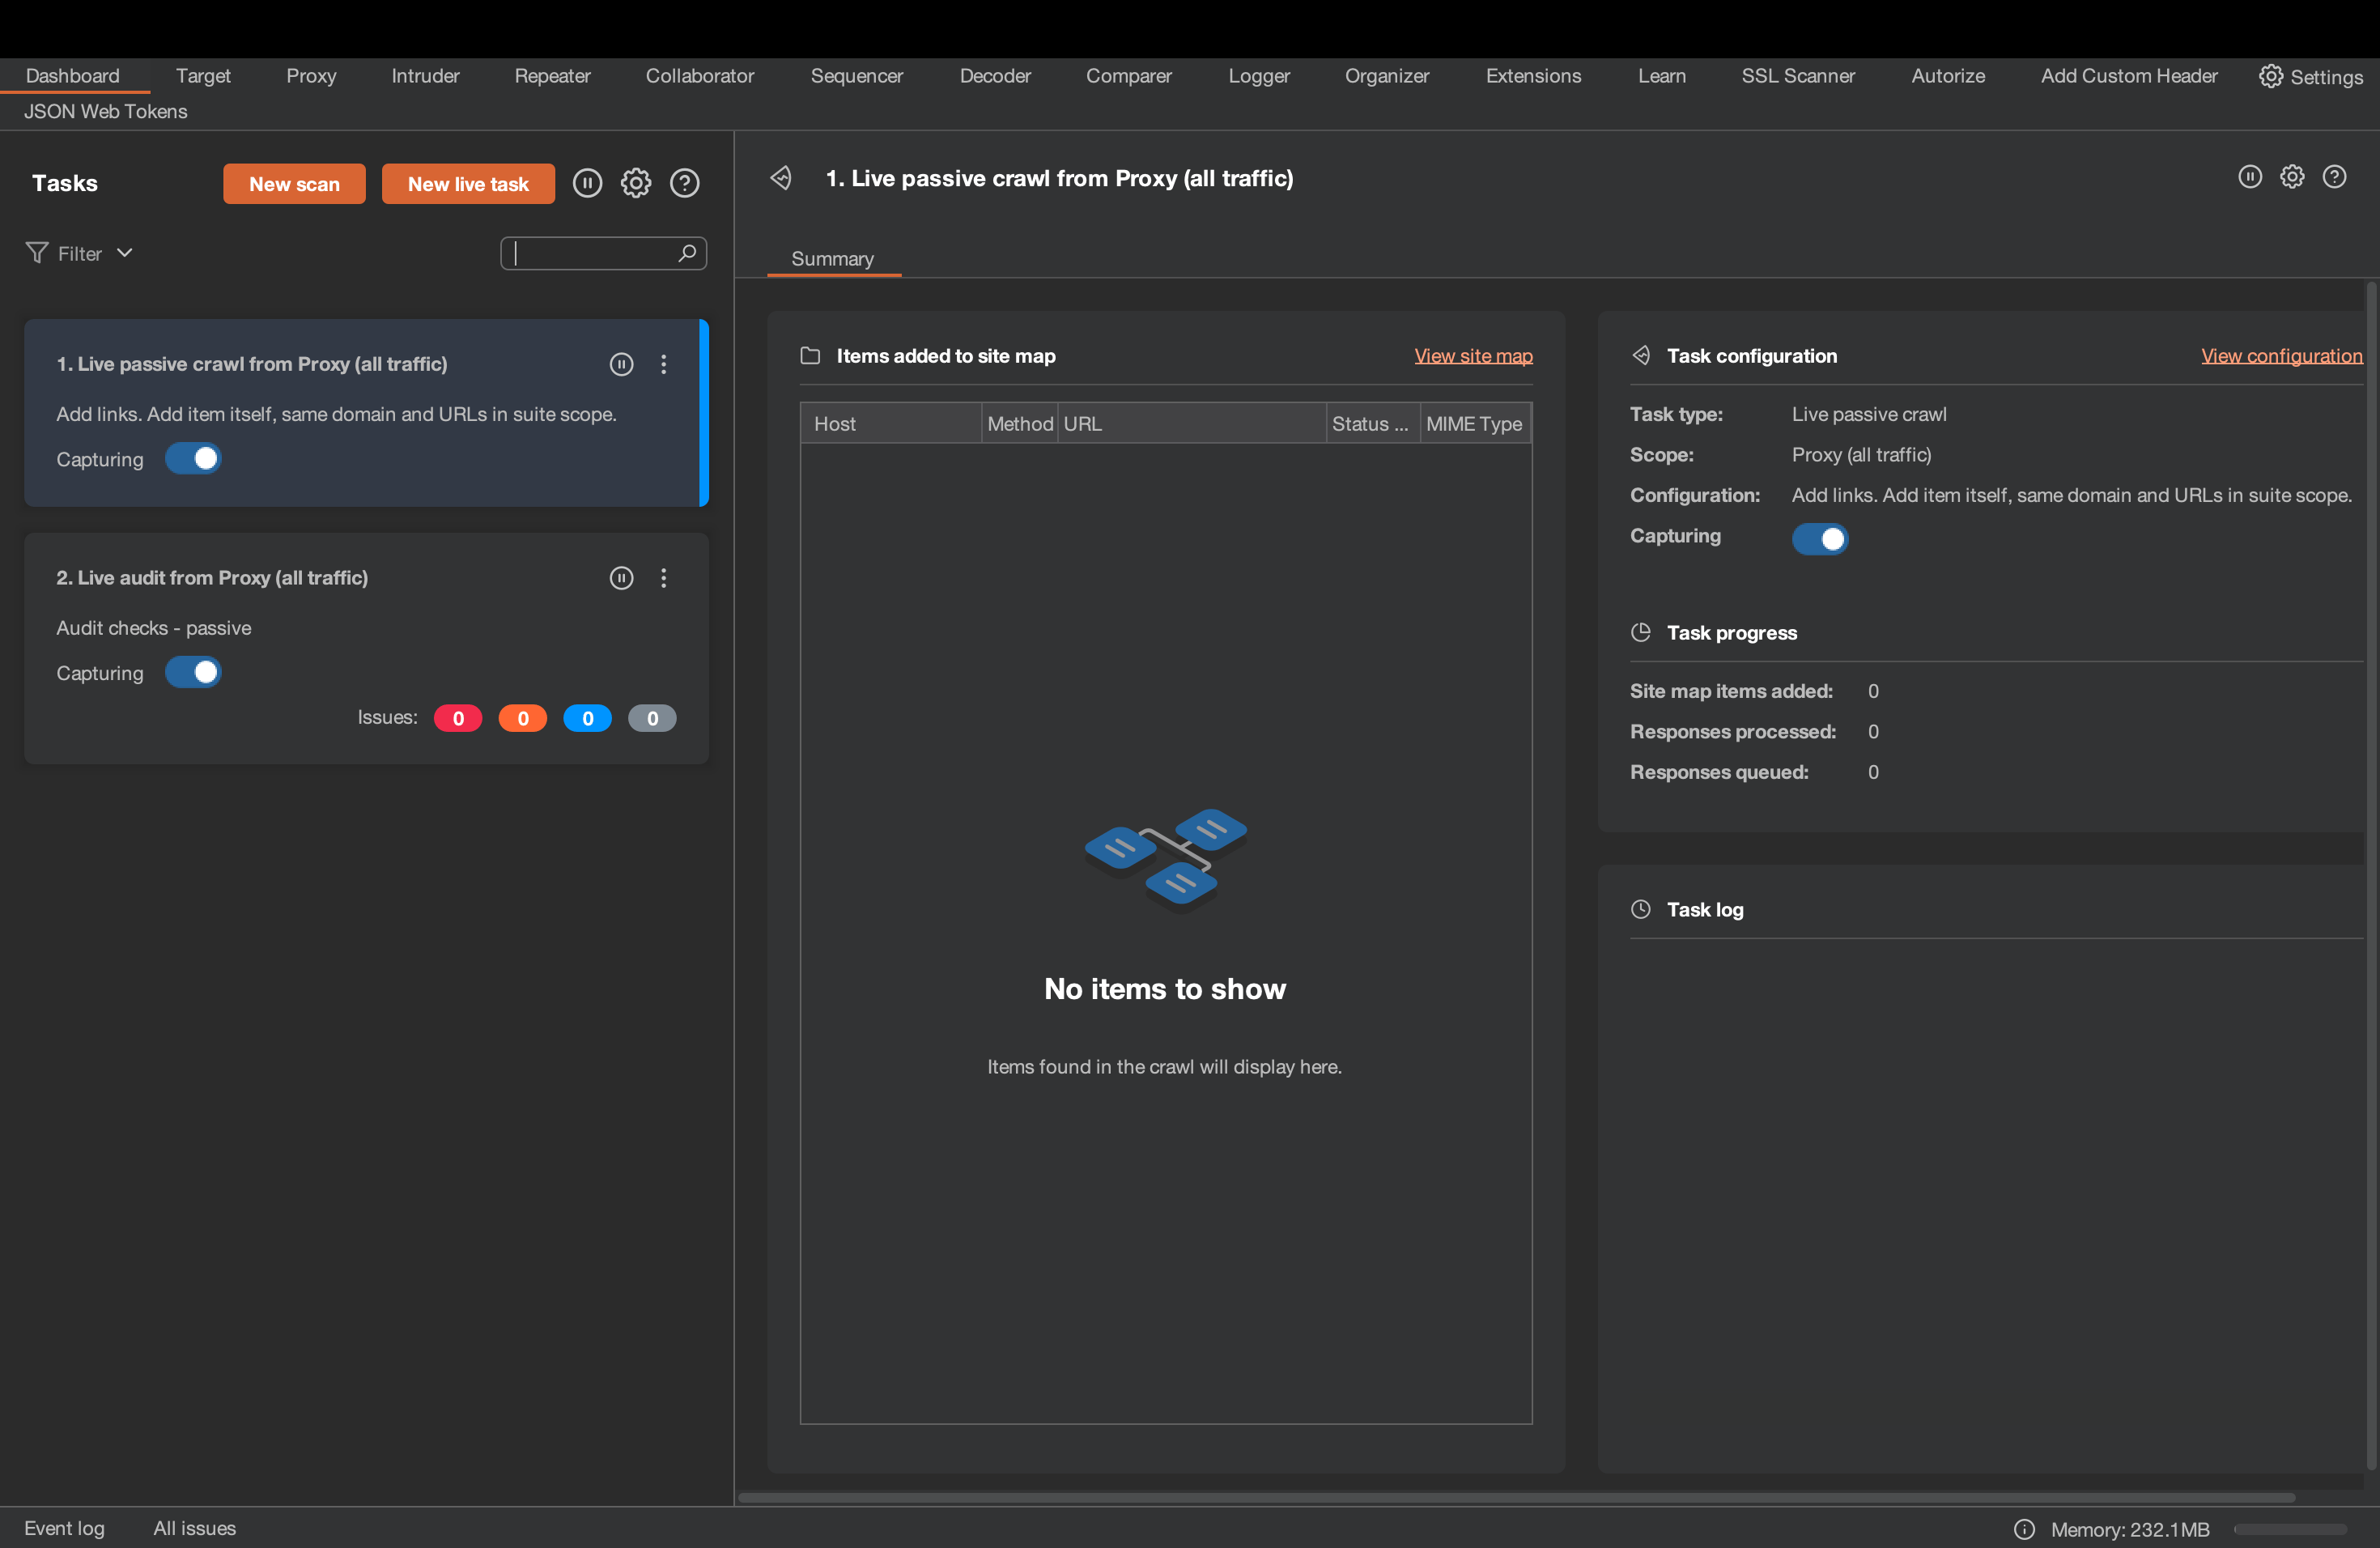
Burp Suite is a leading penetration testing tool for analyzing applications helping the security experts with manual as well as automated testing. It functions as a proxy server, giving testers the power to investigate and amend the data exchange between the browser and the chosen application.
Key Features:
- Scanner Capabilities: Automated and manual vulnerability testing.
- Accuracy: High, minimal false positives.
- Compliance Support: OWASP, PCI DSS, GDPR.
- App Support: Both Android and iOS.
- Pricing: Starts at $499/year.
Pros:
- Great for manual and automated penetration testing
- Strong community support
Limitations:
- Requires a learning curve
- Does not cover binary review, local storage, or runtime behavior by itself.
3. Checkmarx
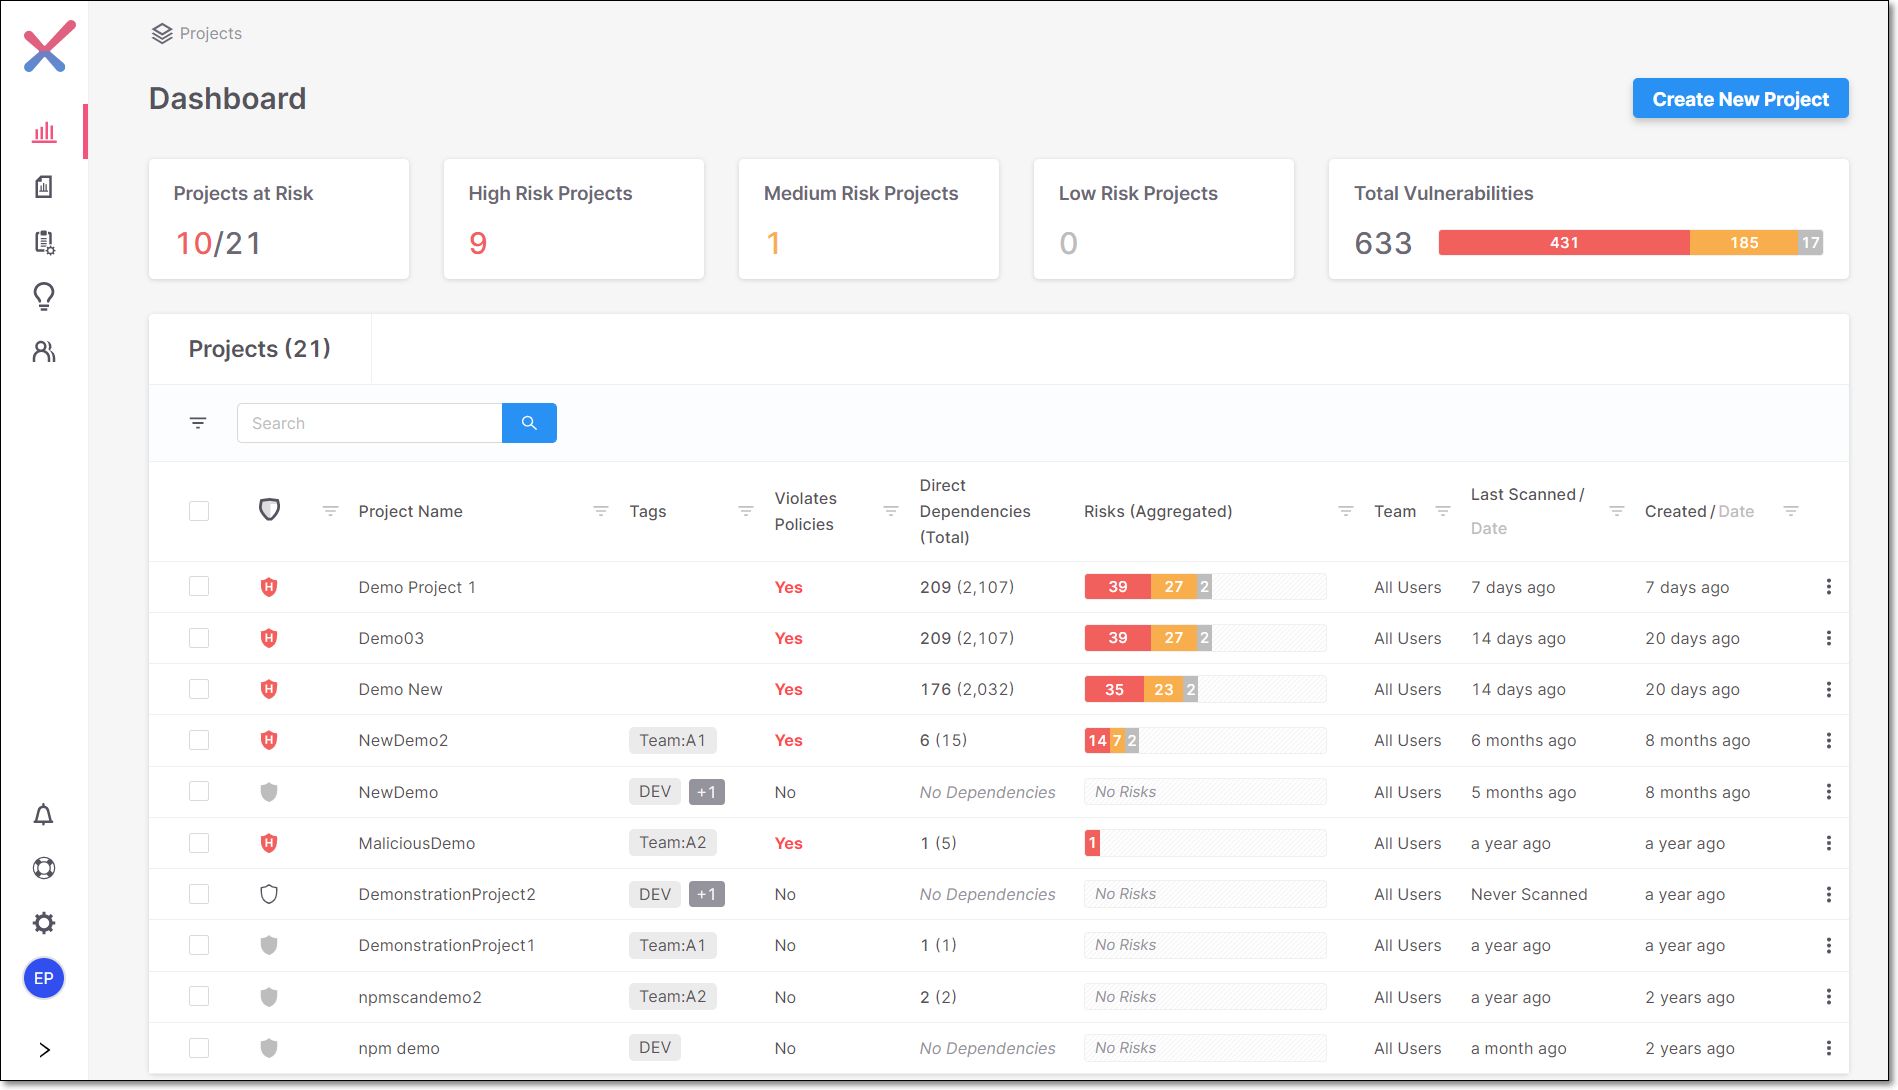
Checkmarx is one of the leading SAST mobile app pentesting tools that integrates with the CI/CD pipeline to identify issues in the codebase. Developers and security teams use it to detect and analyze vulnerabilities during the SDLC, helping to secure the application from the beginning.
Key Features:
- Scanner Capabilities: Scans source code for vulnerabilities, CI/CD integration.
- Accuracy: High, with detailed remediation guidance.
- Compliance Support: GDPR, ISO 27001, and OWASP Top 10.
- App Support: Both Android and iOS.
- Pricing: Custom pricing available.
Pros:
- Easy to integrate into CI/CD pipelines
- Provides detailed remediation guidelines
Limitations:
- Slower scan times for large projects
- Device-layer and business-logic testing still need other tools or expert review.
4. Ostor Labs
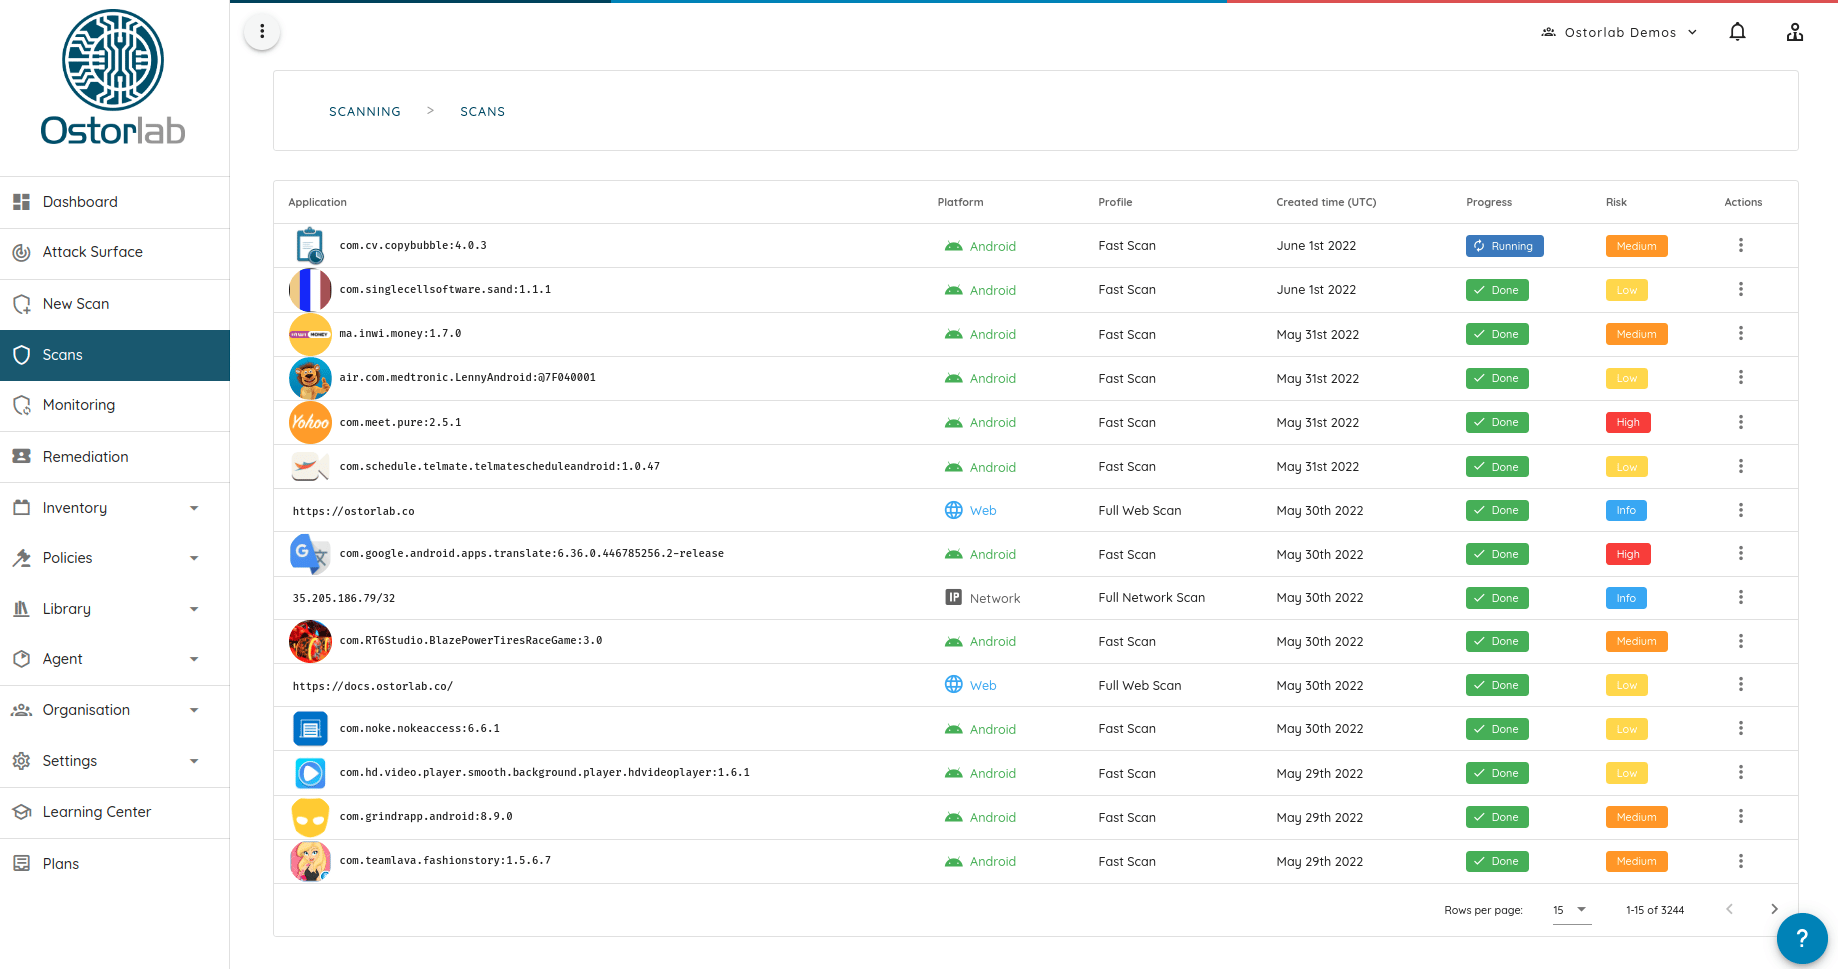
Ostor Labs is one of the most recommended tools by security analysts as it provides a strong automated mobile application testing platform that performs in-depth vulnerability scans on the applications.
Key Features:
- Scanner Capabilities: Automated static and dynamic scans.
- Accuracy: High, with minimal false positives.
- Compliance Support: PCI DSS, GDPR, and OWASP.
- App Support: Both Android and iOS.
- Pricing: Starts at $653/month.
Pros:
- Strong automation with minimal manual intervention
- Supports multiple compliance standards
Limitations:
- Limited customization for advanced testing scenarios
5. ZAP by Checkmarx (Zed Attack Proxy)
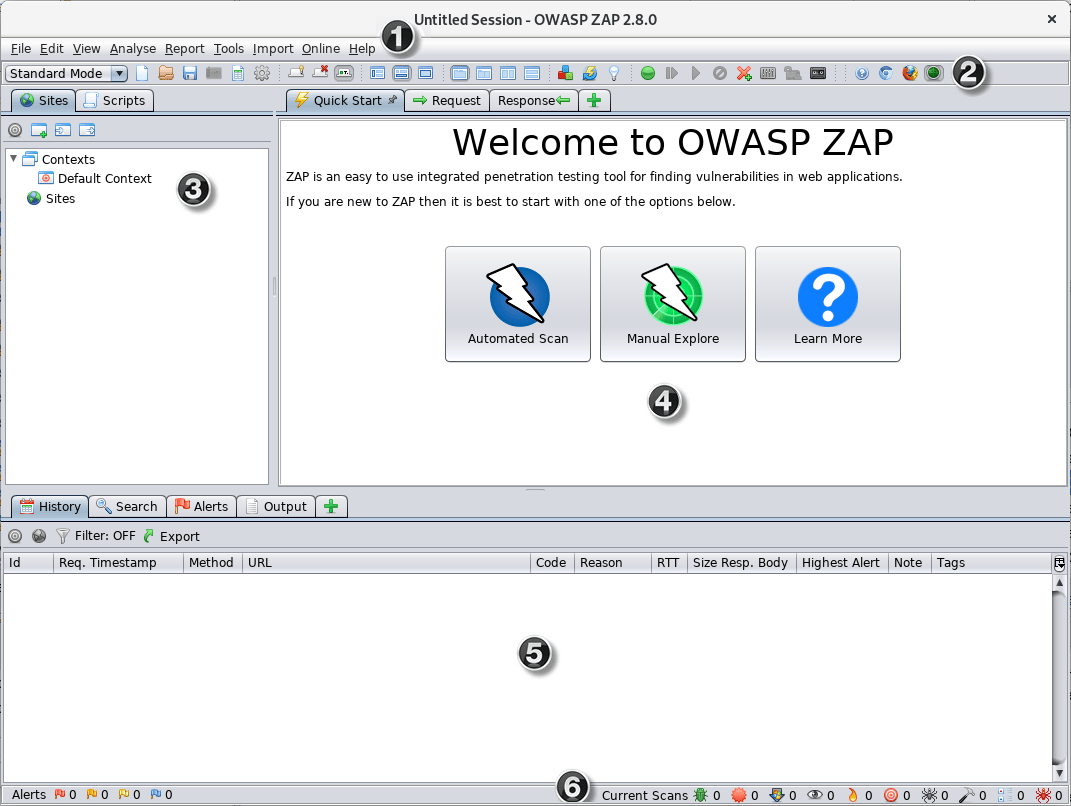
ZAP or Zed Attack Proxy is a free and open-source application testing tool for web applications and includes mobile applications. It is a DAST tool based on the OWASP Top 10 and performs a comprehensive analysis of mobile applications.
Key Features:
- Scanner Capabilities: Automated scans, proxy-based manual testing.
- Accuracy: Moderate, with some false positives.
- Compliance Support: OWASP Top 10.
- App Support: Android, iOS.
- Pricing: Open source
Pros:
- Streamlined user experience
- Advanced security testing capabilities
Limitations:
- Direct support options may be limited
6. Mobile Security Framework (MobSF)
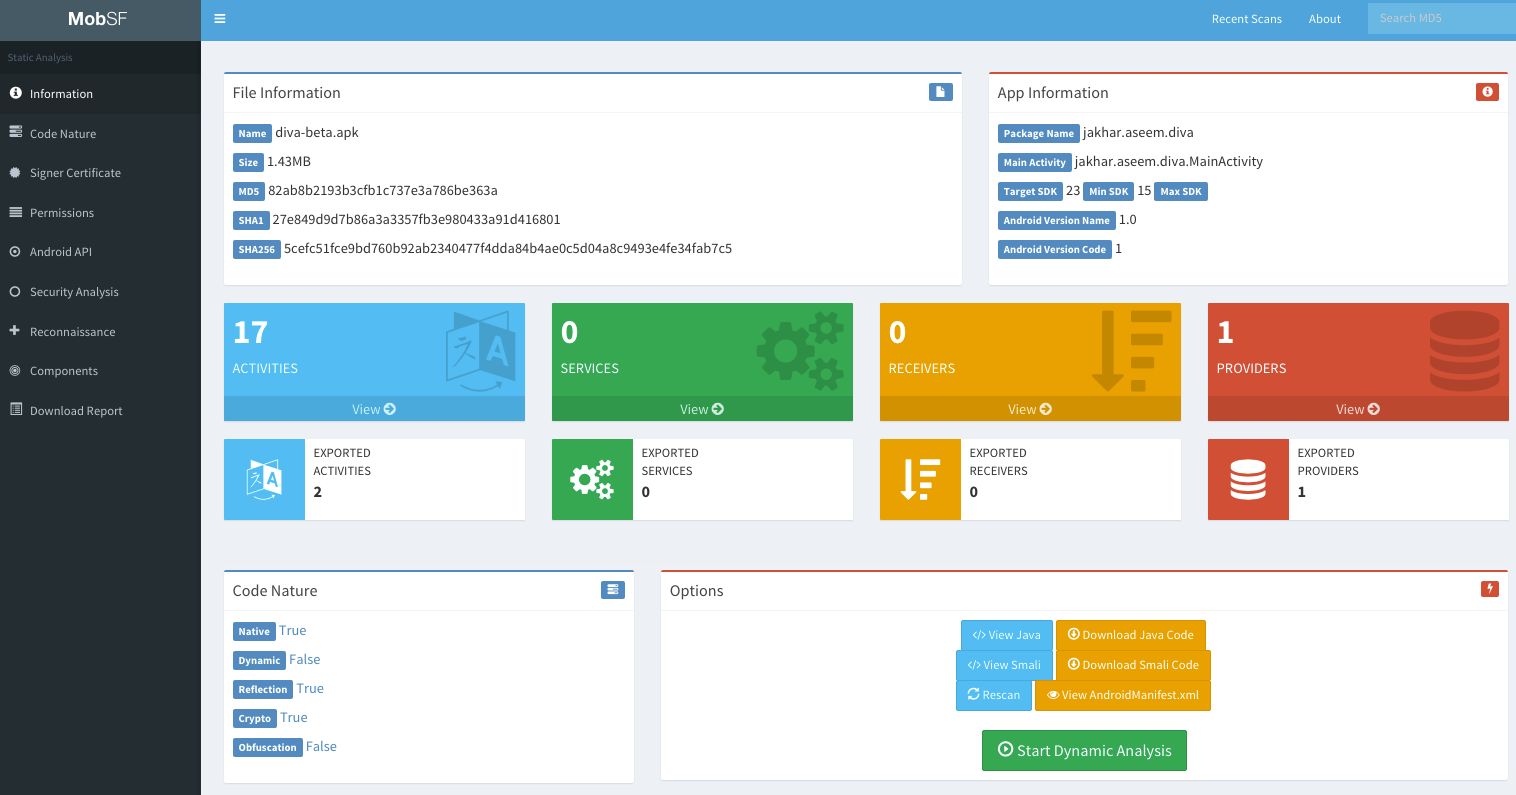
MobSF, or Mobile Security Framework, is an all-in-one tool for static and dynamic testing of mobile applications. It delves into the code to scout for possible security issues and vulnerabilities in libraries and examines insecure permissions and configurations.
Key Features:
- Scanner Capabilities: Comprehensive scans covering static, dynamic, and malware analysis.
- Accuracy: High for static analysis, moderate for dynamic.
- Compliance Support: PCI DSS, OWASP, MASVS and others.
- App Support: Both Android and iOS.
- Pricing: Open source (Free).
Pros:
- Provides support for both static and dynamic analysis.
- Automated API and permissions analysis.
Limitations:
- The interface could be more intuitive.
- Requires manual review since automated findings need validation.
7. Frida
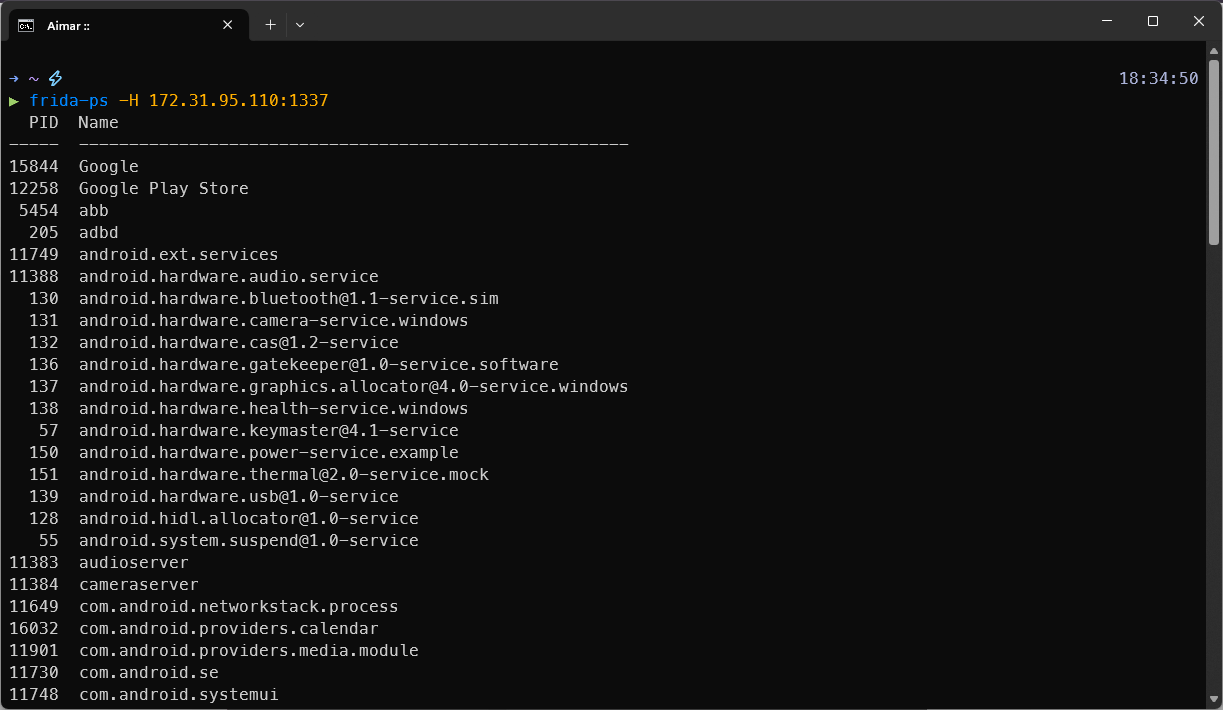
Frida is a dynamic toolkit used by security experts to analyze mobile applications at runtime. As one of the more prominent mobile application pentesting tools, it equips testers with the ability to inspect, intercept, and modify app behavior, making it a very effective dynamic testing tool.
Key Features:
- Scanner Capabilities: Customizable real-time vulnerability assessment.
- Accuracy: High, depending on user expertise.
- Compliance Support: Indirect support through custom analysis.
- App Support: Both Android and iOS.
- Pricing: Open source (Free).
Pros:
- Great for dynamic analysis and runtime testing
- Provides flexibility
Limitations:
- Requires expertise to use effectively
8. Data Theorem
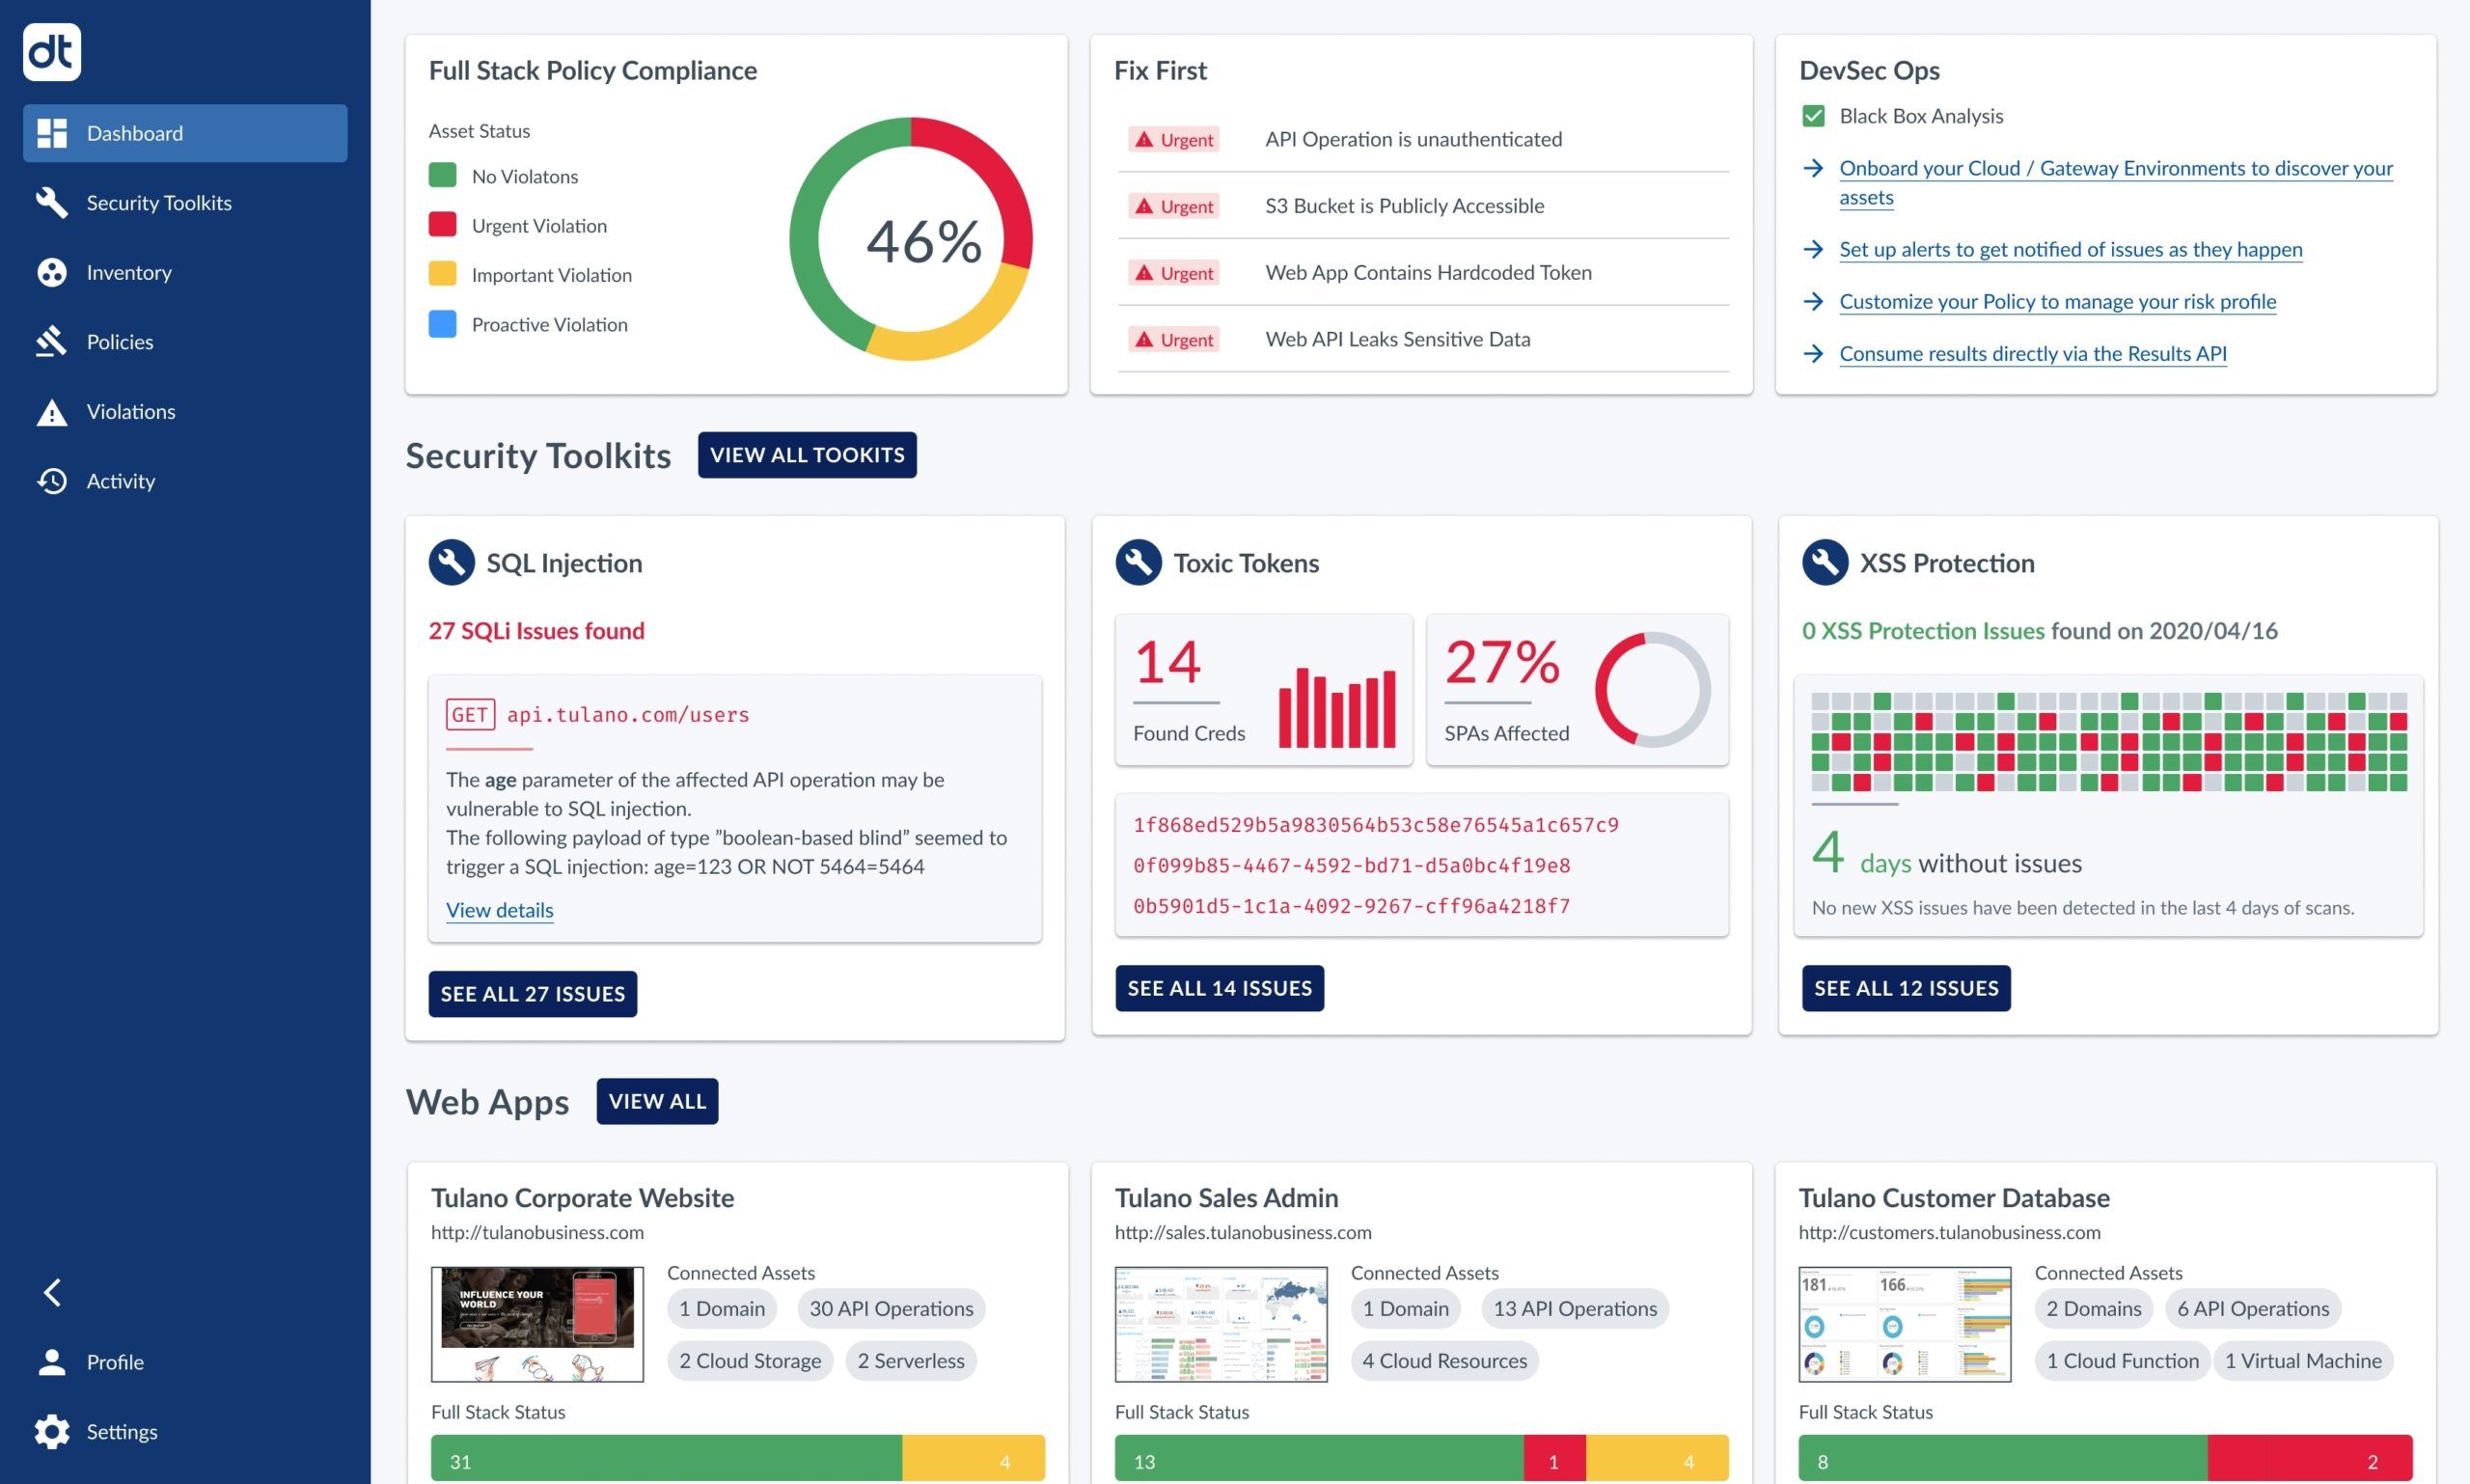
Data Theorem provides automated security and privacy scanning for mobile apps, APIs, and cloud ecosystems. It is a DAST scanner focusing on identifying vulnerabilities in the runtime and helps mitigate potential risks.
Key Features:
- Scanner Capabilities: Automated scans for runtime and API vulnerabilities.
- Accuracy: High with real-time insights.
- Compliance Support: PCI DSS, HIPAA, GDPR, FedRAMP, SOC 2, and ISO 27001.
- App Support: Both Android and iOS.
- Pricing: Custom quote. Pricing is not publicly listed.
Pros:
- Strong focus on runtime and API security
- Real-time monitoring with actionable insights
Limitations:
- Limited manual testing capabilities
9. Drozer
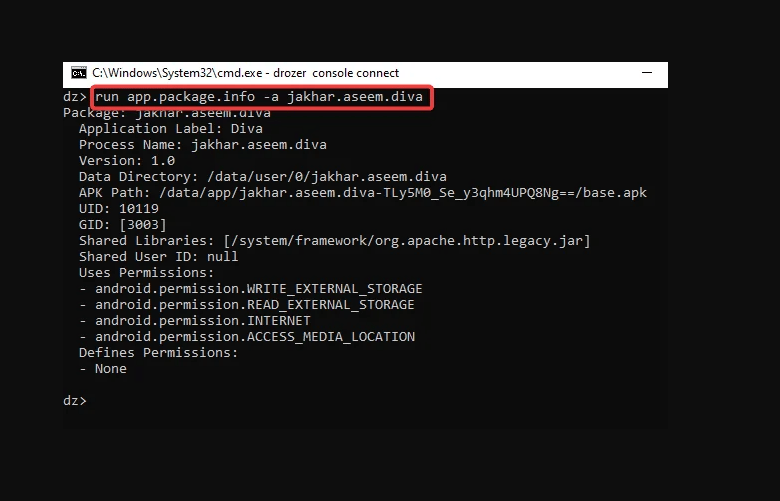
Drozer is a powerful Android security testing toolkit built to identify and exploit application vulnerabilities. It runs comprehensive tests to identify and exploit misconfigurations and issues related to exposed components and permissions.
Key Features:
- Scanner Capabilities: Targeted scans for Android app vulnerabilities.
- Accuracy: High for Android-specific issues.
- Compliance Support: Android-specific security guidelines.
- App Support: Android only.
- Pricing: Open source (Free).
Pros:
- High accuracy with Android security misconfigurations
- One of the free and open-source mobile penetration testing tools
Limitations:
- Limited to Android testing
10. NowSecure
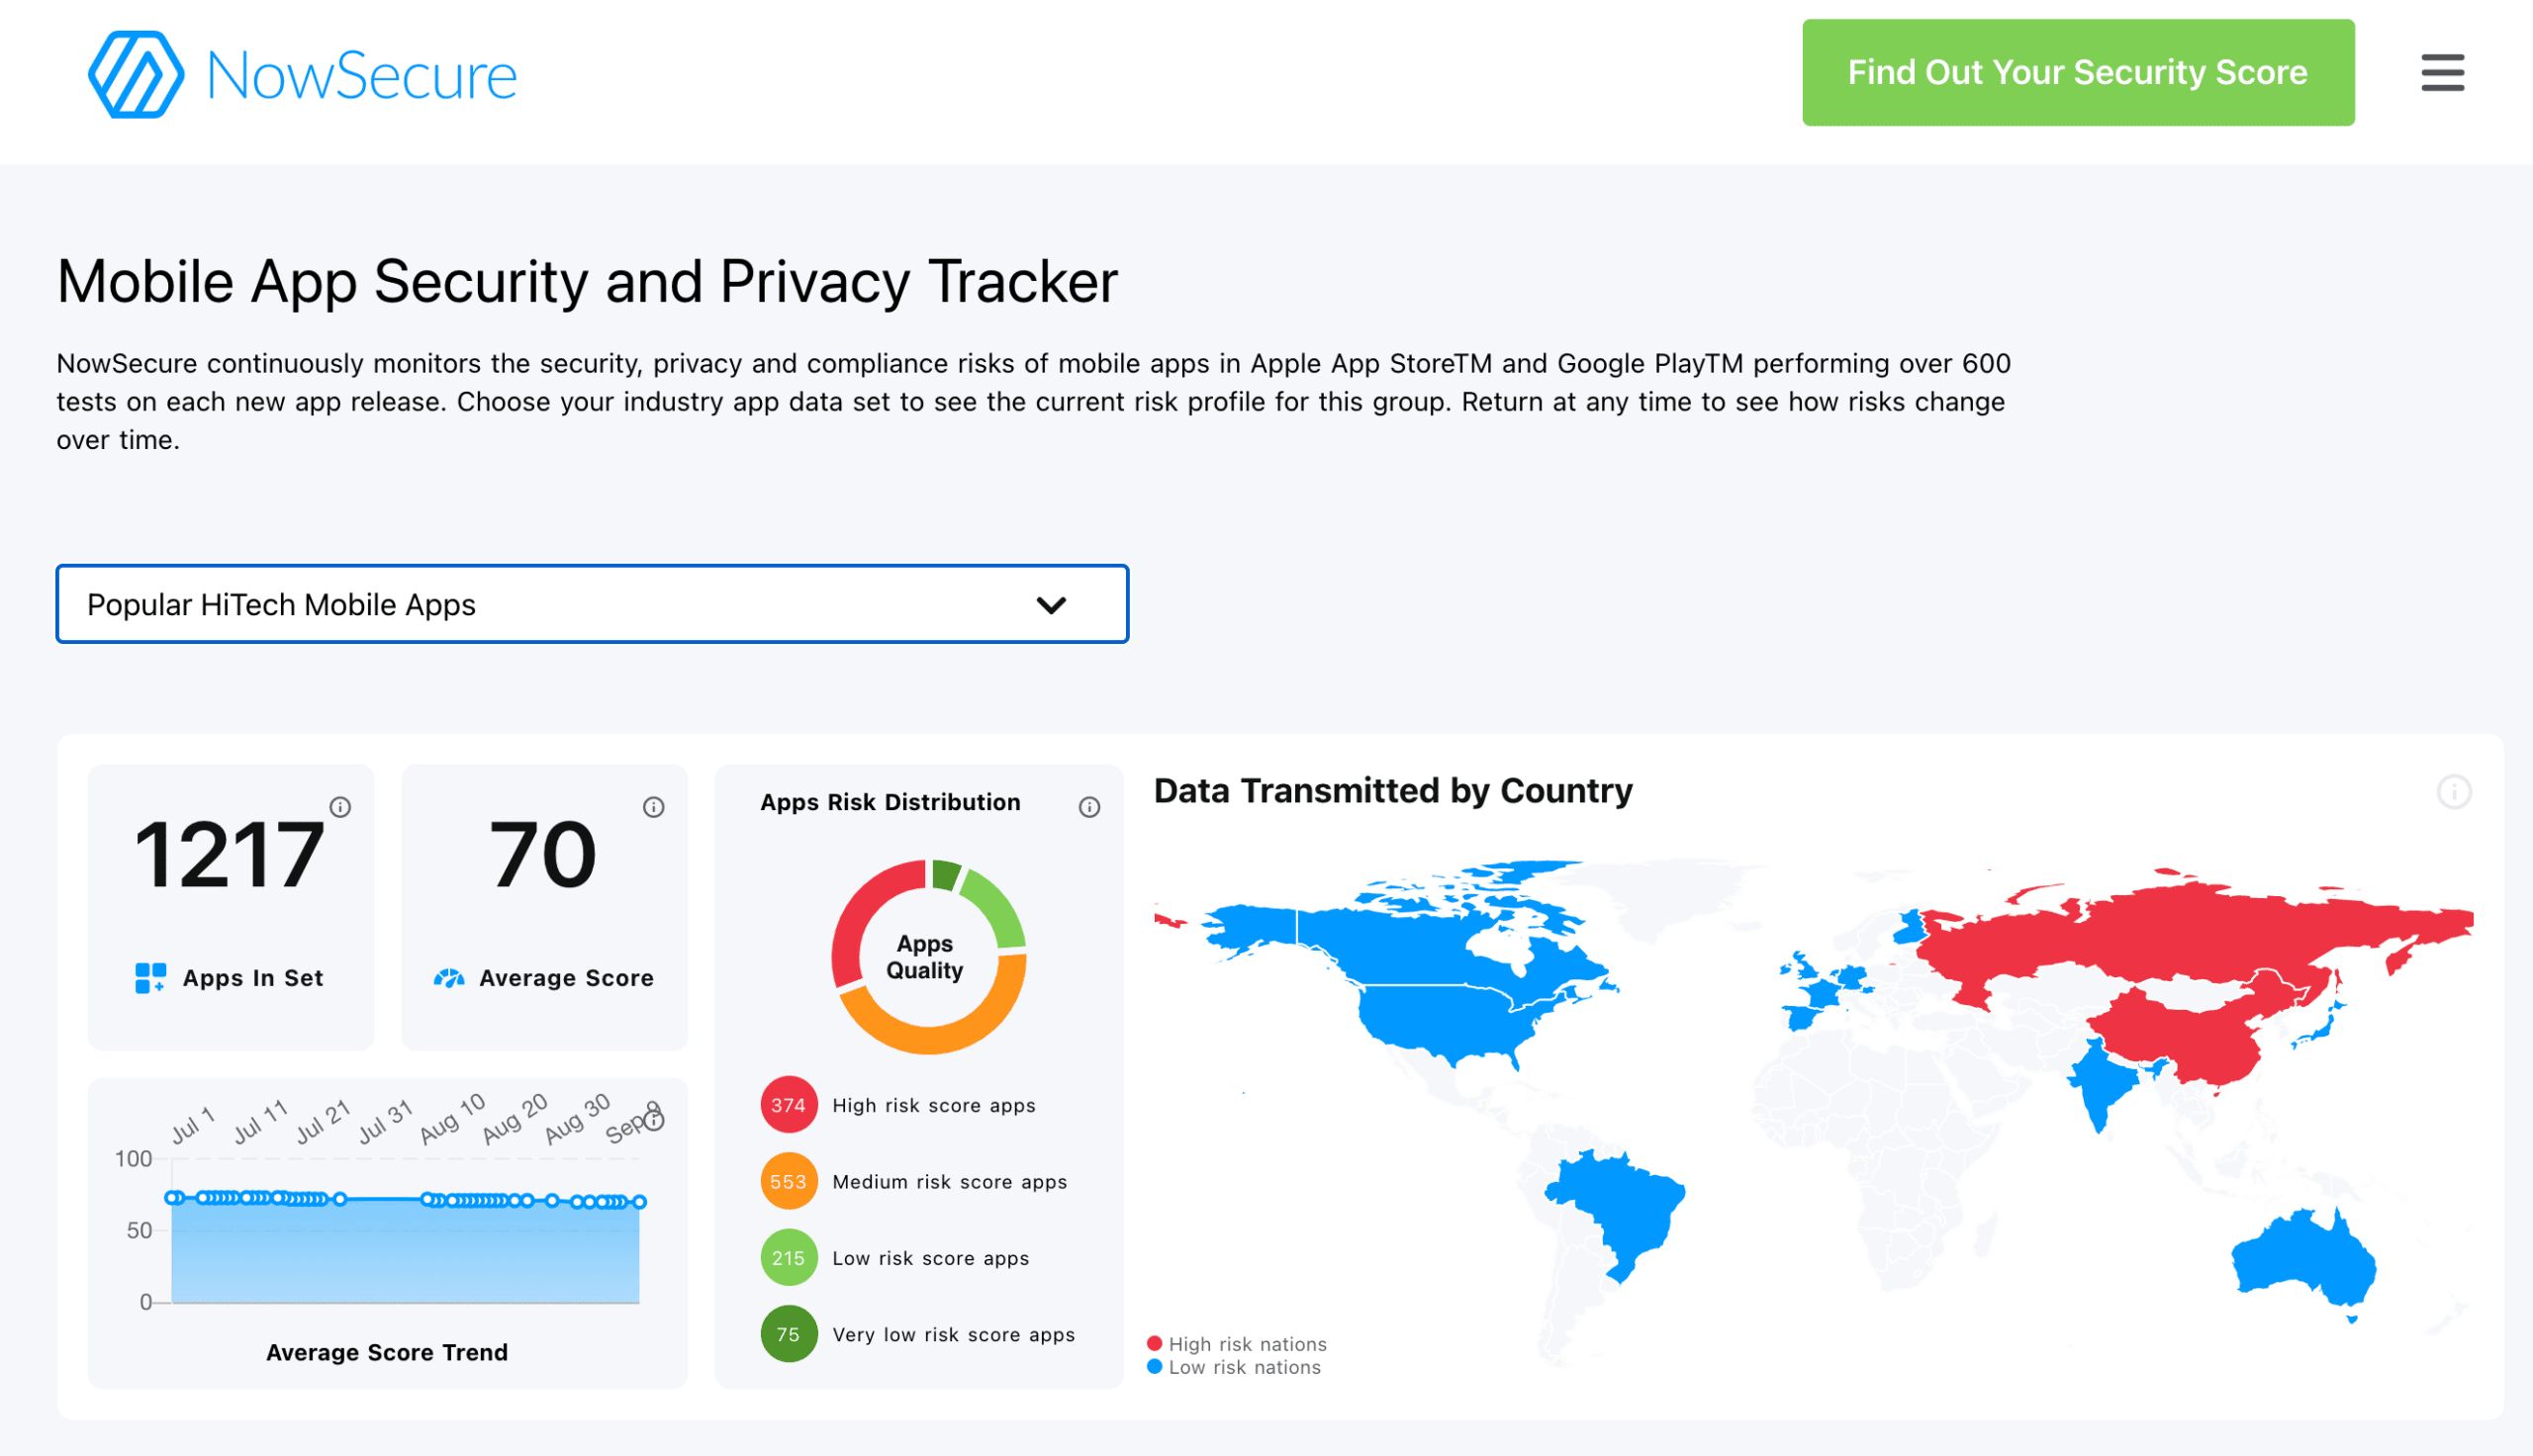
NowSecure is a mobile-first application security testing platform for Android and iOS apps. It combines automated static, dynamic, interactive, API, privacy, and behavioral testing with OWASP MASVS mapping, making it a strong fit for teams that test mobile apps continuously across release pipelines.
Key Features:
- Scanner Capabilities: Automated binary and runtime testing, API analysis, and expert assessments.
- Accuracy: Less than 1% reported false positives.
- Compliance Support: Supports OWASP MASVS and MASTG, ADA MASA, NIAP, PCI DSS, HIPAA, and GDPR-oriented evidence.
- App Support: Both Android and iOS.
- Pricing: Custom quote. Pricing is not publicly listed.
Pros:
- Deep mobile specialization.
- Strong CI/CD coverage for frequent releases.
Limitations:
- Suitable for larger teams.
- Custom pricing, reduced upfront cost clarity.
11. Apktool
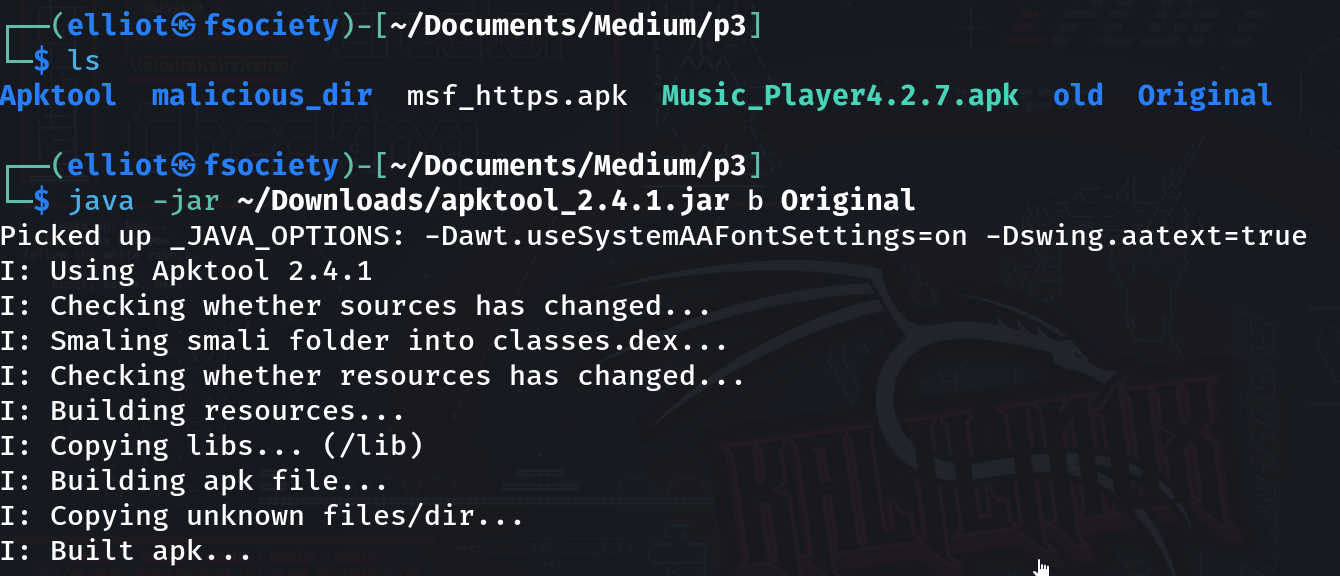
Apktool is an open source reverse engineering tool for android applications designed to decompile APK files and analyzes them for misconfigurations. It is used by security experts mainly to look for structural vulnerabilities and debugging issues in Android applications.
Key Features:
- Scanner Capabilities: Decompile APKs, uncover structural vulnerabilities.
- Accuracy: Manual review required; accuracy depends on expertise.
- Compliance Support: Secure development practices.
- App Support: Both Android and iOS.
- Pricing: Open source (Free).
Pros:
- Great for decompiling and modifying APKs
- It provides a user-friendly command-line interface
Limitations:
- Requires expertise to use the tool effectively
12. Appknox
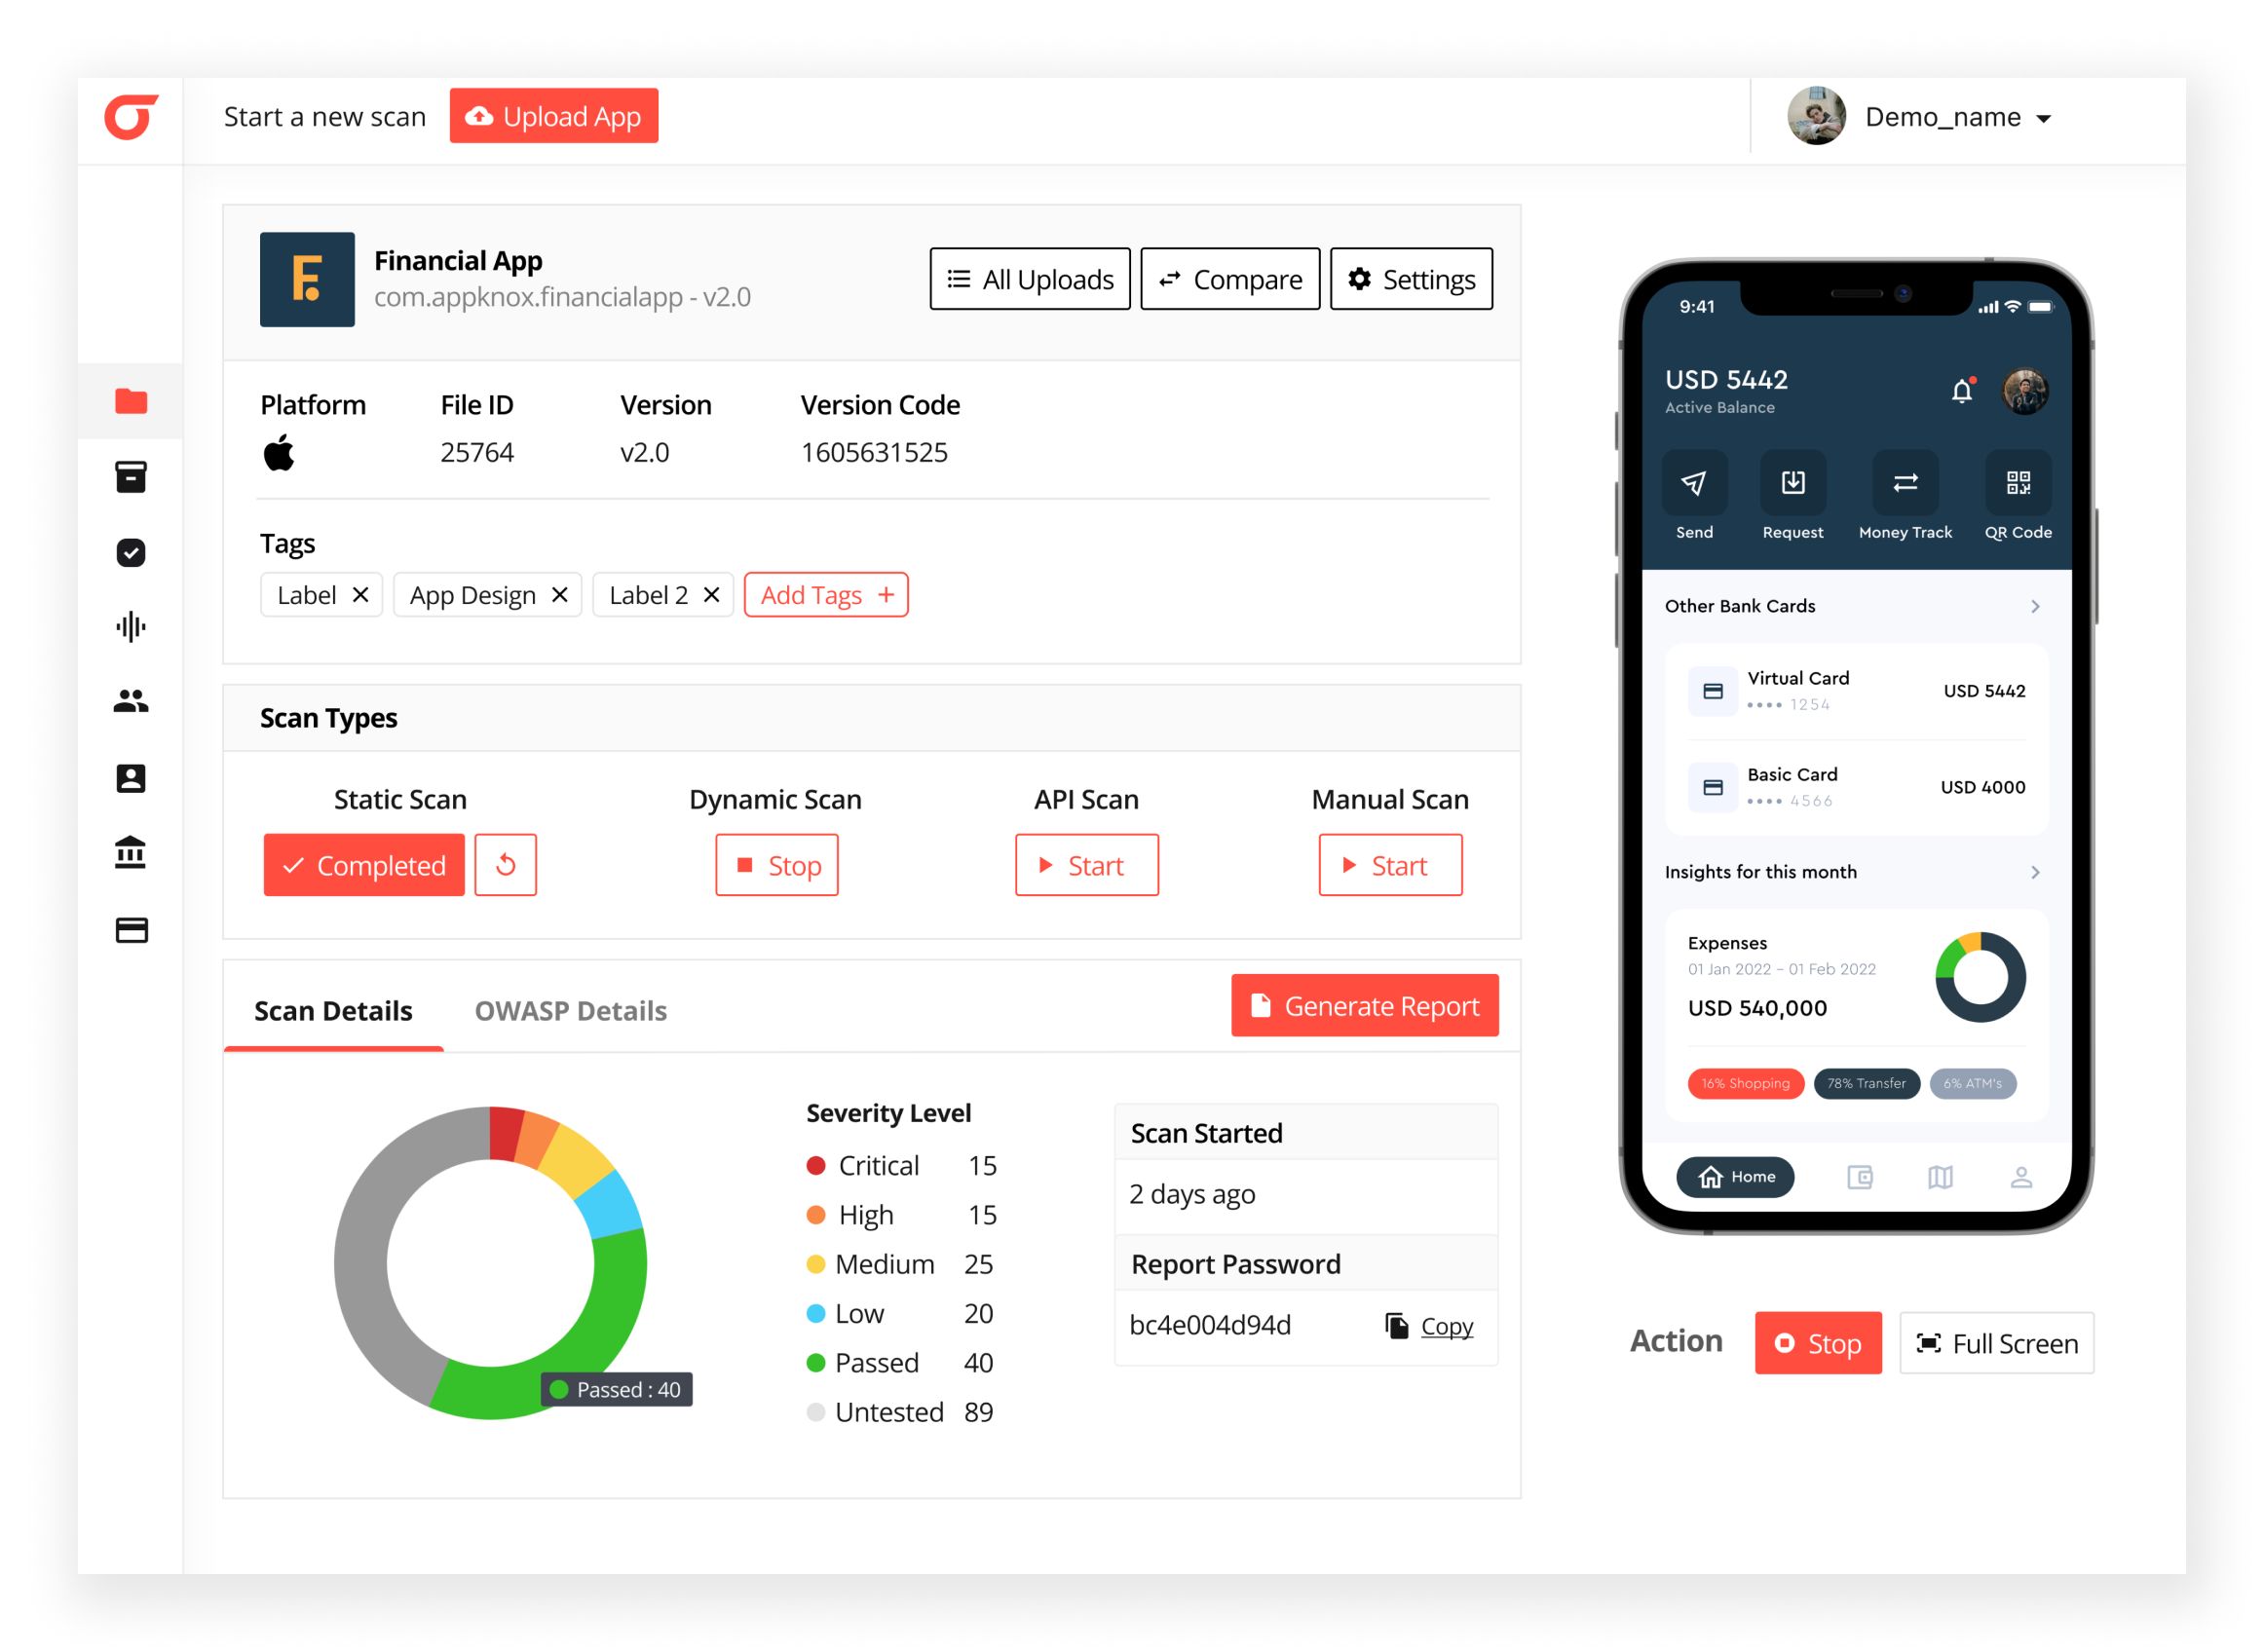
Appknox is a mobile application security testing platform built around binary-based testing, which means it scans the compiled APK, AAB, or IPA that actually ships to users.
Key Features:
- Scanner Capabilities: Binary SAST, DAST on physical devices, API testing, SBOM, app-store monitoring, manual pentesting.
- Accuracy: High when handled by experienced users.
- Compliance Support: Maps evidence to OWASP Mobile Top 10 2024, PCI DSS 4.0, GDPR, HIPAA, NIST, DORA, and SAMA.
- App Support: iOS only.
- Pricing: Custom quote. Pricing is not publicly listed.
Pros:
- Broad mobile-native coverage.
- Useful compliance mapping and CI/CD integration.
Limitations:
- No fixed public price, and add-ons can change total cost.
How To Choose the Best Mobile App Pentesting Tool For You?
Start with your testing gap, not the longest feature list. A comprehensive and appropriate manner of mobile application penetration testing process usually requires more than one technique.
Testing methods
Use SAST for source or binary review, DAST for running-app behavior, proxy tools for API and network traffic, and runtime instrumentation for tampering and control bypasses.
Testing Depth
Android and iOS have different storage, permission, signing, and runtime models. Confirm that each platform is tested separately and that cross-platform frameworks such as Flutter or React Native are supported.
Evidence of findings
Prioritize reproducible findings, proof of concept, remediation guidance, retesting, and traceability to the current OWASP MASVS, MASWE, and MASTG structure.
Secure every release
Astra’s 2026 report found that 22% of organizations tested once and stopped. Choose CI/CD triggers, scheduled checks, or a managed workflow that makes retesting realistic after code changes.
For a practical control list, use this mobile app security checklist. For budgeting, compare tool licensing with the wider cost of penetration testing and the internal time needed to operate and validate each tool.
Final Thoughts
Mobile app penetration testing tools are not just an investment but a necessity to create a secure environment for the users of the application and their data. Using the right combination of tools enables you to adopt a proactive approach and detect vulnerabilities before attackers can exploit them.
Choosing solutions that align with your application needs, provide seamless integrations, and have top features like compliance reporting can significantly help reduce risks and strengthen your defense policies.
FAQs
1. What are the best tools for mobile app penetration testing in 2026?
Astra Security is the best overall option for managed mobile pentesting with expert validation. NowSecure and Appknox are strong mobile-first platforms for automated test at scale. Burp Suite Professional, MobSF, Frida, ZAP, Drozer, and Apktool are useful hands-on tools for specific parts of a mobile assessment.
2. How much does penetration testing cost?
The cost of mobile penetration testing depends on the scope of the test, along with some other factors. Hence, it is difficult to provide a definitive figure. It can cost anywhere from $2,000 – $10,000.
3. How often should mobile apps be penetration tested?
Test before major releases, after sensitive feature changes, after authentication or payment-flow changes, and at least annually for compliance. High-change apps should add CI/CD checks and periodic expert-led assessments.